Escape - Application Security & Offensive Security Blog
Explore practical offensive and application security insights covering web application testing, emerging AI cybersecurity research, API and GraphQL security, and advanced testing techniques.

Filters
GraphQL
Introducing Seamless GraphQL Compliance
As your go-to partner in GraphQL Security, we at Escape are constantly innovating to simplify and streamline security for you. We're proud of our reputation for crafting modern, dynamic application security testing (DAST) tools tailored to GraphQL, beloved by developers and trusted by security teams worldwide. From comprehensive
3 min read
GraphQL Vulnerability
GraphQL XSS: Cross-Site Scripting Explained
Every Monday morning, you go through your ritual and check the users' feedback. This week, despite all the wonderful feedback, some users are complaining that someone has impersonated them and performed actions on their accounts without their knowledge.
After some investigation, you discover that all the complaining users have
5 min read
GraphQL
GraphQL Input Validation & Sanitization
Why input validation and sanitization are important in GraphQL?
GraphQL allows you to identify the data and validate inputs based on type information. By default, GraphQL Specification has the Int, Float, String, Boolean and ID Scalar types. But as a conscious API developer, you've probably come across situations
5 min read
Say Hi to SecureGPT: The free Security Tool for ChatGPT Developers
👋 tl;dr Are you a ChatGPT plugin developer who wants to ensure the safety and security of your creations? Look no further. Escape is thrilled to announce the release of SecureGPT, a lightning-fast and free security tool designed specifically for ChatGPT plugins. Secure your ChatGPT plugins in seconds with SecureGPT
2 min read
GraphQL
Top 5 GraphQL vulnerabilities burdening HIPAA compliance
TL;DR: GraphQL vulnerabilities will inevitably burden organizations, especially when healthcare compliances like HIPAA come into play. This article highlights how Escape makes it super easy to release compliant APIs.
The correlation between HIPAA and GraphQL is that PHI resources can be exposed through GraphQL APIs, allowing for a more
5 min read
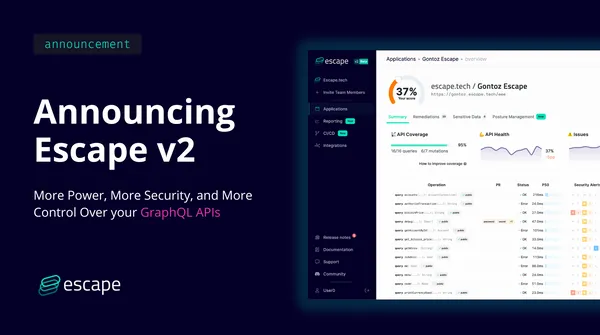
Introducing Escape v2: More Power, More Security, and More Control Over Your GraphQL APIs
tl;dr we are releasing the biggest update of our GraphQL Security platform so far. It includes numerous new features, including API Posture management, Reporting Overview, Better CI/CD Integration, GitHub SSO, and OWASP API Top 10 2023 Support.
Hello, Escape community! We are thrilled to announce the release of
3 min read
GraphQL Vulnerability
Demystifying GraphQL Security: A Comprehensive Guide to GraphQL Introspection
Whether or not to disable introspection in GraphQL has been a common debate among GraphQL developers since its inception. In this blog post, we will explain why completely disabling GraphQL introspection is not necessary and why it can be counterproductive.
I can't really find any good reasons for
5 min read
Research
The State of Public APIs 2023
tl;dr we scanned 6056+ public APIs on the internet with our in-house feedback driven exploration tech and ranked them using security, performance, reliability, and design criteria. We decided to analyze the resulting data and produce a full featured report: The State of Public APIs 2023
Why build this report?
2 min read
The EU’s PSD2: API Security and Financial Services
In 2015, the European Union adopted the Revised Payment Services Directive (PSD2). This legislative framework aimed to fix the financial services market, which was disrupted by the arrival of new innovative players.
The 2010s gave birth to numerous FinTech startups providing new services in addition to traditional banking institutions. These
5 min read
Announcement
APIRank.dev: we scanned and ranked 6031+ public APIs on the internet
tl;dr we scanned 6031+ public APIs on the internet with our in-house feedback driven exploration tech and ranked them using security, performance, reliability, and design criteria. The results are public on APIrank.dev. You can also request to index your own API for free and see how it compares
3 min read
Introducing API Security Posture Management for GraphQL
tl;dr The Escape Team is excited to announce the release of its latest feature, API Security Posture Management for GraphQL. This feature proposes a single API Catalog view to explore the security, integrity, and performance of all GraphQL operations in one place. See it for yourself in action
With
2 min read
Introducing OpenAPI.Security, a free tool to quickly check the security of REST APIs
tl;dr We released OpenAPI.security, an online tool that performs a dozen of security tests on any given OpenAPI/Swagger-based API, with no signup or email required
Our team at Escape is mainly focused on securing GraphQL APIs. For this, we developed a new approach called feedback-driven API exploration,
1 min read
Escape is proud to be backed by Y Combinator!
Escape is proud to announce that we are backed by Y Combinator, the world's most prestigious and well-known startup accelerator, joining the YC Winter 23 batch!
Y Combinator, known for investing in and mentoring early-stage startups, has an impressive portfolio of successful companies such as Airbnb, Dropbox, and
2 min read
GraphQL Vulnerability
The 8 Most Common GraphQL Vulnerabilities (and How to Fix Them)
We at Escape have been scanning GraphQL APIs for vulnerabilities for more than two years. In this post, we will share the most common GraphQL vulnerabilities, affecting close to all GraphQL APIs we have scanned. We strongly recommend you check your GraphQL APIs for these vulnerabilities.
4 min read
How to set up modern design system using Storybook and Figma
As our product expands, and so does our team, we need to have a better workflow. By basing themselves on a single source of truth, designers and developers speak the same language, and everyone can then focus on the essential: the user experience. This source of truth is called the
5 min read
Postman
Find & Fix GraphQL API Security Issues with Postman
Improve the security of your GraphQL API with Escape and Postman
Are you tired of dealing with pesky API vulnerabilities? Want to take your GraphQL game to the next level? Introducing the perfect combo for GraphQL success - Escape and Postman.
Escape is a tool that helps developers automatically and
3 min read


Feedback Driven API exploration at the service of GraphQL Security
Introduction
Automating the audit of APIs is a very hard problem: we want to dynamically evaluate those APIs' security, performance, and reliability.
But APIs take parameters that are tightly coupled to the underlying business logic. We need a way to know what sequences of requests to send, with what
Migrating from Vue 2 to Svelte
After using Vue 2 as our front-end framework for almost two years, it was announced that this support would no longer be maintained, so we decided to migrate to a new framework. But which one to choose: Vue 3 or Svelte?
Please note that our goals after the migration were
7 min read
Achieving end-to-end type safety in a modern JS GraphQL stack – Part 2
Welcome back! This article is the second and last part of the Achieving end-to-end type safety in a modern JS GraphQL stack series. Read the first part if you haven't yet!
Svelte
I won't go into the details of why Svelte, but I like Svelte a
5 min read
Achieving end-to-end type safety in a modern JS GraphQL stack – Part 1
In this article, we will create a simple GraphQL application, a message board, by combining many recent open-source technologies. This article aims to be a showcase of technologies that work well together rather than a complete tutorial on project setup. It is however a long read, so we decided to
7 min read
Don’t let your vulnerabilities escape.
Ready to multiply your force, not just noise?
Book a demo
Book a demo