Escape - Application Security & Offensive Security Blog
Explore practical offensive and application security insights covering web application testing, emerging AI cybersecurity research, API and GraphQL security, and advanced testing techniques.

Filters
Webinar
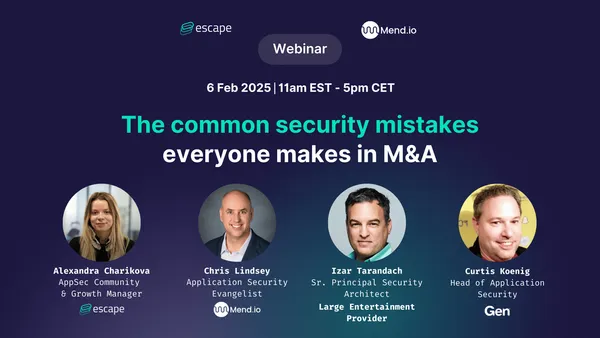
Webinar: The security mistakes everyone makes in M&A
If you often manage security across diverse brands or handle mergers and acquisitions, this webinar is not to be missed, as a panel of guest experts take you through all of the real-world security pitfalls when bringing companies together.
2 min read
Product updates
Kickstart 2025 with New DAST Scanner Features
The start of a new year brings exciting updates to our DAST scanner!
Our goal is simple: to improve testing accuracy by leveraging real, concrete examples of API requests when they might be required. While we don’t need to have direct access to live traffic to start in-depth testing,
4 min read
Product updates
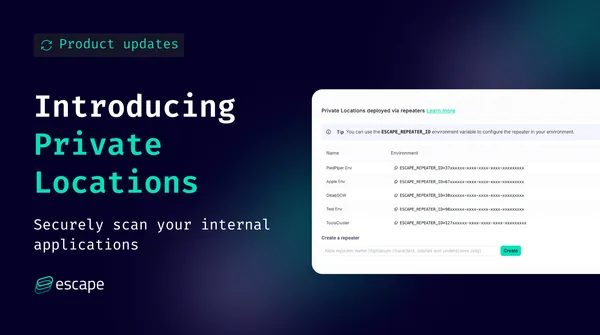
Introducing Private Locations: Securely Scan Your Internal Applications
While public applications often receive focused attention, the reality is that many critical applications operate behind firewalls, VPNs, or in private networks. These internal apps can be just as vulnerable to attacks—but securing them without disrupting your infrastructure can be a challenge.
Today, we’re introducing Private Locations, a
3 min read
Research
Fortune 1000 at risk: How we discovered 30k exposed APIs & 100k API vulnerabilities in the world’s largest organizations
Hey there!
Next week, social media will be flooded with Thanksgiving feasts (and Black Friday deals). But before you dive into the holiday shopping madness, the Escape team has prepared a special treat for you—not a Black Friday deal on Escape, of course, but rather some impressive findings on

6 min read
API Security
API Security Day - powered by APIDays & Escape
Are you ready to dive deep into API security? Join Escape's team for a focused, one-day event at the APIDays Paris. Learn from industry leaders and discover the latest strategies and technologies to protect your APIs. Whether you're a cybersecurity professional, API developer, or API architect,
2 min read
Application Security
The Schedule is Live: The Elephant in AppSec Conference
The Elephant in AppSec Conference agenda is live! It’s packed with sessions that dive into what’s broken in AppSec, how to fix it, and unique insights from top experts on the latest AppSec tooling.
Prepare for bold opinions and fresh perspectives, where the best in Application Security come
2 min read
API Security
Forrester's CISO Budget Planning Guide for 2025: Prioritize API Security
As we head into 2025, planning a robust security budget is more critical than ever. According to Forrester's latest Budget Planning Guide for Security and Risk Leaders, one element stands out as indispensable: API security.
APIs form the backbone of modern digital interactions, connecting services, platforms, and users.
10 min read
Compliance
How API Security Fits into DORA Compliance: Everything You Need to Know
With over 22,000 financial institutions and IT service providers now affected, the Digital Operational Resilience Act (DORA) represents an important shift in cybersecurity for the EU’s financial sector.
DORA forces tighter collaboration between regulators, financial institutions, and third-party vendors. It’s not just about protecting internal systems anymore
7 min read
Don’t let your vulnerabilities escape.
Ready to multiply your force, not just noise?
Book a demo
Book a demo