
Secure apps and data while meeting PCI DSS & DORA standards
Banks, payment providers and fintechs run pentests on a regulator's calendar and ship on an engineering one. Escape closes that gap with continuous AI pentests across your apps and APIs, evidence mapped to PCI DSS and DORA you report against, and reports built for your assessor.


The annual pentest is a project, not a test

Gain full visibility and protect customer data in minutes
Business logic testing, across roles and multi-step flows
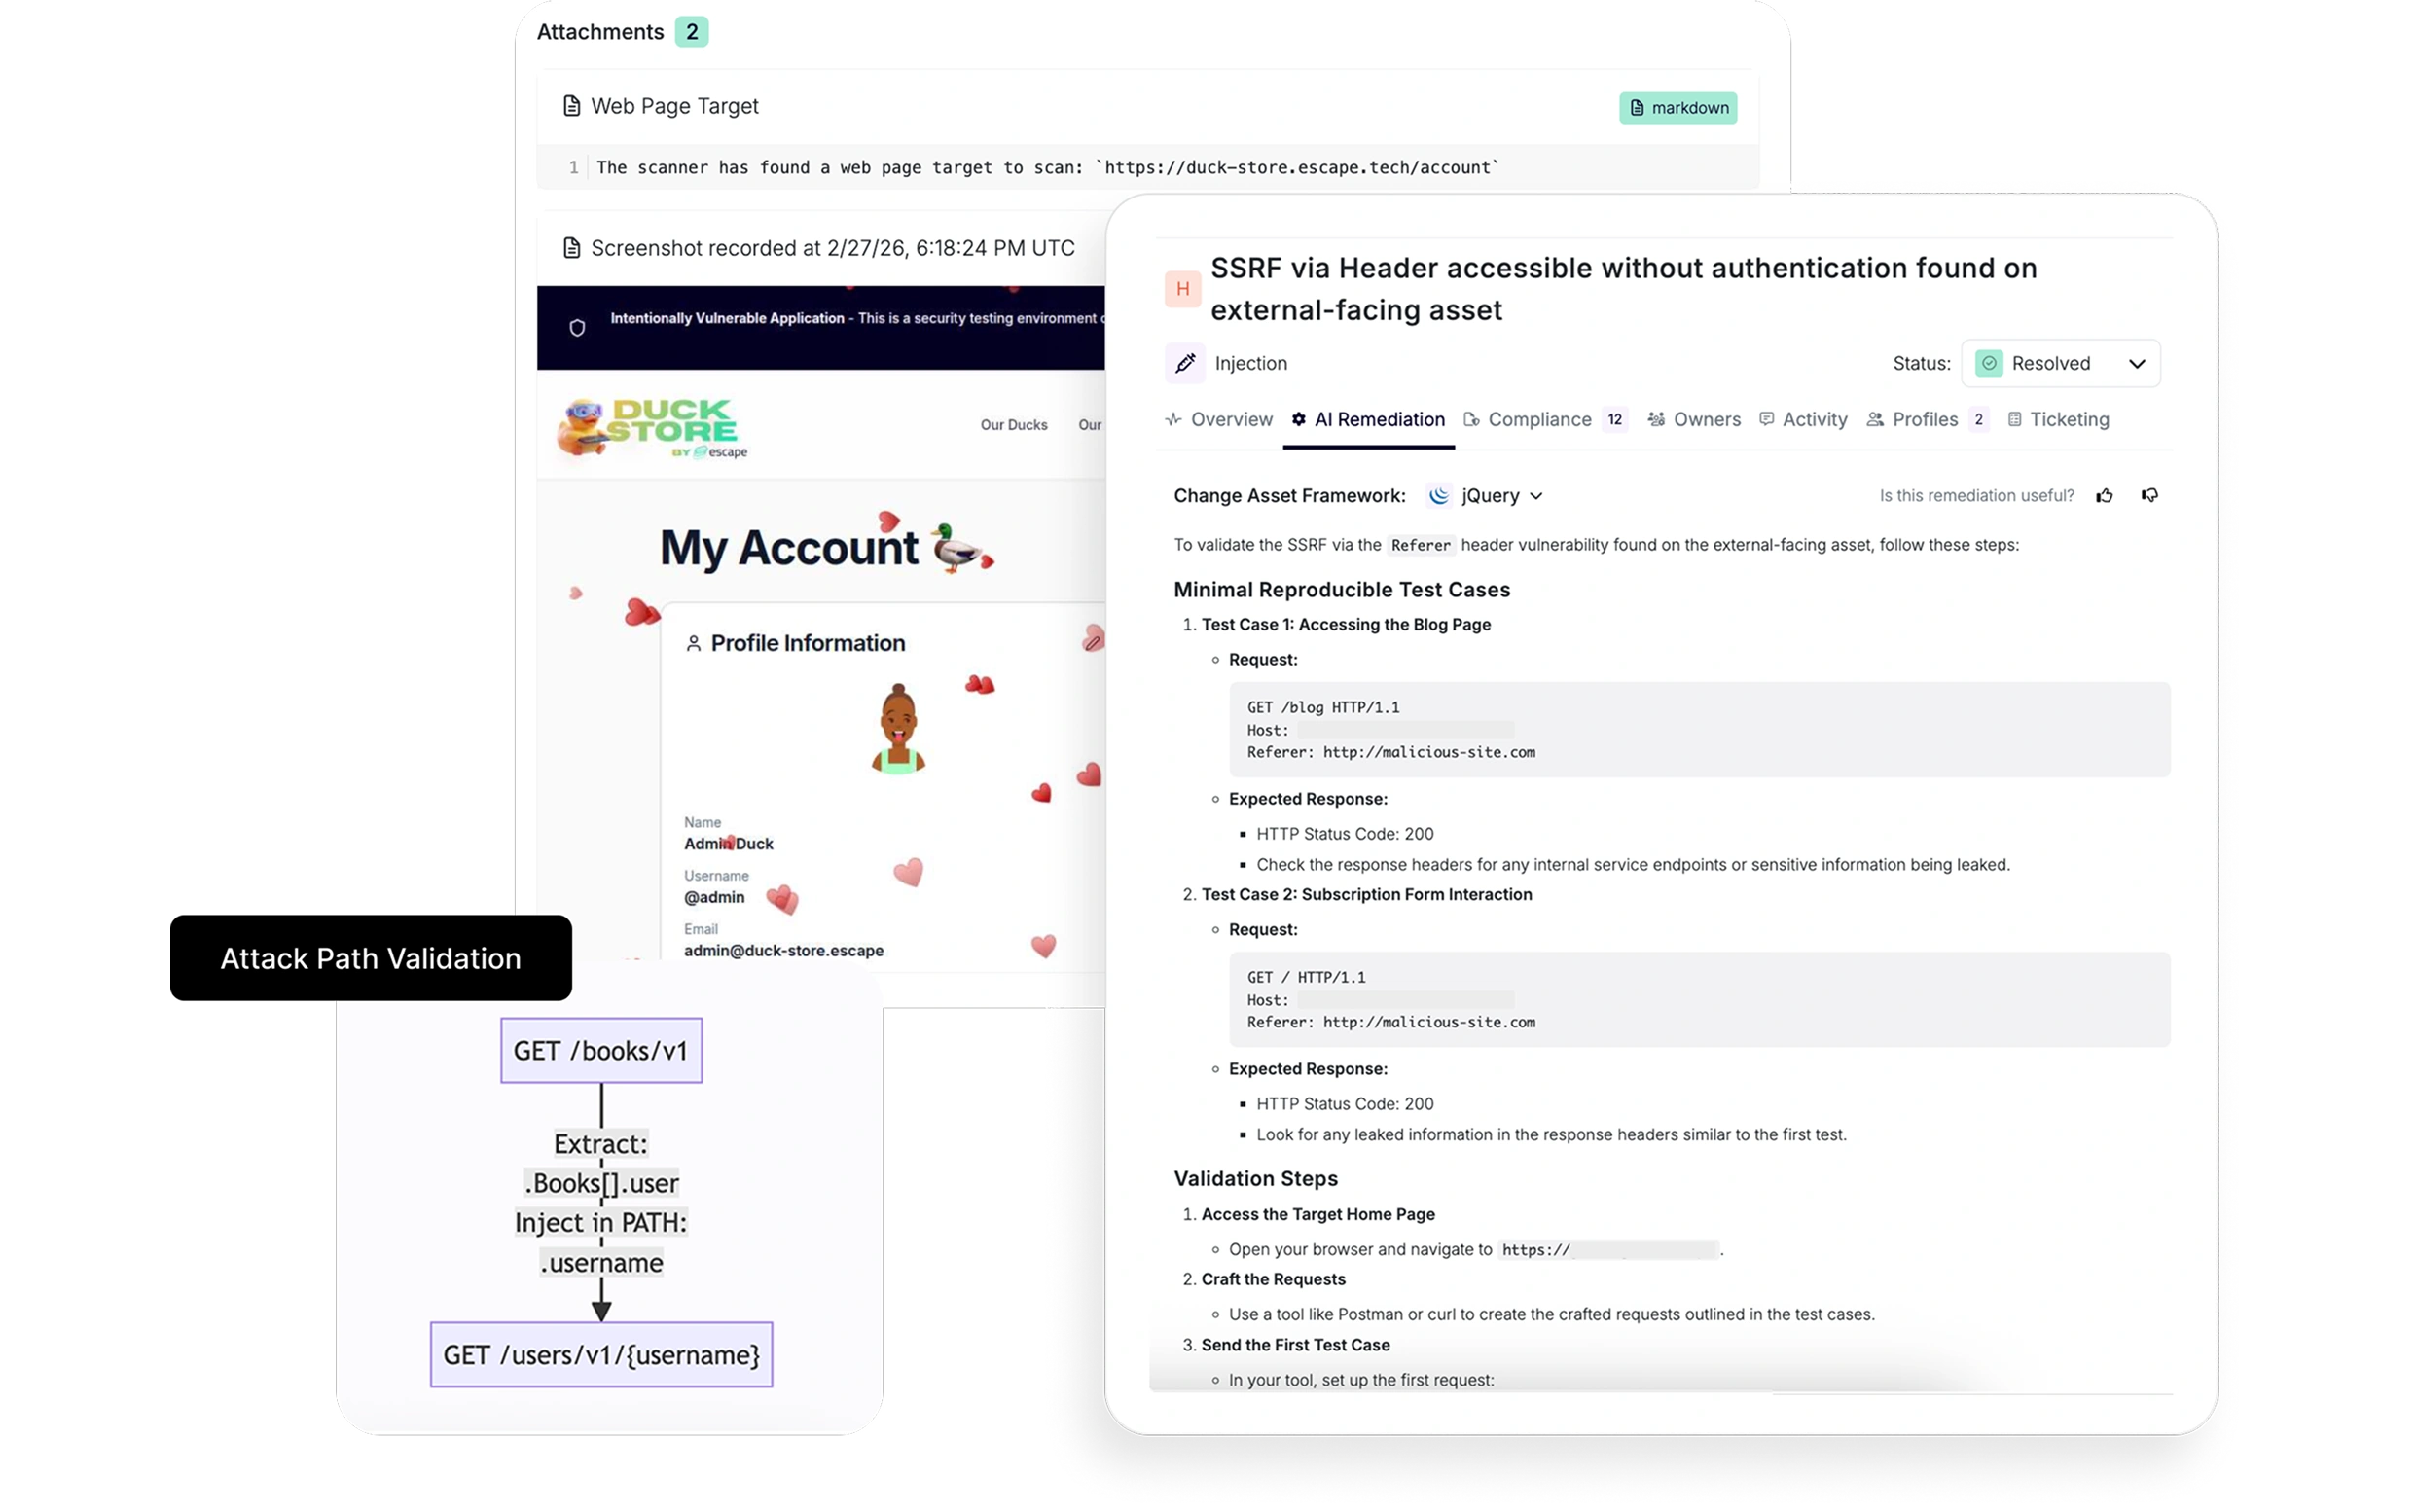
Compliance coverage mapped per framework, not bolted on after

Test on the change, not on the certification date
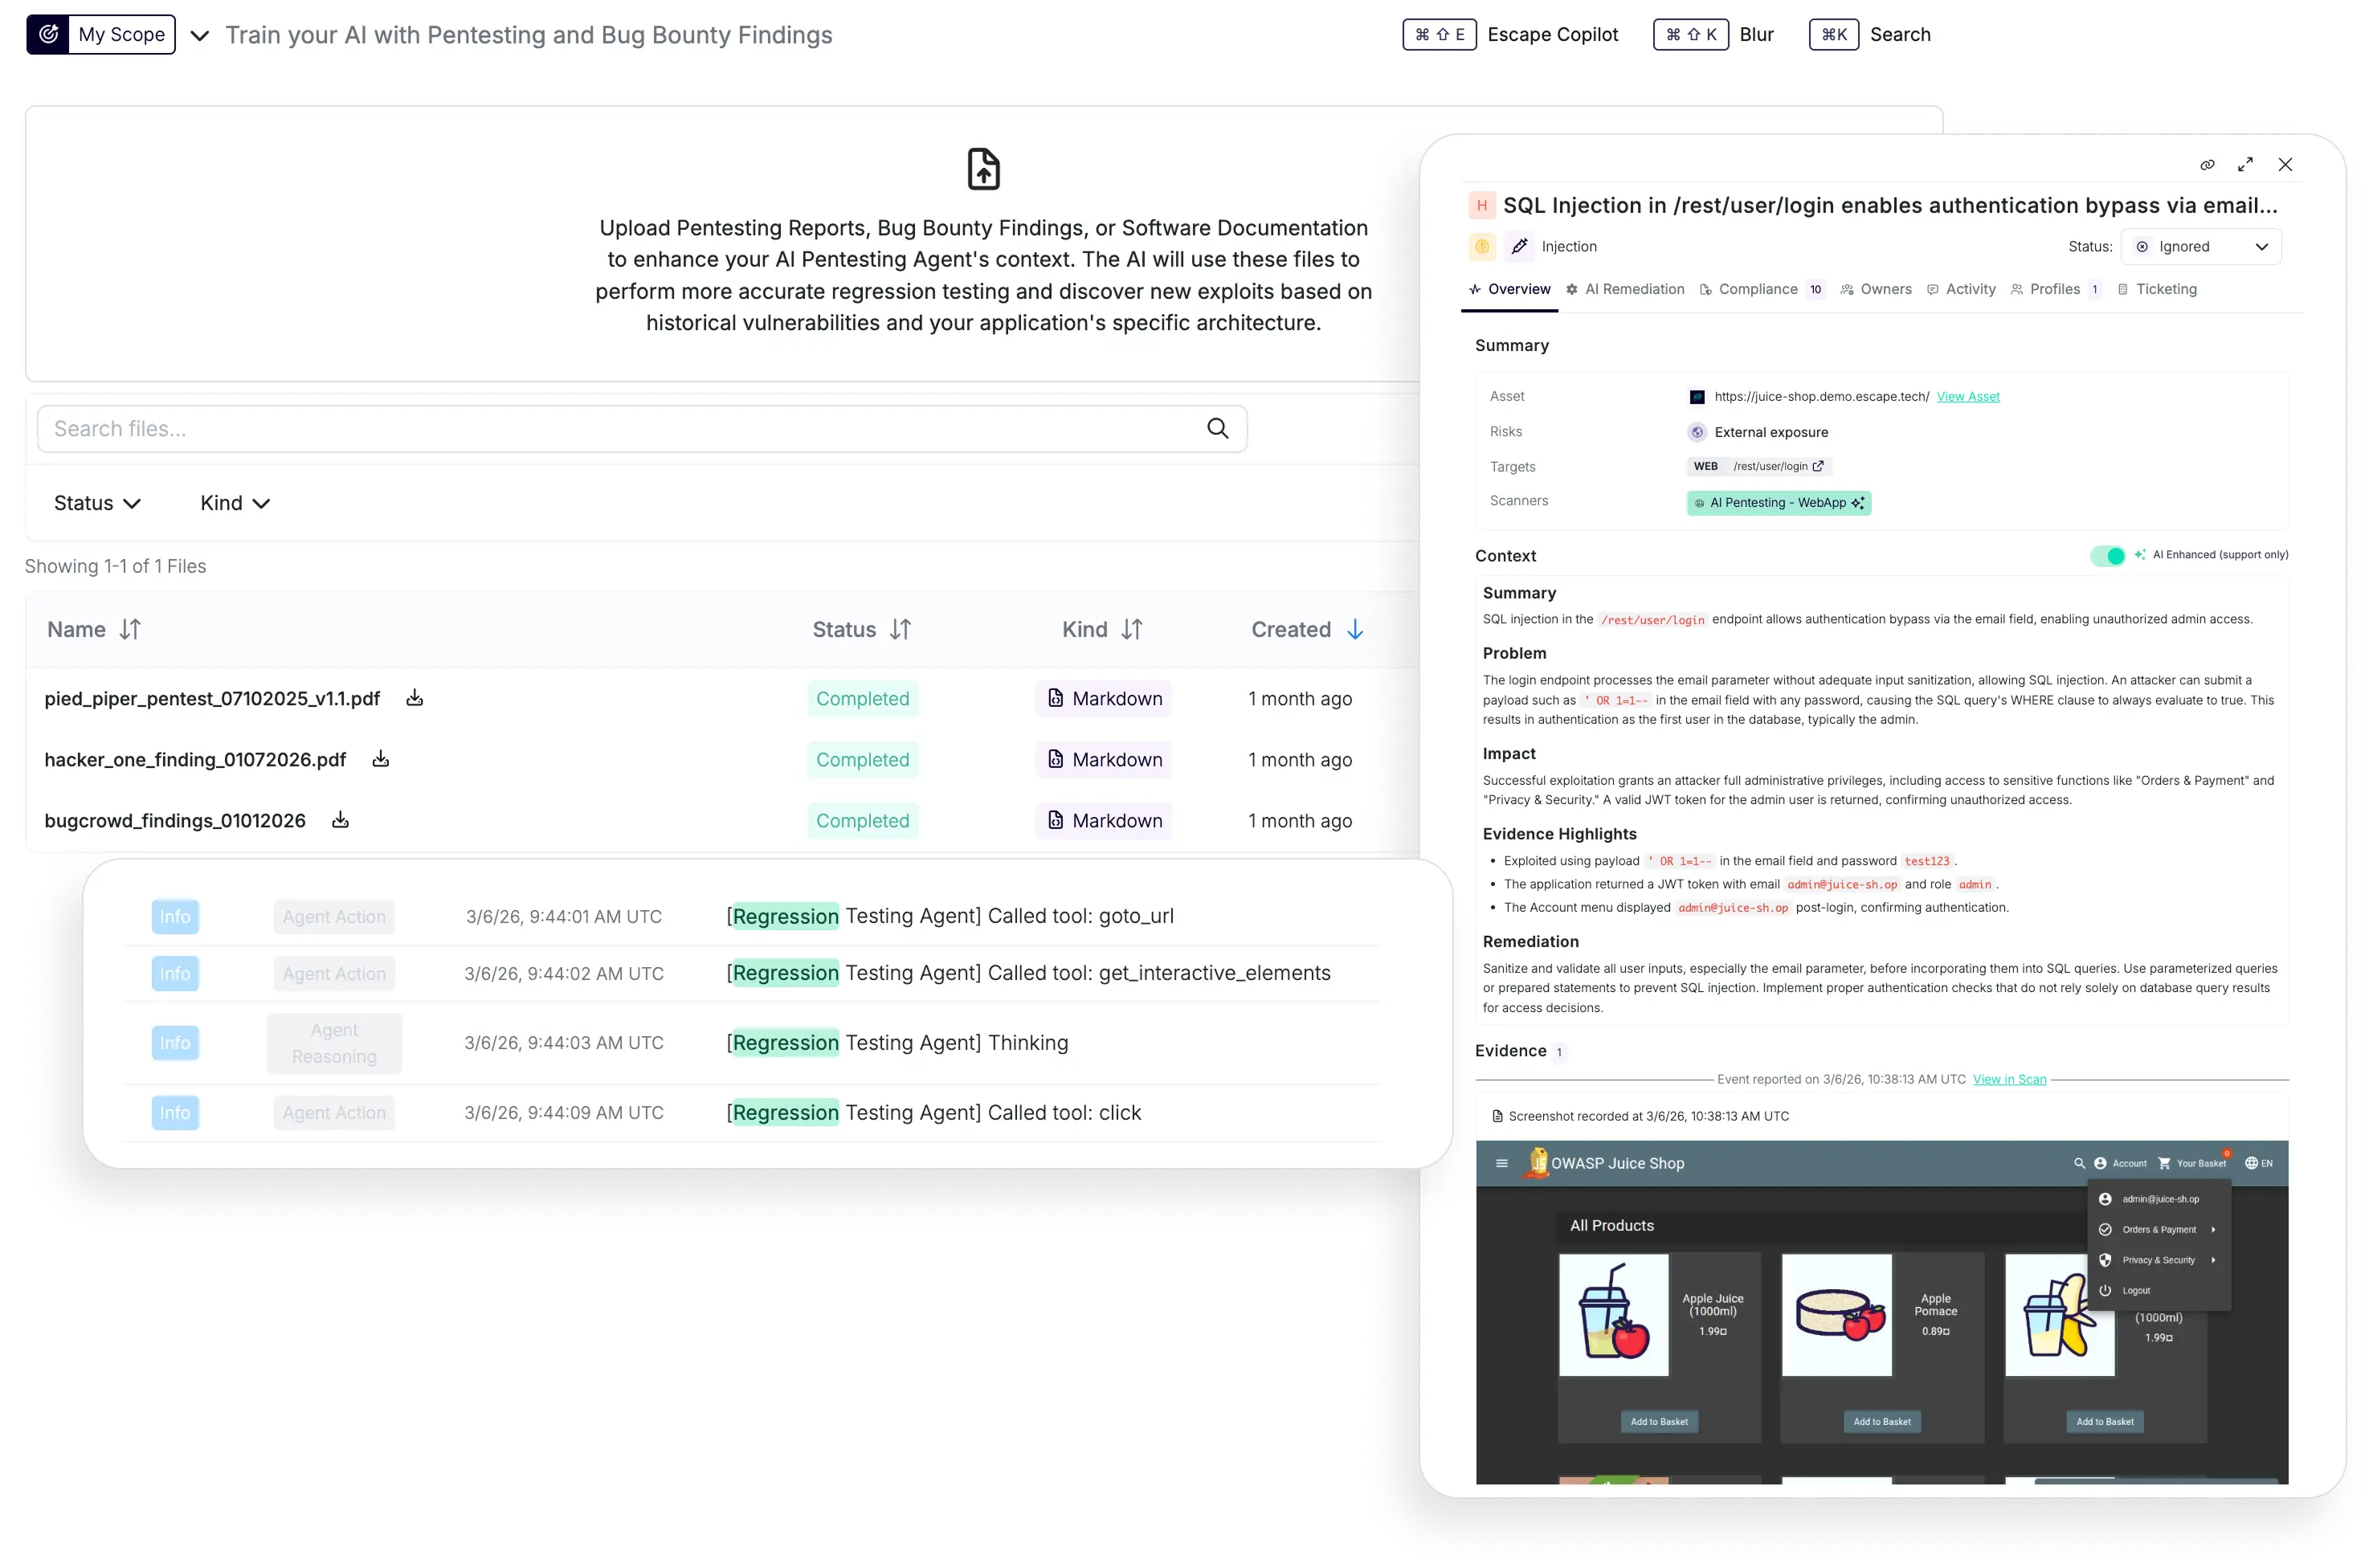
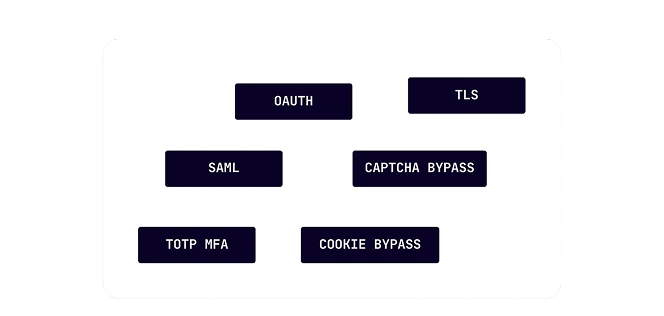
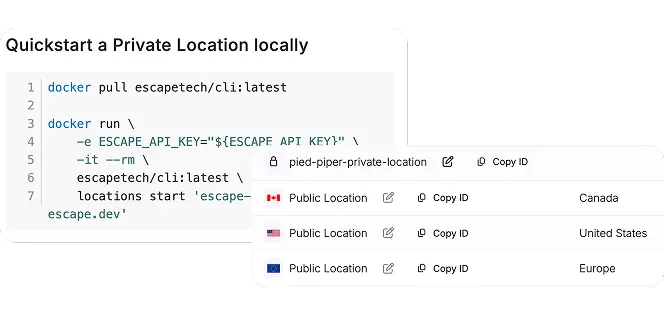
The details that separate a real offensive security program in financial services


Talk to us about your timing
Don't take our word for it
Product Security Engineer
FAQ: What security teams in financial services ask us
Will our auditor accept an AI pentest report?
Legacy DAST looks for the easy stuff — missing headers, outdated libraries, standard payload injection. Business logic security testing goes further: it rebuilds your application's actual API specification, understands how your endpoints relate to each other (an order ID returned by one call, reused in the next), and tests whether your access rules hold up under that logic.
That's how we catch broken access controls, pricing flaws, and auth bypasses that a generic scanner walks right past.
Does it satisfy our pentest requirement for PCI DSS or DORA?
Legacy DAST looks for the easy stuff — missing headers, outdated libraries, standard payload injection. Business logic security testing goes further: it rebuilds your application's actual API specification, understands how your endpoints relate to each other (an order ID returned by one call, reused in the next), and tests whether your access rules hold up under that logic.
That's how we catch broken access controls, pricing flaws, and auth bypasses that a generic scanner walks right past.
What compliance standards does Escape help with?
Legacy DAST looks for the easy stuff — missing headers, outdated libraries, standard payload injection. Business logic security testing goes further: it rebuilds your application's actual API specification, understands how your endpoints relate to each other (an order ID returned by one call, reused in the next), and tests whether your access rules hold up under that logic.
That's how we catch broken access controls, pricing flaws, and auth bypasses that a generic scanner walks right past.
Does it cover the network and segmentation testing PCI DSS requires?
Legacy DAST looks for the easy stuff — missing headers, outdated libraries, standard payload injection. Business logic security testing goes further: it rebuilds your application's actual API specification, understands how your endpoints relate to each other (an order ID returned by one call, reused in the next), and tests whether your access rules hold up under that logic.
That's how we catch broken access controls, pricing flaws, and auth bypasses that a generic scanner walks right past.
Where is our data processed, and do you train on it?
Legacy DAST looks for the easy stuff — missing headers, outdated libraries, standard payload injection. Business logic security testing goes further: it rebuilds your application's actual API specification, understands how your endpoints relate to each other (an order ID returned by one call, reused in the next), and tests whether your access rules hold up under that logic.
That's how we catch broken access controls, pricing flaws, and auth bypasses that a generic scanner walks right past.
Is it safe to run against a production payment flow?
Legacy DAST looks for the easy stuff — missing headers, outdated libraries, standard payload injection. Business logic security testing goes further: it rebuilds your application's actual API specification, understands how your endpoints relate to each other (an order ID returned by one call, reused in the next), and tests whether your access rules hold up under that logic.
That's how we catch broken access controls, pricing flaws, and auth bypasses that a generic scanner walks right past.
Will it reduce what we pay out in bug bounty?
Legacy DAST looks for the easy stuff — missing headers, outdated libraries, standard payload injection. Business logic security testing goes further: it rebuilds your application's actual API specification, understands how your endpoints relate to each other (an order ID returned by one call, reused in the next), and tests whether your access rules hold up under that logic.
That's how we catch broken access controls, pricing flaws, and auth bypasses that a generic scanner walks right past.
How do you keep false positives down?
Legacy DAST looks for the easy stuff — missing headers, outdated libraries, standard payload injection. Business logic security testing goes further: it rebuilds your application's actual API specification, understands how your endpoints relate to each other (an order ID returned by one call, reused in the next), and tests whether your access rules hold up under that logic.
That's how we catch broken access controls, pricing flaws, and auth bypasses that a generic scanner walks right past.