
You are outnumbered. Work like you are not.
Escape runs the offensive security work that repeats: authenticated testing across every role, on every release, with the attack path proven and the fix written for the framework your developers use. What is left is the work that actually needed you.


Legacy scanners and manual processes were never going to work
by developers
creates more work
never gets started
The deep testing you are actually good at, chaining logic flaws across a real workflow, keeps moving to next quarter.

What changes for you with Escape
Coverage that does not stop at what fit in the statement of work
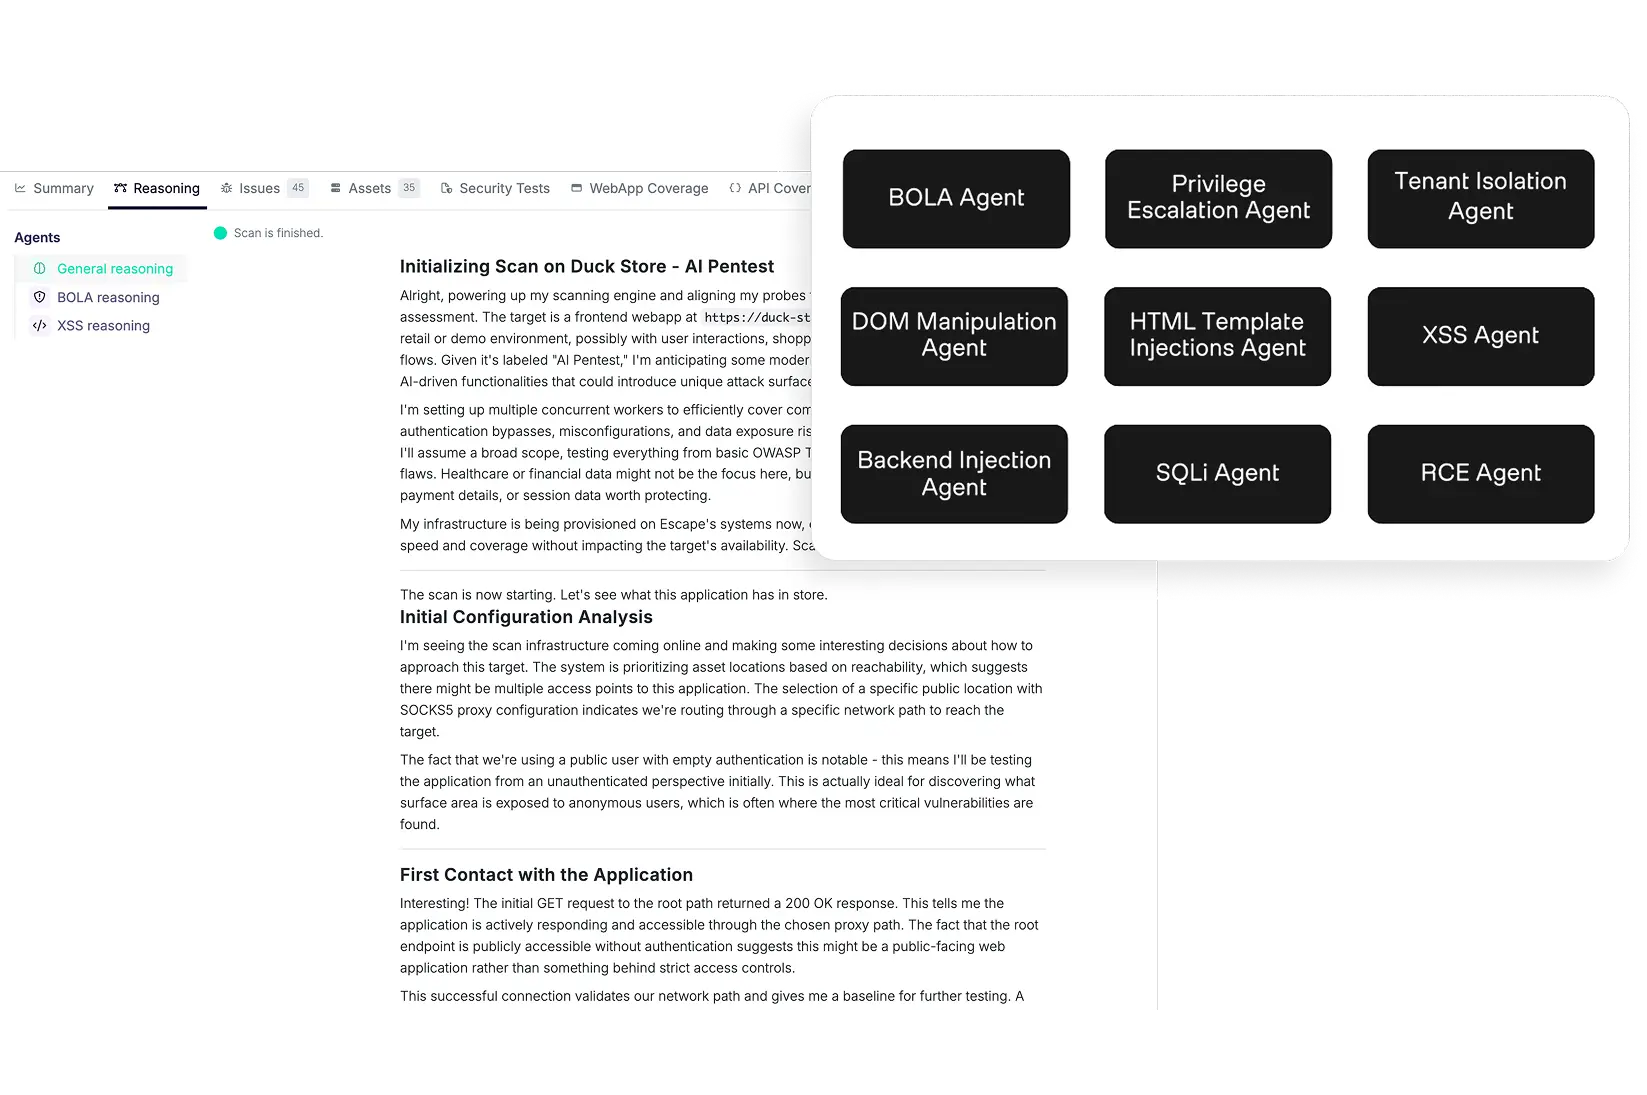
Proof that gets engineering to move
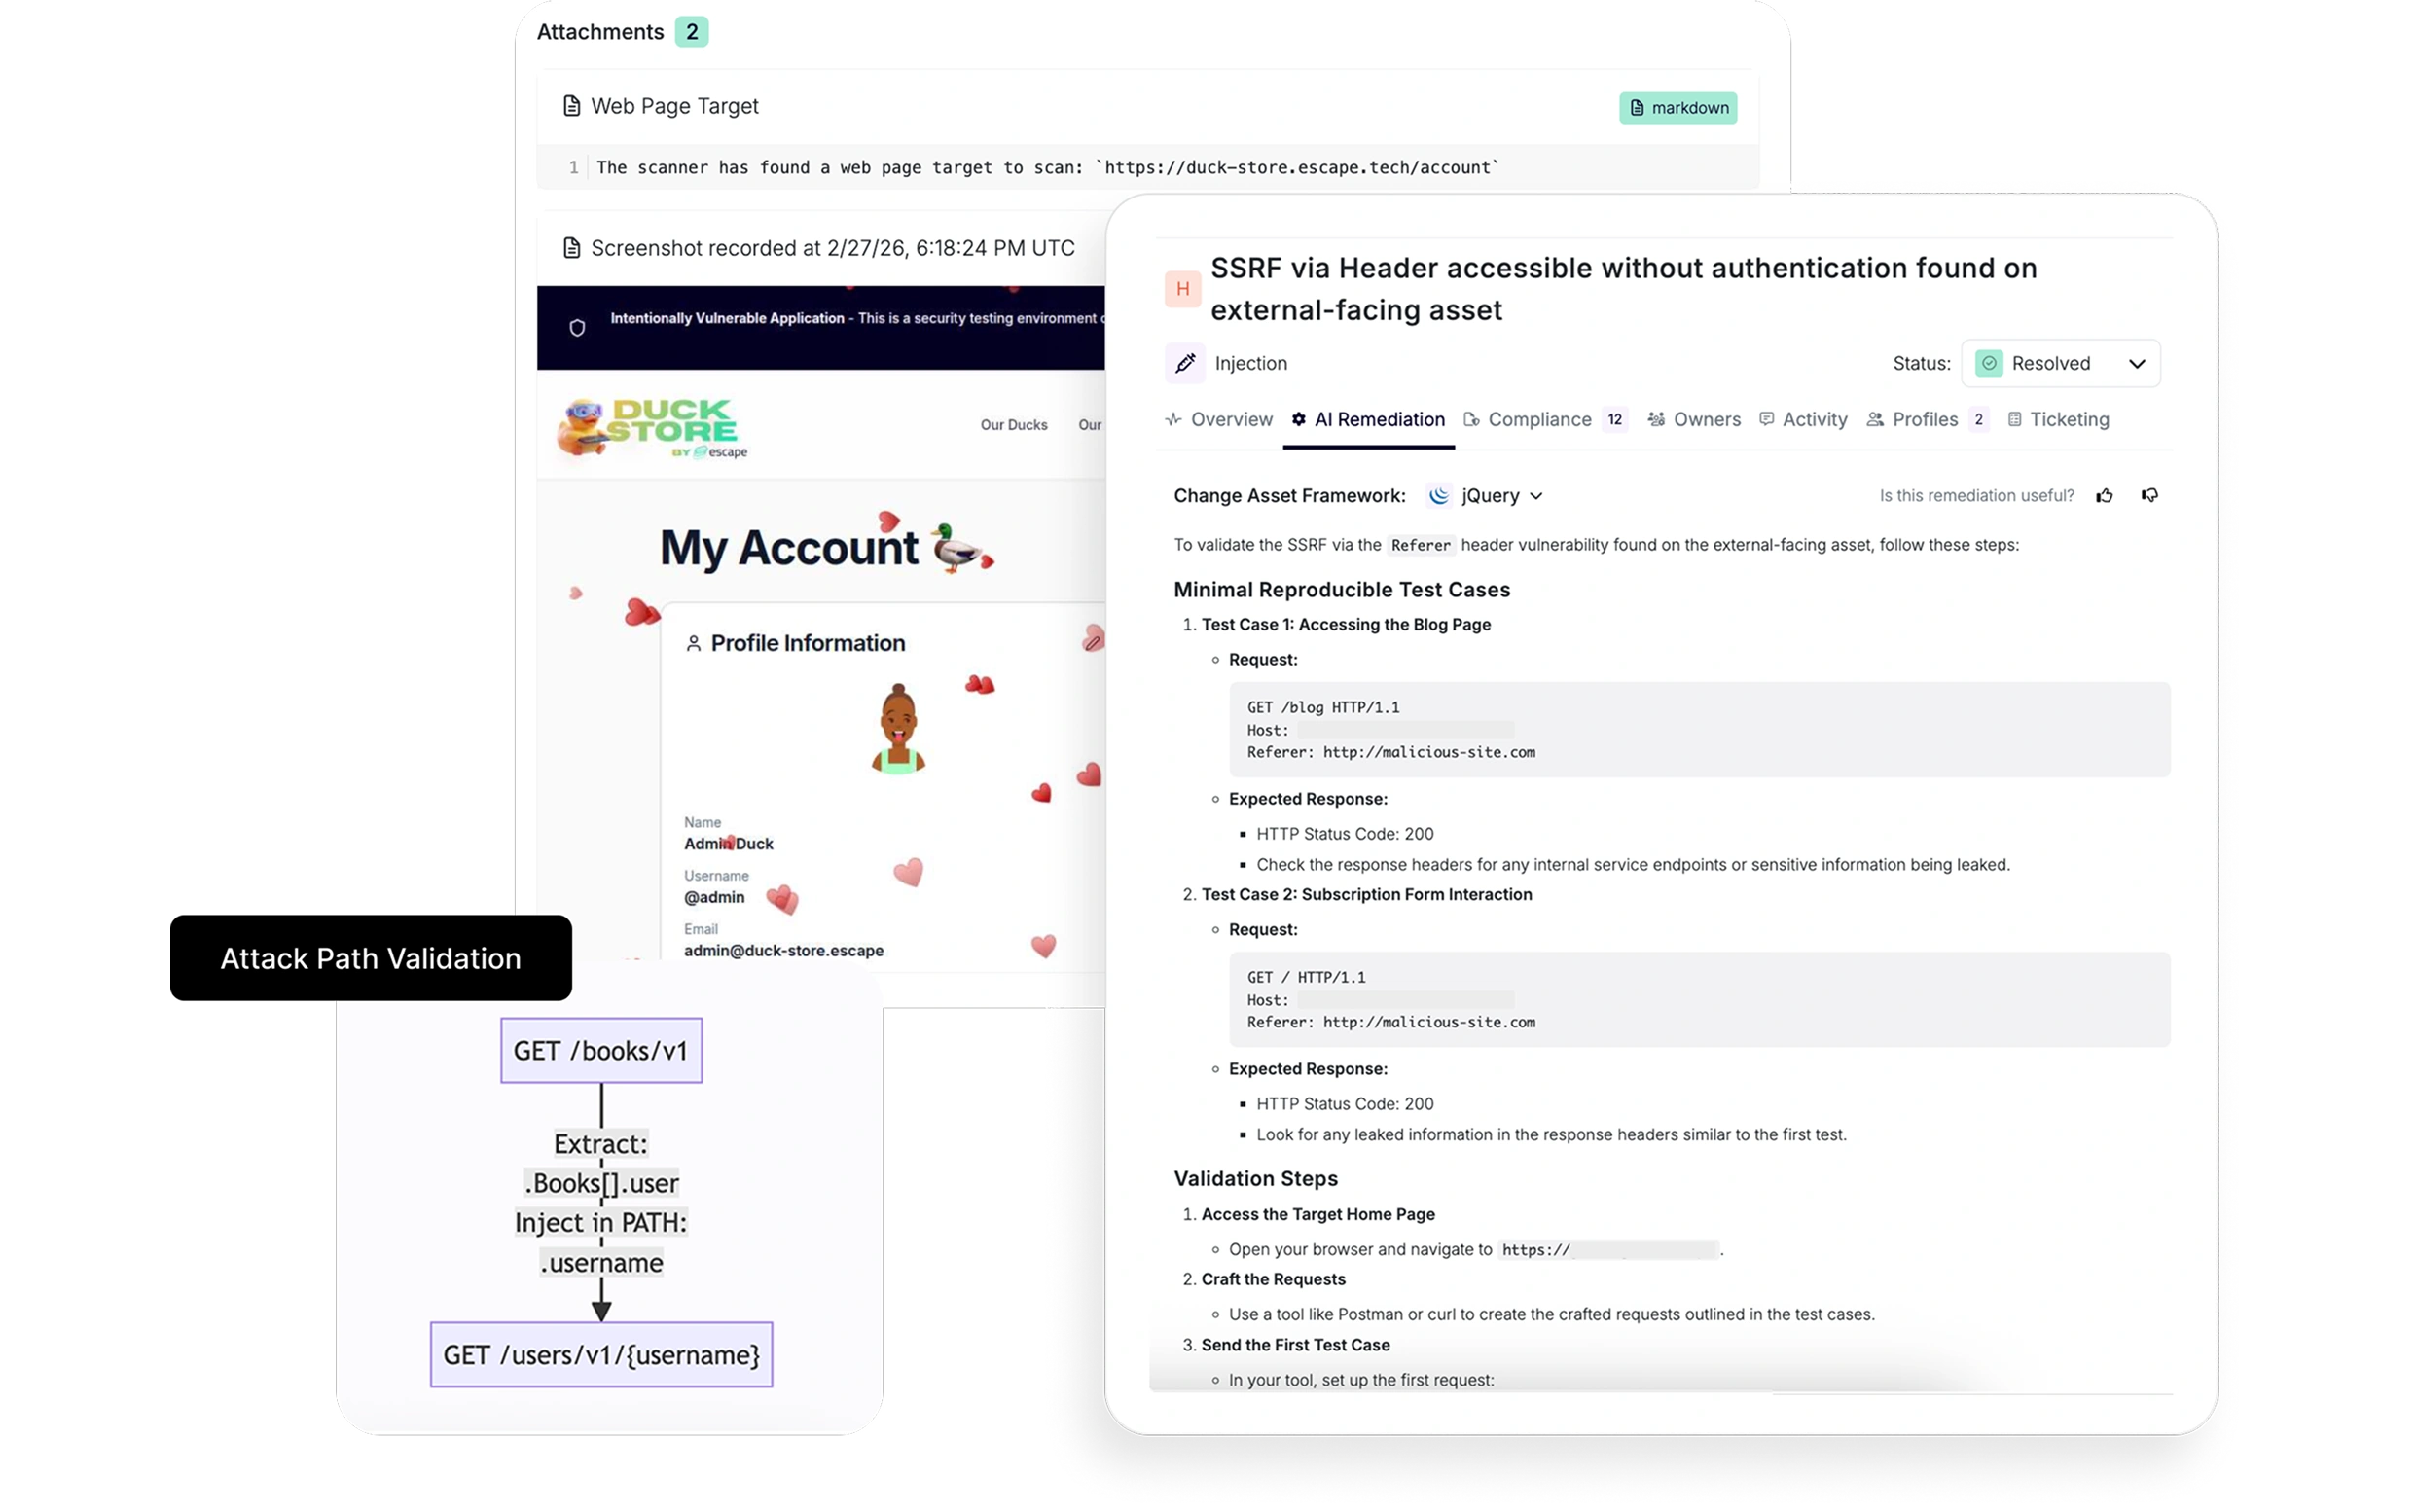
Every finding is proven, then re-tested forever
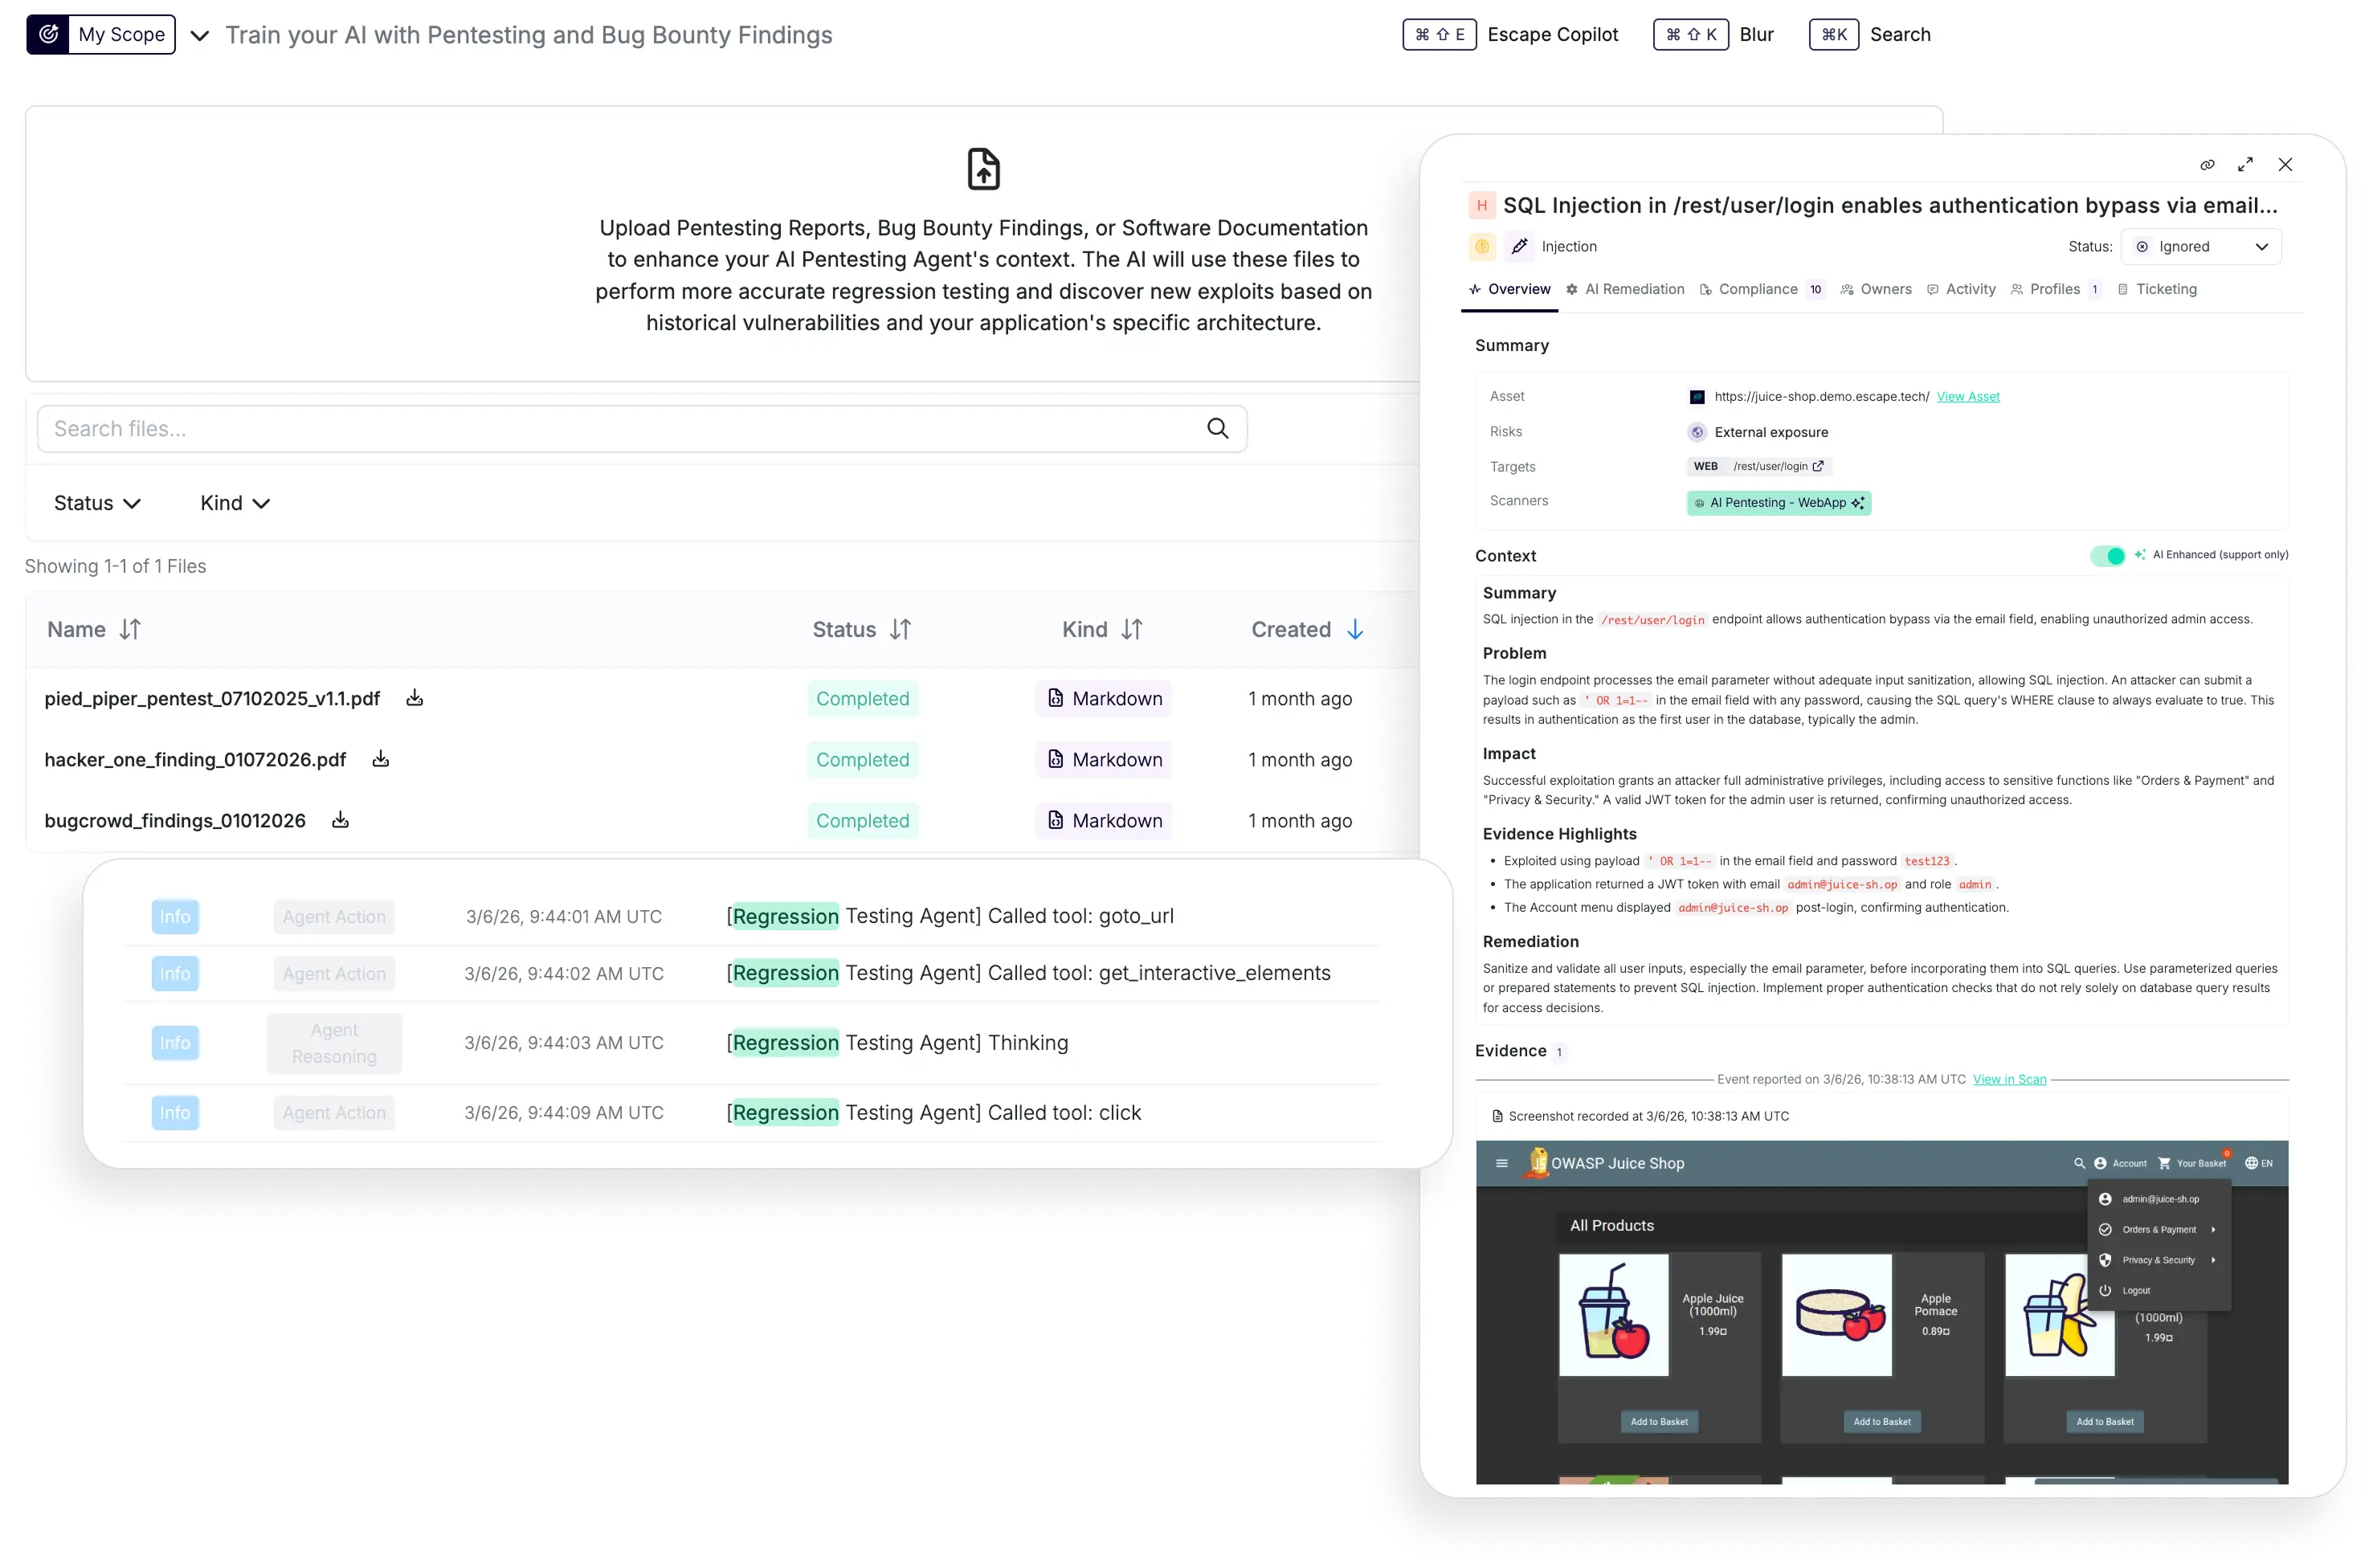
The details that separate a real offensive security program from a compliance checkbox.


Schedule a call with one of our experts
Don't take our word for it

Sr.AppSec Manager


IT Security Engineer


FAQ: What security engineers ask us
Can AI really replace a pentester?
Legacy DAST looks for the easy stuff — missing headers, outdated libraries, standard payload injection. Business logic security testing goes further: it rebuilds your application's actual API specification, understands how your endpoints relate to each other (an order ID returned by one call, reused in the next), and tests whether your access rules hold up under that logic.
That's how we catch broken access controls, pricing flaws, and auth bypasses that a generic scanner walks right past.
How is this different from a scanner?
Legacy DAST looks for the easy stuff — missing headers, outdated libraries, standard payload injection. Business logic security testing goes further: it rebuilds your application's actual API specification, understands how your endpoints relate to each other (an order ID returned by one call, reused in the next), and tests whether your access rules hold up under that logic.
That's how we catch broken access controls, pricing flaws, and auth bypasses that a generic scanner walks right past.
Does it satisfy our pentest requirement for PCI DSS or DORA?
Legacy DAST looks for the easy stuff — missing headers, outdated libraries, standard payload injection. Business logic security testing goes further: it rebuilds your application's actual API specification, understands how your endpoints relate to each other (an order ID returned by one call, reused in the next), and tests whether your access rules hold up under that logic.
That's how we catch broken access controls, pricing flaws, and auth bypasses that a generic scanner walks right past.
Can we run it on internal applications?
Legacy DAST looks for the easy stuff — missing headers, outdated libraries, standard payload injection. Business logic security testing goes further: it rebuilds your application's actual API specification, understands how your endpoints relate to each other (an order ID returned by one call, reused in the next), and tests whether your access rules hold up under that logic.
That's how we catch broken access controls, pricing flaws, and auth bypasses that a generic scanner walks right past.
Does Escape replace my annual API pentest?
Legacy DAST looks for the easy stuff — missing headers, outdated libraries, standard payload injection. Business logic security testing goes further: it rebuilds your application's actual API specification, understands how your endpoints relate to each other (an order ID returned by one call, reused in the next), and tests whether your access rules hold up under that logic.
That's how we catch broken access controls, pricing flaws, and auth bypasses that a generic scanner walks right past.
What compliance standards does Escape help with?
Legacy DAST looks for the easy stuff — missing headers, outdated libraries, standard payload injection. Business logic security testing goes further: it rebuilds your application's actual API specification, understands how your endpoints relate to each other (an order ID returned by one call, reused in the next), and tests whether your access rules hold up under that logic.
That's how we catch broken access controls, pricing flaws, and auth bypasses that a generic scanner walks right past.
We already run a bug bounty. Why this too?
Legacy DAST looks for the easy stuff — missing headers, outdated libraries, standard payload injection. Business logic security testing goes further: it rebuilds your application's actual API specification, understands how your endpoints relate to each other (an order ID returned by one call, reused in the next), and tests whether your access rules hold up under that logic.
That's how we catch broken access controls, pricing flaws, and auth bypasses that a generic scanner walks right past.
How do you keep false positives down?
Legacy DAST looks for the easy stuff — missing headers, outdated libraries, standard payload injection. Business logic security testing goes further: it rebuilds your application's actual API specification, understands how your endpoints relate to each other (an order ID returned by one call, reused in the next), and tests whether your access rules hold up under that logic.
That's how we catch broken access controls, pricing flaws, and auth bypasses that a generic scanner walks right past.
Can I drive it from the CLI and CI instead of the UI?
Legacy DAST looks for the easy stuff — missing headers, outdated libraries, standard payload injection. Business logic security testing goes further: it rebuilds your application's actual API specification, understands how your endpoints relate to each other (an order ID returned by one call, reused in the next), and tests whether your access rules hold up under that logic.
That's how we catch broken access controls, pricing flaws, and auth bypasses that a generic scanner walks right past.