Escape - Application Security & Offensive Security Blog
Explore practical offensive and application security insights covering web application testing, emerging AI cybersecurity research, API and GraphQL security, and advanced testing techniques.

Filters
Custom Security Tests
Are custom security tests a product security superpower? ⎜Keshav Malik (LinkedIn)
Welcome to the Elephant in AppSec, the podcast to explore, challenge, and boldly face the AppSec Elephants in the room.
In this article, we'll cover the main takeaways from our conversation with Keshav Malik, a senior Product Security Engineer at LinkedIn. Our goal is to help you understand
5 min read
API Security
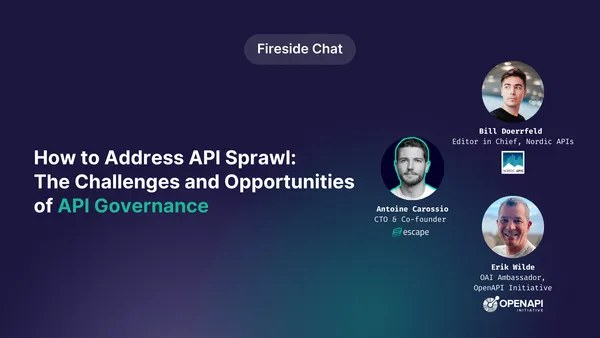
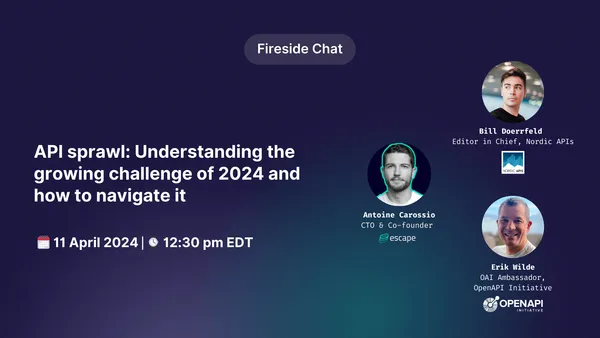
[Fireside Chat] API sprawl: Understanding the growing challenge of 2024 and how to navigate it
Hey there 👋
Join Bill Doerrfeld, tech journalist and Editor-in-Chief at the Nordic APIs blog, Erik Wilde, OAI Ambassador at the OpenAPI Initiative, and Antoine Carossio, CTO and co-founder at Escape, for a fireside chat on the challenges of API sprawl.
Sign me up!
During this live discussion, they will explore:
1 min read
API Security
Workshop "How to write custom security tests" - Main Takeaways
Organizations are constantly seeking ways to improve their defenses against business logic vulnerabilities. These vulnerabilities, often difficult to detect, can lead to significant security breaches if left unchecked. To address this challenge, we've introduced a new feature within our platform that empowers teams to create custom business logic
5 min read
API Security
Why security engineers need a new approach to identify business logic flaws
In the last decade, security scanners have evolved to identify common vulnerabilities like SQL injections.
But that’s just not enough anymore.
In 2024, data leaks in applications come from exploiting business logic flaws. In the next few years, applications will grow in size and number too fast, so the
8 min read
Podcast
The art and science of product security: A deep dive with Jacob Salassi
Welcome to the Elephant in AppSec, the podcast to explore, challenge, and boldly face the AppSec Elephants in the room.
Today we’re excited to have an amazing guest, Jacob Salassi, join us. You can find the main takeaways from our conversation with Jacob just down below!
Jacob's
6 min read
Product updates
Introducing Escape rules - Rules that adapt for you
Today, we’re launching customization improvements to Escape’s automated testing capabilities. With Escape Rules, you can now write custom security tests that do not require any maintenance and adapt to each newly discovered API and each new version of your existing APIs.
💡Want to learn how to write custom
4 min read
Application Security
Building security training for developers in 2024: Is it really worth it and how to proceed?
If you're a security engineer, the chances that you've struggled with your development team to implement secure coding practices are high. If you don't have the right culture in your organization, it might be even harder. Developers consider you as an adversary, rather than
9 min read
API Security
Sensitive data exposure: How to prevent it and where do we stand in 2025
Do you fully grasp the magnitude of sensitive data exposure? It stands as one of the most prevalent and menacing threats to organizational security in 2025.
Picture any information quintessential to an individual's or a company's identity and safety - personal, financial, health, or trade secrets.
9 min read
API Discovery
What is a Shadow API? Understanding the risks and strategies to prevent their sprawl
API Sprawl is a serious challenge in 2024, and shadow APIs are part of the problem. But do you actually know what Shadow APIs are and why they represent danger for organizations?
With the ever-increasing number of exposed APIs, the pain of not being able to gain visibility over all
6 min read
Podcast
Developers and security training: can they co-exist?⎜Laura Bell Main
Welcome to the Elephant in AppSec, the podcast to explore, challenge, and boldly face the AppSec Elephants in the room.
Today, we’re excited to have an amazing guest, Laura Bell Main, join us.
With over 20 years in software development and application security, Laura is the co-founder and CEO
2 min read
API Security
API security for PCI compliance: A deep dive into the PCI DSS 4.0 impact
There are more than 50 new requirements in PCI DSS v4.0 – do you know which ones apply to you and what you need to do to meet them? The March deadline is approaching, and we want to ensure you're fully prepared for the changes ahead.
The deadline
10 min read
API Security
How to secure gRPC APIs
Looking for ways to secure gRPC APIs? Don't worry, we've got you covered!
In this article, we will be exploring the topic of gRPC security and its importance in ensuring the security of API endpoints. We will also discuss the role of dynamic application security testing
8 min read
Podcast
AppSec vendors and CISOs: a love-hate relationship? ⎜Olivia Rose
Welcome to the Elephant in AppSec, the podcast to explore, challenge, and boldly face the AppSec Elephants in the room.
Today, we're joined by an amazing guest, Olivia Rose.
Olivia is an executive leader with more than 20 years of dedicated experience, having served as the former CISO
1 min read
API Security
Understanding Broken Object Level Authorization (BOLA) Vulnerability in API Security
Want to know how to secure your applications? You're in the right place. In this article, we will discuss a critical vulnerability that ranks number one in the OWASP API top 10 2023 - Broken Object Level Authorization, also known as BOLA. We will explore the concept of
5 min read
Application Security
4 lessons from recent application security case studies
Every organization, no matter how big or small, if it's dependent on the software (which is impossible not to be in the modern world), must prioritize software security. Interested in enhancing yours? Want to know how real-world application security challenges are tackled? Let's get straight to
6 min read
Don’t let your vulnerabilities escape.
Ready to multiply your force, not just noise?
Book a demo
Book a demo