Escape - Application Security & Offensive Security Blog
Explore practical offensive and application security insights covering web application testing, emerging AI cybersecurity research, API and GraphQL security, and advanced testing techniques.

Filters
API Security
API security for PCI compliance: A deep dive into the PCI DSS 4.0 impact
There are more than 50 new requirements in PCI DSS v4.0 – do you know which ones apply to you and what you need to do to meet them? The March deadline is approaching, and we want to ensure you're fully prepared for the changes ahead.
The deadline
10 min read
API Security
How to secure gRPC APIs
Looking for ways to secure gRPC APIs? Don't worry, we've got you covered!
In this article, we will be exploring the topic of gRPC security and its importance in ensuring the security of API endpoints. We will also discuss the role of dynamic application security testing
8 min read
Podcast
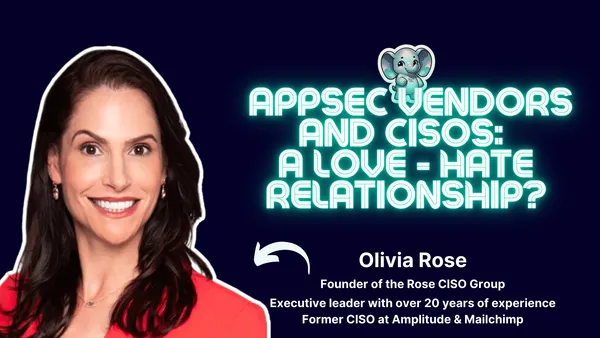
AppSec vendors and CISOs: a love-hate relationship? ⎜Olivia Rose
Welcome to the Elephant in AppSec, the podcast to explore, challenge, and boldly face the AppSec Elephants in the room.
Today, we're joined by an amazing guest, Olivia Rose.
Olivia is an executive leader with more than 20 years of dedicated experience, having served as the former CISO
1 min read
API Security
Understanding Broken Object Level Authorization (BOLA) Vulnerability in API Security
Want to know how to secure your applications? You're in the right place. In this article, we will discuss a critical vulnerability that ranks number one in the OWASP API top 10 2023 - Broken Object Level Authorization, also known as BOLA. We will explore the concept of
5 min read
Application Security
4 lessons from recent application security case studies
Every organization, no matter how big or small, if it's dependent on the software (which is impossible not to be in the modern world), must prioritize software security. Interested in enhancing yours? Want to know how real-world application security challenges are tackled? Let's get straight to
6 min read
API Security
API gateway security: 8 best practices
Are your API gateways well secured? If you have doubts, then they are not. API gateways play a large role in securing the flow of data between clients and backend services. But with the surge in API adoption (nearly 90% of developers are using APIs) and the increasing sophistication of
6 min read
API Security
Laravel SQL injection guide: Practical examples included
Want to know how to protect your Laravel applications? Dive into our latest blog post, where we guide you through the best practices for Laravel security. Explore how these techniques can not only enhance the security of your web applications but also bring tangible benefits to your development journey.
In
6 min read
API Security
Methodology: How we discovered over 18,000 API secret tokens
Hey there!
It's just the beginning of the year, but our security research team has been working hard to identify current API security challenges.
So for the Escape team, January went under the tagline "API secret sprawl" (we thought it was more fun than"Dry
6 min read
Podcast
Security training: Necessary investment or overrated expense?⎥Mel Reyes (Global CEO, CIO, CISO, & CTO with 30 years of experience)
Welcome to the Elephant in AppSec, the podcast to explore, challenge, and boldly face the AppSec Elephants in the room.
Today, we’re excited to have an amazing guest, Mel Reyes, join us.
Mel has navigated through two IPOs and three M&As, worked with several startups, Pepsi and
1 min read
Podcast
What is ASPM: A breakdown of the current state and its future⎥James Berthoty (Security at PagerDuty)
Welcome to the Elephant in AppSec, the podcast to explore, challenge, and boldly face the AppSec Elephants in the room.
Today, we're excited to have an amazing guest, James Berthoty, joining us.
James has been in technology for over 10 years across engineering and security. An early advocate
18 min read
API Security
How to build secure APIs with Ruby on Rails: Security guide
Are your Ruby on Rails APIs as secure as they could be? In today's world, where digital security is no longer an option, ensuring the robustness of your APIs is crucial. If you find yourself uncertain when attempting to answer this question, then this guide is for you.
13 min read
Flask security
Best practices to protect your Flask applications
Want to know how to protect your Flask applications? Dive into our latest blog post, where we guide you through the best practices for Flask security. Explore how these techniques can not only enhance the security of your web applications but also bring tangible benefits to your development journey.
In
12 min read
Podcast
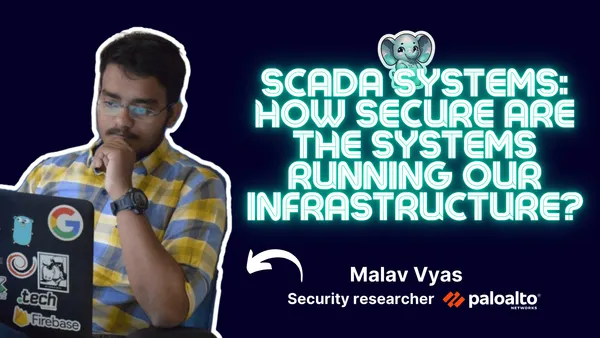
SCADA systems: How secure are the systems running our infrastructure?⎥Malav Vyas (Security Researcher at Palo Alto Networks)
Welcome to the Elephant in AppSec, the podcast to explore, challenge, and boldly face the AppSec Elephants in the room.
Today, we're excited to have an amazing guest, Malav Vyas, joining us.
Malav is a security researcher at Palo Alto Networks, passionate about exploiting and securing systems.
Security
14 min read
Application Security
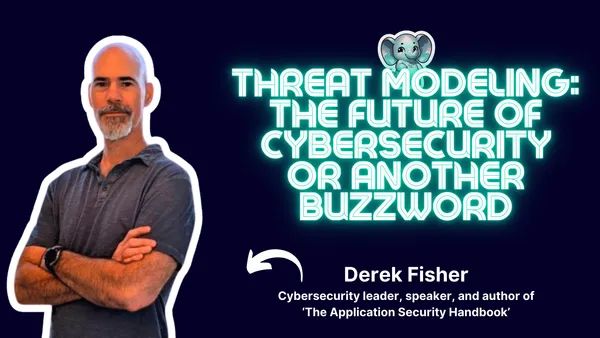
Threat modeling: the future of cybersecurity or another buzzword⎥Derek Fisher (author of The Application Security Handbook)
Welcome to the Elephant in AppSec, the podcast to explore, challenge, and boldly face the AppSec Elephants in the room.
Today we’re excited to have an amazing guest, Derek Fisher, joining us.
Derek is a cybersecurity leader, a speaker on various cybersecurity topics, and author of the famous “The
25 min read
API Security
ASP.NET security best practices
Curious about the key strategies to ensure the security and reliability of your ASP.NET applications, including building APIs? Dive into our latest blog post, where we guide you through ASP.NET security best practices. Explore how these practices can not only enhance the security of your web applications but
7 min read
Don’t let your vulnerabilities escape.
Ready to multiply your force, not just noise?
Book a demo
Book a demo