Product updates
38 posts
Product updates
Driving efficiency in pentesting: new features live in Escape
Offensive security teams are covering more dev teams every quarter without their own headcount growing to match. Their roles continue to be forced into project management and firefighting instead of finding the vulnerabilities that get them speaking spots at conferences.
Our latest batch of features removes manual steps that eat
3 min read
Product updates
wp2shell (CVE-2026-63030 + CVE-2026-60137): WordPress pre-auth RCE, now detected by Escape
wp2shell is an unauthenticated RCE chain in WordPress core. It combines two separate vulnerabilities: CVE-2026-63030 and CVE-2026-60137. Escape detects it across DAST and AI Pentesting, confirms exploitability, and shows affected assets within its Attack Surface Management.
7 min read
Product updates
Fix issues with a prompt built for your coding agent
There's a translation step between a security finding and a fix, and it's usually done by hand.
Someone opens the issue, reads the description, checks the CVSS score, follows the link to the affected asset, works out which endpoint is actually involved, then writes all of
2 min read
Product updates
Reproduce complex exploits in Escape: Multi-Step Custom Rules Are Here
Until now, custom rules in Escape were limited to single-request vulnerabilities. You could only define and test one request at a time.
This meant that more complex vulnerabilities, such as those requiring multiple chained steps (e.g., creating a user, then editing that user to escalate privileges), couldn’t be
5 min read
Product updates
Introducing Multi-User Testing with Natural Language Queries in Escape DAST
Most of today’s SaaS structures are multi-tenant environments. Making sure that each tenant’s data and resources are securely isolated from others is critical. Weaknesses or misconfigurations in tenant isolation can lead to unauthorized access or data leaks between tenants, compromising the security of the entire system.
If you’
8 min read
Product updates
Introducing AI-Powered Exploit Validation and Remediation Guidelines
Security teams know that finding a vulnerability is only half the battle. The harder part is validating that it can be exploited and applying the right fix with confidence. Too often, remediation guidance is static, generic, or incomplete, leaving engineers guessing. This also strains the relationships between security and developers.
4 min read
Product updates
August Product Updates: Enhancements to the Escape Public API and CLI, and the Introduction of Global Configuration Management
August is usually synonymous with vacations, beach days, and relaxation. But here at Escape, we’re not taking a break from empowering security teams (just kidding, we still took a break, but we shipped more efficiently!). While many are winding down, we’re cranking up the pace with some exciting
7 min read
Product updates
More Support for Complex Authentication Flows: TOTP MFA and Text-Based CAPTCHA
This June, we’re making it easier to test real-world applications with complex authentication flows without sacrificing automation.
Security teams need to test applications exactly as they exist in production, including MFA and CAPTCHA-protected flows. Historically, these protections aren’t "scanner-friendly" and often introduce friction into DAST workflows.
3 min read
Product updates
From Alert to Action: Escape’s Jira Integration Explained
Ticketing systems are an essential part of modern DevSecOps. They orchestrate cross-functional collaboration, ensure accountability, and drive issues to resolution. But in application security, the value of ticketing hinges on one critical factor: context.
Too often, security tools generate vague alerts or findings without right context associated with them that
5 min read
Product updates
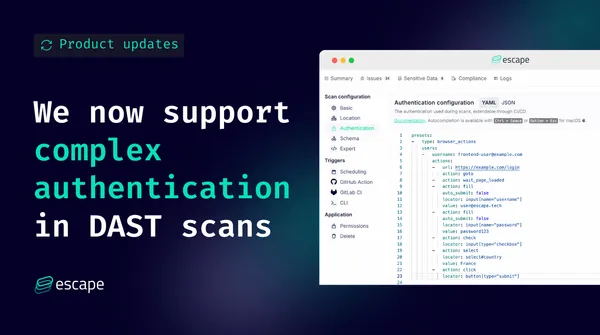
We now support complex authentication in DAST scans
We all know how frustrating the authentication process can be when running DAST scans. It's one of the most common pain points our customers face, and it often becomes a roadblock that slows down testing cycles. Whether it's dealing with complex custom authentication processes or navigating
3 min read
Product updates
Kickstart 2025 with New DAST Scanner Features
The start of a new year brings exciting updates to our DAST scanner!
Our goal is simple: to improve testing accuracy by leveraging real, concrete examples of API requests when they might be required. While we don’t need to have direct access to live traffic to start in-depth testing,
4 min read
Product updates
Introducing Private Locations: Securely Scan Your Internal Applications
While public applications often receive focused attention, the reality is that many critical applications operate behind firewalls, VPNs, or in private networks. These internal apps can be just as vulnerable to attacks—but securing them without disrupting your infrastructure can be a challenge.
Today, we’re introducing Private Locations, a
3 min read