The Elephant in AppSec
21 posts
Application Security
The Schedule is Live: The Elephant in AppSec Conference
The Elephant in AppSec Conference agenda is live! It’s packed with sessions that dive into what’s broken in AppSec, how to fix it, and unique insights from top experts on the latest AppSec tooling.
Prepare for bold opinions and fresh perspectives, where the best in Application Security come
2 min read
Application Security
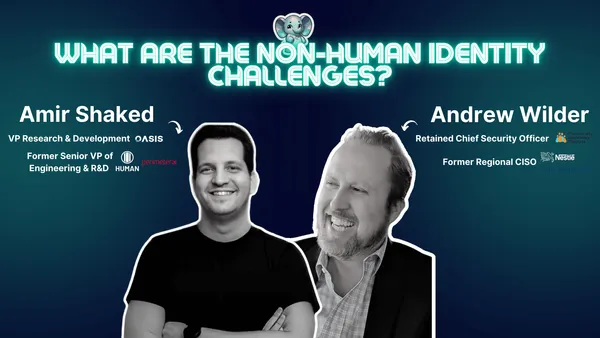
How to secure non-human identities? with Andrew Wilder and Amir Shaked
This blog is based on our conversation with Andrew Wilder, Retained Chief Security Officer at Community Veterinary Partners and Amir Shaked, VP of R&D at Oasis Security. It covers the unique challenges of securing non-human identities.
8 min read
Application Security
Software Supply Chain Risks ⎪Cassie Crossley (VP Supply Chain Security, Schneider Electric)
This blog is based on our conversation with Cassie Crossley, Vice President of Supply Chain Security at Schneider Electric. It covers the unique challenges of software supply chain security.
10 min read
Custom Security Tests
Are custom security tests a product security superpower? ⎜Keshav Malik (LinkedIn)
Welcome to the Elephant in AppSec, the podcast to explore, challenge, and boldly face the AppSec Elephants in the room.
In this article, we'll cover the main takeaways from our conversation with Keshav Malik, a senior Product Security Engineer at LinkedIn. Our goal is to help you understand
5 min read
Podcast
The art and science of product security: A deep dive with Jacob Salassi
Welcome to the Elephant in AppSec, the podcast to explore, challenge, and boldly face the AppSec Elephants in the room.
Today we’re excited to have an amazing guest, Jacob Salassi, join us. You can find the main takeaways from our conversation with Jacob just down below!
Jacob's
6 min read
Podcast
Developers and security training: can they co-exist?⎜Laura Bell Main
Welcome to the Elephant in AppSec, the podcast to explore, challenge, and boldly face the AppSec Elephants in the room.
Today, we’re excited to have an amazing guest, Laura Bell Main, join us.
With over 20 years in software development and application security, Laura is the co-founder and CEO
2 min read
Podcast
AppSec vendors and CISOs: a love-hate relationship? ⎜Olivia Rose
Welcome to the Elephant in AppSec, the podcast to explore, challenge, and boldly face the AppSec Elephants in the room.
Today, we're joined by an amazing guest, Olivia Rose.
Olivia is an executive leader with more than 20 years of dedicated experience, having served as the former CISO
1 min read
Podcast
Security training: Necessary investment or overrated expense?⎥Mel Reyes (Global CEO, CIO, CISO, & CTO with 30 years of experience)
Welcome to the Elephant in AppSec, the podcast to explore, challenge, and boldly face the AppSec Elephants in the room.
Today, we’re excited to have an amazing guest, Mel Reyes, join us.
Mel has navigated through two IPOs and three M&As, worked with several startups, Pepsi and
1 min read
Podcast
What is ASPM: A breakdown of the current state and its future⎥James Berthoty (Security at PagerDuty)
Welcome to the Elephant in AppSec, the podcast to explore, challenge, and boldly face the AppSec Elephants in the room.
Today, we're excited to have an amazing guest, James Berthoty, joining us.
James has been in technology for over 10 years across engineering and security. An early advocate
18 min read
Podcast
SCADA systems: How secure are the systems running our infrastructure?⎥Malav Vyas (Security Researcher at Palo Alto Networks)
Welcome to the Elephant in AppSec, the podcast to explore, challenge, and boldly face the AppSec Elephants in the room.
Today, we're excited to have an amazing guest, Malav Vyas, joining us.
Malav is a security researcher at Palo Alto Networks, passionate about exploiting and securing systems.
Security
14 min read
Application Security
Threat modeling: the future of cybersecurity or another buzzword⎥Derek Fisher (author of The Application Security Handbook)
Welcome to the Elephant in AppSec, the podcast to explore, challenge, and boldly face the AppSec Elephants in the room.
Today we’re excited to have an amazing guest, Derek Fisher, joining us.
Derek is a cybersecurity leader, a speaker on various cybersecurity topics, and author of the famous “The
25 min read