Escape - Application Security & Offensive Security Blog
Explore practical offensive and application security insights covering web application testing, emerging AI cybersecurity research, API and GraphQL security, and advanced testing techniques.

Filters
Shift left
Why ‘Shift-Left’ Isn’t Good Enough? Our conversation with Chris Romeo
This blog is based on our conversation with Chris Romeo, founder of Devici, an AI-infused collaborative threat modeling tool. It explores how "shift-left" may be a useful tool in the security toolkit, but it’s far from the only one.
6 min read
Product updates
Product Updates: Persisted GraphQL Query Support
You can now test the security of persisted GraphQL Queries with Escape's platform. This new capability enhances our GraphQL API security testing by providing deeper insights into vulnerabilities specific to persisted queries, enabling your team to protect your APIs from targeted attacks better.
We support the following formats:
2 min read
API Security
Escape vs Rapid7 InsightAppSec: The Best Rapid7 Alternative For Modern DAST
Explore how Escape DAST serves as the best alternative to Rapid7, offering advanced vulnerability detection for web applications and APIs, support for complex authentication and seamless integration into modern development workflows.
10 min read
Product updates
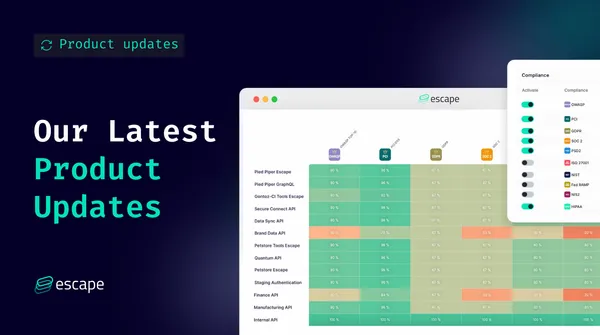
Our Latest Product Updates
We’re constantly improving our product for our customers. See the latest features, improvements, and fixes we have shipped over the past month.
Customize your compliance view
Last month we shipped a new feature designed to enhance your compliance management experience. It allows you to hide irrelevant compliance frameworks from
5 min read
API Security
Reinventing API security: Why Escape is better than traditional traffic-based tools
We have been doing API Security wrong. Discover how the limitations of traffic-based API security tools might impact your security and why Escape's agentless technology is the best way to protect your APIs.
12 min read
Podcast
AI Security: How Hard Is It to Develop Secure AI?
This blog is based on our conversation with Rob van der Veer, Senior Principal Expert at the Software Improvement Group. It explores the complex challenges of developing secure AI systems and the critical role of governance and role segregation in AI security.
8 min read
Product updates
Product updates: Automated schema generation
We are excited to introduce our latest feature: automated schema generation for all your discovered APIs.
Having an OpenAPI Specification (OAS) is beneficial because it provides a standardized, machine-readable format for documenting RESTful APIs, promoting clarity and consistency across different services. with an OAS, developers can leverage a plethora of
4 min read
API Security
Limitations of current automatic specification generation tools
Have you ever wondered how automatic specification generation can streamline API security scanning? By significantly reducing the manual effort involved in creating and maintaining API specifications, automated tools offer clear benefits in terms of scan accuracy and setup time.
Yet, many existing tools on the market have notable limitations. Understanding
5 min read
Application Security
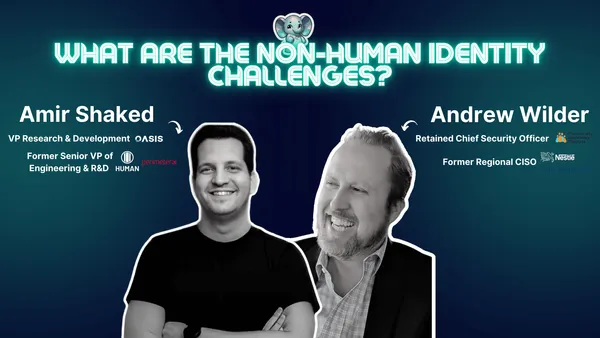
How to secure non-human identities? with Andrew Wilder and Amir Shaked
This blog is based on our conversation with Andrew Wilder, Retained Chief Security Officer at Community Veterinary Partners and Amir Shaked, VP of R&D at Oasis Security. It covers the unique challenges of securing non-human identities.
8 min read
Application Security
Software Supply Chain Risks ⎪Cassie Crossley (VP Supply Chain Security, Schneider Electric)
This blog is based on our conversation with Cassie Crossley, Vice President of Supply Chain Security at Schneider Electric. It covers the unique challenges of software supply chain security.
10 min read
Case Study
Case Study: How Sungage Financial improved their application security within 1 week
Sungage Financial chose Escape's API security solution to secure their new GraphQL APIs. Escape’s easy setup, actionable remediation, and GraphQL support enabled comprehensive risk evaluation and swift vulnerability fixes, enhancing security and efficiency.
3 min read
Don’t let your vulnerabilities escape.
Ready to multiply your force, not just noise?
Book a demo
Book a demo