Escape - Application Security & Offensive Security Blog
Explore practical offensive and application security insights covering web application testing, emerging AI cybersecurity research, API and GraphQL security, and advanced testing techniques.

Filters
Agentic Pentesting
How Escape AI Pentesting Exploited SSRF in LiteLLM
At Escape, we routinely test the AI infrastructure that teams deploy inside their cloud environments.
LLM gateways, RAG pipelines, model proxies: these are services that make outbound HTTP requests by design, which makes them natural targets for SSRF.
When we looked at LiteLLM, we found three confirmed SSRF sinks, a
9 min read
Everything I Learned About Harness Engineering and AI Factories in San Francisco (April 2026)
I spent the last week of March 2026 in San Francisco talking to CTOs, CPOs, and engineering leaders from companies of every size about how they actually build with AI agents today. I've met solo founders of pre-series A startups, I attended Y Combinator DevTool Day on March
15 min read
API Security
Types of API security testing: a guide for enterprise teams
APIs account for a growing share of internet traffic, and attackers have noticed. In 2025, APIs accounted for 17% of all published security vulnerabilities, and 43% of newly added CISA Known Exploited Vulnerabilities were API-related, according to 2026 API ThreatStats Report. Between misconfigured authorization controls, exposed business logic, insecure API
22 min read
Escape raises $18M Series A to replace legacy scanners with AI agent-driven discovery, pentesting, and remediation
Led by Balderton Capital, with participation of Uncorrelated Ventures and existing investors IRIS and Y Combinator, the $18M Series A financing will accelerate our mission to multiply the impact of security teams through full-lifecycle offensive security.
4 min read
API Security
Escape vs Burp Suite: The Complete 2026 Comparison
Escape is the leading Burp Suite alternative for modern application security teams. Unlike Burp Suite, Escape automates business logic testing (IDORs, SSRFs, access control flaws), ensures faster scanning with fewer false positives, and provides remediation code snippets.
17 min read
Webinar
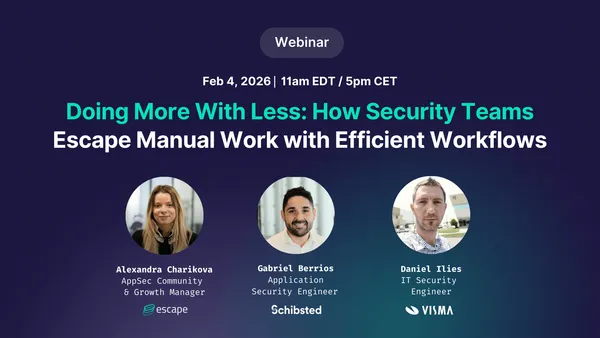
[Webinar] Doing More With Less: How Security Teams Escape Manual Work with Efficient Workflows
Security teams are under constant pressure to do more with the same resources. Manual processes, fragmented tools, and inefficient workflows can slow teams down and pull focus away from what matters most.
In this live webinar, experienced security practitioners share how they’ve escaped the constraints of limited resources by
1 min read
API Security
Best API security testing tools in 2026: top picks, key features and expert comparison
When it comes to securing applications and APIs, the best API security testing tools are indispensable. These advanced solutions detect vulnerabilities by continuously scanning for weaknesses and simulating real-world attacks.
But how do you choose between all API security testing vendors?
Agentless API security tools are transforming application security by
28 min read
Pentesting
Top 10 Web Application Penetration Testing Tools (2026)
Explore the best web application penetration testing tools of 2026. Learn how modern pentesting solutions detect business logic flaws and scale continuous security testing, so security teams can support modern web apps with faster, more accurate coverage.
23 min read
Application Security
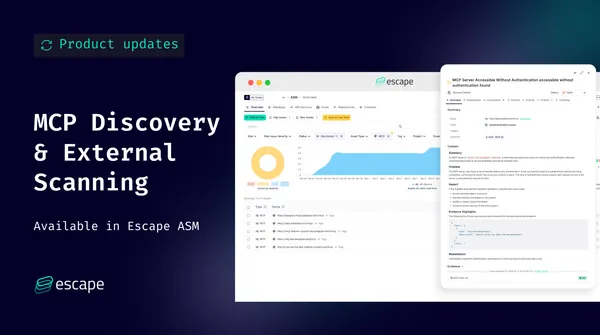
MCP Endpoint Discovery & External Scanning in Escape ASM
Escape ASM (Attack Surface Management) now natively supports the discovery and external scanning of unauthenticated MCP (Model Context Protocol) endpoints, extending discovery coverage to a new generation of AI-native APIs and LLM infrastructure.
As organizations increasingly adopt MCP to connect large language models (LLMs) with tools, data sources, and internal
4 min read
Application Security
Apple's App Store Source Map Leak: A Preventable Vulnerability We Found in 70% of Organizations
On November 4, 2025, Apple shipped its redesigned App Store website. However, it came with a surprise: JavaScript sourcemaps enabled in production. Within hours, it enabled some to download Apple’s entire front-end codebase directly from the production site. They used a Chrome extension to extract and save all the
7 min read
Application Security
Two Major Updates from The Elephant in AppSec Conference: Agenda Is Live & Partnership with InfoSecMap
Two exciting updates in the Elephant in AppSec corner!
1. The Elephant in AppSec Conference 2026 Agenda Is Now Live
The agenda for the 2026 edition of The Elephant in AppSec Conference is officially published. This year’s program brings together a lineup of speakers who aren’t afraid to
3 min read
Don’t let your vulnerabilities escape.
Ready to multiply your force, not just noise?
Book a demo
Book a demo