Escape - Application Security & Offensive Security Blog
Explore practical offensive and application security insights covering web application testing, emerging AI cybersecurity research, API and GraphQL security, and advanced testing techniques.

Filters
API Security
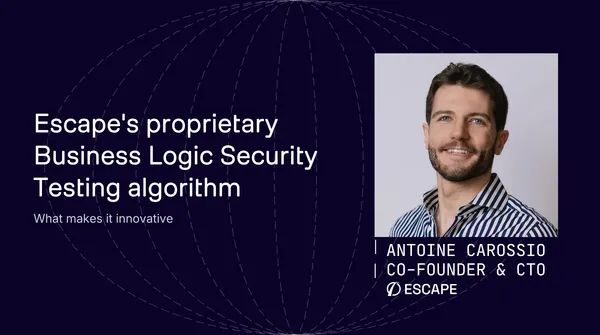
Escape's DAST proprietary Business Logic Security Testing algorithm: what makes it innovative
Testing APIs for Business Logic vulnerabilities is hard. Actually, this is a mission that old-school DAST solutions like ZAP (formerly OWASP ZAP) cannot handle.
I'm Antoine Carossio, passionate about Computer Science for more than 15 years now and cofounder & CTO of Escape. With my team, we'
10 min read
Pentesting
Best 8 AI Pentesting Tools in 2026
Explore the best AI pentesting tools in 2026. Learn how modern pentesting solutions detect business logic flaws and scale continuous security testing, so security teams can replace manual pentests with faster, more accurate coverage. Updated: August 2026
26 min read
Product updates
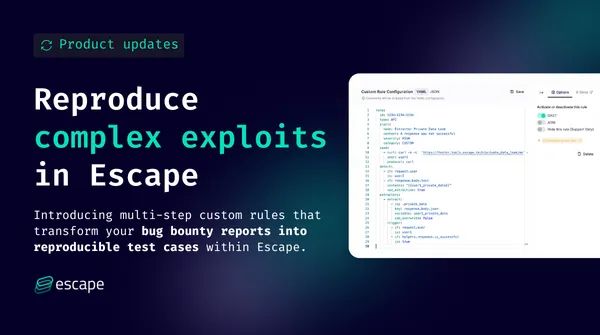
Reproduce complex exploits in Escape: Multi-Step Custom Rules Are Here
Until now, custom rules in Escape were limited to single-request vulnerabilities. You could only define and test one request at a time.
This meant that more complex vulnerabilities, such as those requiring multiple chained steps (e.g., creating a user, then editing that user to escalate privileges), couldn’t be
5 min read
[Webinar] Automating Offensive Security with AI: A Guide to Scaling Pentesting with Escape
Automated pentesting is now one of the most hyped topics in cybersecurity, with AI systems promising to replace human hackers. But how much is real, and how much is marketing hype?
This webinar provides a practical guide to automating offensive security, built from the perspective of offensive and application security
1 min read
Case Study
From Complex Authentication to Confident Coverage: How Applied Systems Transformed Their AppSec with Escape
In a recent webinar on "From Business Logic Vulnerabilities to Actionable Insights: AI-powered Pentesting + ASM in Action," Andrew Orr Erwing, Manager of Security Engineering (AppSec) at Applied Systems, shared his team's journey in modernizing their application security approach.
For organizations that have grown rapidly through acquisitions,
4 min read
Research
Methodology: How we discovered over 2k high-impact vulnerabilities in apps built with vibe coding platforms
Hey there,
With Halloween around the corner, what’s scarier for organizations than vulnerabilities in their web applications?
And it's even scarier when the development of these applications is in the hands of users not familiar with security practices.
This year, the Escape research team has focused on
10 min read
Product updates
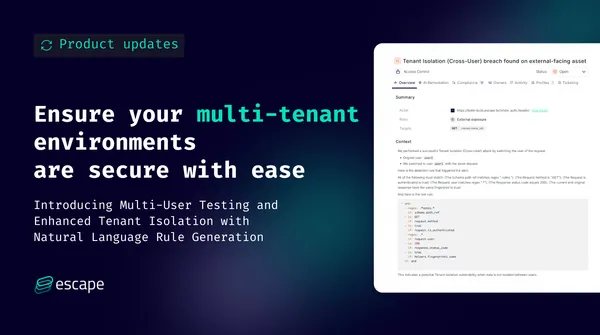
Introducing Multi-User Testing with Natural Language Queries in Escape DAST
Most of today’s SaaS structures are multi-tenant environments. Making sure that each tenant’s data and resources are securely isolated from others is critical. Weaknesses or misconfigurations in tenant isolation can lead to unauthorized access or data leaks between tenants, compromising the security of the entire system.
If you’
8 min read
Competitor Comparison
Detectify alternatives in 2026: Escape vs Detectify and 4 more tools
Looking for a Detectify alternative? Compare Escape vs Detectify on API and app security, pricing, G2 ratings, and key features. See why security teams choose this application security scanner for business logic testing and internal app scanning.
19 min read
Application Security
Gin & Juice Shop Benchmark: How DAST Tools Really Stack Up
This month, we set out to compare our DAST against some of the established names in Dynamic Application Security Testing. We’ve already benchmarked our scanner on vulnerable apps like VAMPI and DVGA, and now we’re putting it up against Qualys, ZAP, and Intruder (available in free trial) on
11 min read
Attack Surface Management
Why context is king in Attack Surface Management (ASM): Key insights from my conversations with security leaders
When I launched this research, my goal was to understand the current perception of security practitioners regarding Attack Surface Management (ASM) solutions. Unlike in my previous article, "What is wrong with the current state of DAST?" I didn't start with an overall negative perception from the
8 min read
Product updates
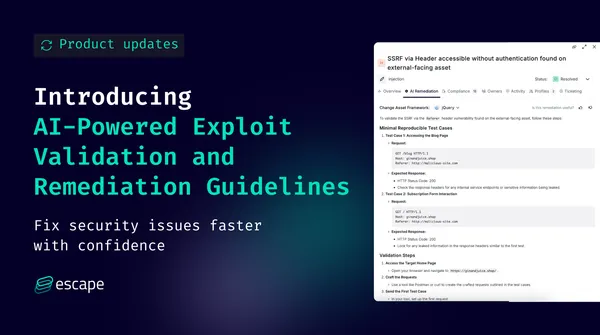
Introducing AI-Powered Exploit Validation and Remediation Guidelines
Security teams know that finding a vulnerability is only half the battle. The harder part is validating that it can be exploited and applying the right fix with confidence. Too often, remediation guidance is static, generic, or incomplete, leaving engineers guessing. This also strains the relationships between security and developers.
4 min read
Application Security
[Webinar] From Business Logic Vulnerabilities to Actionable Insights: AI-powered Pentesting + ASM in Action
For years, security teams have relied on human penetration testers to uncover critical vulnerabilities hidden in complex business logic. These flaws are subtle, context-dependent, and unique to every system’s workflow. Even modern scanners struggle to capture them, focusing only on a limited range of vulnerabilities displayed in their UI.
2 min read
Product updates
August Product Updates: Enhancements to the Escape Public API and CLI, and the Introduction of Global Configuration Management
August is usually synonymous with vacations, beach days, and relaxation. But here at Escape, we’re not taking a break from empowering security teams (just kidding, we still took a break, but we shipped more efficiently!). While many are winding down, we’re cranking up the pace with some exciting
7 min read
Pentesting
Top Automated Penetration Testing Tools (2026)
Explore the best automated penetration testing tools of 2026. Learn how modern pentesting solutions detect business logic flaws and scale continuous security testing, so security teams can replace manual pentests with faster, more accurate coverage.
29 min read
Application Security
Top Vulnerability Scanning tools 2026
In 2026, vulnerability scanning tools are essential for modern security teams, but running a scan is rarely the hard part anymore. The real challenge is automating it at scale: across thousands of assets, spanning APIs, web applications, and cloud services, in environments that can change by the hour.
Security engineers
23 min read
Application Security
How to Automate Your Penetration Testing?
AI is revolutionizing penetration testing, transforming traditionally manual exploits, once spanning several days, into automated systems that can now handle reconnaissance, scanning, and fuzzing in a matter of hours.
Automate your pentesting
For teams that deploy every day
Book a demo →
Learn more
"AI is already transforming pentesting. If
11 min read
Don’t let your vulnerabilities escape.
Ready to multiply your force, not just noise?
Book a demo
Book a demo