Escape - Application Security & Offensive Security Blog
Explore practical offensive and application security insights covering web application testing, emerging AI cybersecurity research, API and GraphQL security, and advanced testing techniques.

Filters
Announcement
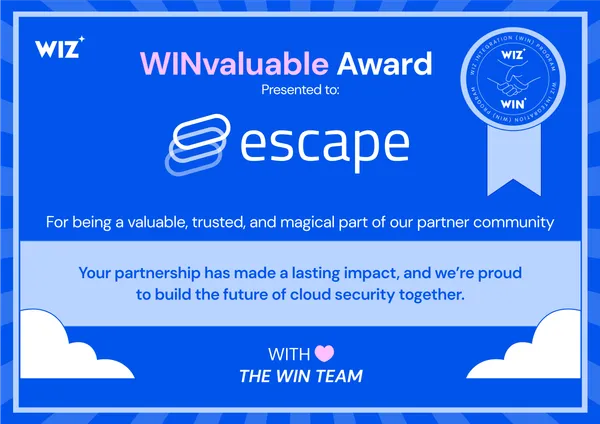
Escape Honored with Inaugural Wiz Integrations (WIN) Partner Award
Escape has been recognized by Wiz as a winner in the inaugural WIN awards, earning the WINvaluable Award for its outstanding partnership!
This recognition highlights Escape's track record of delivering real outcomes for joint customers through the WIN program.
💡Launched in 2023, WIN is Wiz’s open, bidirectional
2 min read
How to Efficiently Implement DAST in CI/CD (2026 Guide)
Working with multiple customers implementing DAST in CI/CD has allowed us to learn a lot about what works, what doesn’t, and most importantly how to do it efficiently.
The truth is, it’s not about adopting just any tool. It's about making testing for runtime vulnerabilities
16 min read
GraphQL
The Paradox of Disabling GraphQL Introspection: Lessons from the Parse Server GraphQL API vulnerability
Last week, the security community was alerted to a vulnerability in Parse Server GraphQL API, which allowed public access to the GraphQL schema without requiring a session token or the master key. It is now identified as CVE-2025-53364.
So, the question comes up: Should we disable introspection entirely in production
4 min read
Application Security
Feedback From Escape Customers: Securing AI-Driven Applications with DAST
“You ask the developer why they wrote the code the way that they did, and they don’t have an answer anymore. They’re like, ‘Well, AI wrote it.” - Seth Kirschner, DoubleVerify
AI is now deeply embedded in software development workflows, and the implications for application security teams are
11 min read
Product updates
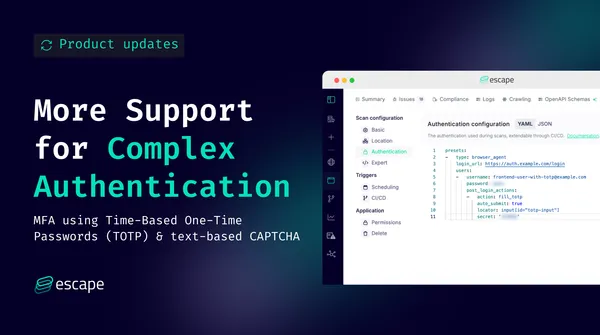
More Support for Complex Authentication Flows: TOTP MFA and Text-Based CAPTCHA
This June, we’re making it easier to test real-world applications with complex authentication flows without sacrificing automation.
Security teams need to test applications exactly as they exist in production, including MFA and CAPTCHA-protected flows. Historically, these protections aren’t "scanner-friendly" and often introduce friction into DAST workflows.
3 min read
Application Security
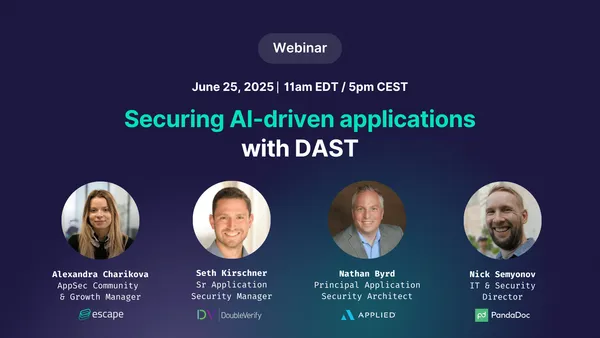
[Webinar] Securing AI-driven applications with DAST
Join us for a live webinar with application security experts and Escape clients - Seth Kirschner (DoubleVerify), Nathan Byrd (Applied Systems), Nick Semyonov (PandaDoc), as they break down how their teams are rethinking testing strategies to keep up with AI-influenced codebases.
1 min read
Compliance
Why DAST Is Critical for Cyber Resilience Act Compliance
The EU’s Cyber Resilience Act is reshaping how companies build and secure digital products. Learn why modern DAST is critical for CRA compliance from secure development to incident response and how to prepare before the 2027 deadline.
10 min read
Product updates
From Alert to Action: Escape’s Jira Integration Explained
Ticketing systems are an essential part of modern DevSecOps. They orchestrate cross-functional collaboration, ensure accountability, and drive issues to resolution. But in application security, the value of ticketing hinges on one critical factor: context.
Too often, security tools generate vague alerts or findings without right context associated with them that
5 min read
Case Study
How Escape Enabled Deeper Business Logic Testing for Arkose Labs
Arkose Labs is a global cybersecurity company that specializes in account security, including bot management, device ID, anti-phishing and email intelligence. Its unified platform helps the world’s biggest enterprises across industries, including banking, gaming, e-commerce and social media, protect user accounts and digital ecosystems from malicious automation, credential stuffing
4 min read
Application Security
The Alternative to Acunetix DAST: Escape DAST
Explore how Escape DAST serves as a superior alternative to Acunetix, offering advanced vulnerability detection for web applications and APIs, seamless integration into modern development workflows, and scalable solutions for enterprises.
8 min read
Announcement
Escape Joins the AWS ISV Accelerate Program to Drive the Future of DAST in Enterprises
A couple of weeks before the RSA conference, we're thrilled to share that Escape has officially joined the AWS ISV Accelerate Program! This is a huge milestone for us, and it marks an exciting new chapter in our mission to transform how enterprises approach application discovery and dynamic
2 min read
Product updates
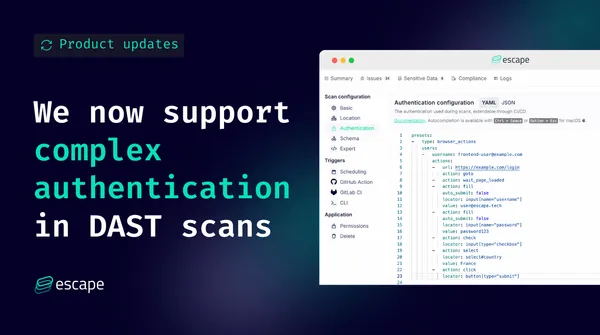
We now support complex authentication in DAST scans
We all know how frustrating the authentication process can be when running DAST scans. It's one of the most common pain points our customers face, and it often becomes a roadblock that slows down testing cycles. Whether it's dealing with complex custom authentication processes or navigating
3 min read
Application Security
How to build a strong business case for replacing legacy DAST with a modern solution - a practical guide
Legacy DAST tools have long been a component in product security programs, but many have become outdated today. Traditional DAST tools were built for yesterday’s web, often providing only basic web scan results and struggling with modern languages like GraphQL or React JS . They tend to be slow, noisy,
10 min read
Webinar recap
Webinar recap: How to combine SAST and DAST for complete application coverage
Modern applications come with a whole host of challenges that legacy SASTs and DASTs simply cannot keep up with. If you want to be sure no vulnerabilities slip through the cracks in these applications, the key is combining a modern SAST and DAST.
Why?
Last week, Escape’s CEO Tristan
16 min read
Don’t let your vulnerabilities escape.
Ready to multiply your force, not just noise?
Book a demo
Book a demo