Pentesting
19 posts
Compliance
Compliance penetration testing requirements, by framework
Introduction
Your auditor wants your latest pentest report to close a control. That same week, a prospect's security team asks for the same PDF before they'll sign. The good news is that the penetration testing requirements behind both mostly agree on timing, and this guide to
17 min read
Pentesting
How to build a continuous pentesting program
Introduction
An unpatched flaw is now the most common entry point for a breach, at 31%, ahead of stolen credentials at 13%, and the median time to fix one has crept up to 43 days (Verizon's 2026 DBIR). So an annual pentest is always a step behind, and
10 min read
Webinar
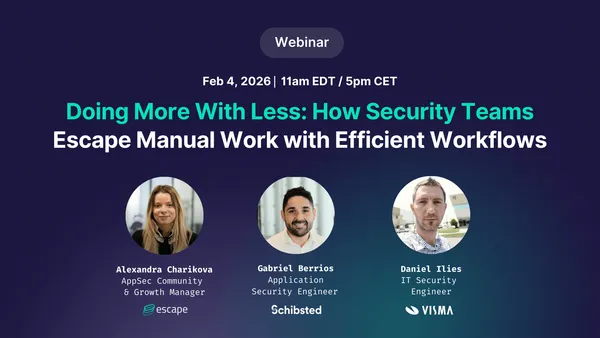
[Webinar] Doing More With Less: How Security Teams Escape Manual Work with Efficient Workflows
Security teams are under constant pressure to do more with the same resources. Manual processes, fragmented tools, and inefficient workflows can slow teams down and pull focus away from what matters most.
In this live webinar, experienced security practitioners share how they’ve escaped the constraints of limited resources by
1 min read
Pentesting
Top 10 Web Application Penetration Testing Tools (2026)
Explore the best web application penetration testing tools of 2026. Learn how modern pentesting solutions detect business logic flaws and scale continuous security testing, so security teams can support modern web apps with faster, more accurate coverage.
23 min read
Pentesting
Best 8 AI Pentesting Tools in 2026
Explore the best AI pentesting tools in 2026. Learn how modern pentesting solutions detect business logic flaws and scale continuous security testing, so security teams can replace manual pentests with faster, more accurate coverage. Updated: August 2026
26 min read
Pentesting
Top Automated Penetration Testing Tools (2026)
Explore the best automated penetration testing tools of 2026. Learn how modern pentesting solutions detect business logic flaws and scale continuous security testing, so security teams can replace manual pentests with faster, more accurate coverage.
29 min read
Application Security
How to Automate Your Penetration Testing?
AI is revolutionizing penetration testing, transforming traditionally manual exploits, once spanning several days, into automated systems that can now handle reconnaissance, scanning, and fuzzing in a matter of hours.
Automate your pentesting
For teams that deploy every day
Book a demo →
Learn more
"AI is already transforming pentesting. If
11 min read
Pentesting
Different types of penetration testing
Penetration testing, commonly known as pentesting, involves simulating a real attack on a server to assess its vulnerabilities against potential real-world attacks. While the primary goal is to emulate concrete threats, pentesting can extend beyond, offering insights into the potential consequences if confidential data were to fall into malicious hackers&
11 min read
Pentesting
GraphQL Pentesting: Thinking Outside the Box
The hardest part when pentesting any system is undoubtedly answering the question:
💡How should we think of that?
What is meant is "how outside-the-box thinking works?", and "how is a pentester meant to think outside the box?".
Although tackling this question might seem like a near
3 min read
Pentesting
GraphQL Pentesting 101: Part 2-Interaction Explained
A Pentester is usually expected to be a higher than average user in terms of interaction with an endpoint. For that reason, I decided to add an intermediary step between "Discovery" and "Exploiting" called "Interaction."
This article is part of the series "Pentesting
5 min read
Pentesting
GraphQL Discovery: Pentesting GraphQL 101 Part 1
Recent statistics say that you have queried at least one GraphQL endpoint today. For me, as a Penetration tester, it is just a matter of concern, especially since high-quality Pentesting guides/articles are scarce online, which only signals that GraphQL security is still rudimentary.
So I decided to start this
6 min read