Alexandra Charikova — Last Publications
Case Study
How Amp got its SOC 2 type II pentest evidence in hours
Amp is building the AI hiring team for frontline employers. Compliance was in the product from day one, which meant a pentest in year one. Here is how they scoped it, ran it in hours with Escape, and made sure they're ready for their SOC 2 Type II audit.
7 min read
Offensive Security
Horizon3.ai alternatives in 2026: Escape vs NodeZero and 4 more tools
Escape is the best Horizon3.ai alternative for continuous AI pentesting across APIs, web apps, and complex authentication, including regression testing, developer-ready remediation, and platform pricing suited for rapidly scaling orgs.
21 min read
Offensive Security
Escape vs Pentera: how each one proves exploitability (2026)
Most teams arrive at this comparison with the wrong framing: two automated penetration testing platforms, pick one.
Start with what Pentera actually is, because the comparisons that skip this get everything after it wrong. Pentera is an exposure validation platform with a key focus on network testing, and a good
14 min read
Offensive Security
Pentera Alternatives for Continuous Pentesting: 7 Competitors Compared In-Depth
Most security and IT teams we talk to who are evaluating Pentera alternatives are mostly happy with what Pentera does. What changed is the shape of the problem underneath them. It used to be a network problem. Now it is also a web application problem, and the tool hasn'
21 min read
Competitor Comparison
Escape vs StackHawk: full DAST comparison 2026
Last updated: August 2026. StackHawk's positioning changed materially in December 2025 with the launch of Business Logic Testing for APIs (Cross-profile BOLA/BFLA only), and again through 2026 with coding-agent integrations. This comparison reflects those changes.
20 min read
Application Security
Authenticated scanning behind OAuth, MFA, and CAPTCHA
Authenticated vulnerability scanning reaches where your real risk lives, behind the login, and it is the kind of security scanning most tools fail at.
A scanner hits the OAuth redirect, the MFA prompt, or the CAPTCHA, falls back to crawling as an anonymous visitor, and still finishes green, so the
10 min read
Offensive Security
Continuous penetration testing: what it means when the testing never stops
In late 2025, Anthropic disclosed the first documented cyberattack run largely by AI, a state-linked group that used Claude Code to run 80 to 90 percent of an espionage campaign on its own, at thousands of requests a second.
Offense now moves at machine speed while most defenses stay scheduled
10 min read
Announcement
Escape joins Anthropic’s Cyber Verification Program to advance AI-powered offensive security
Good news doesn't arrive alone. This month we joined not one frontier AI program but two! Yesterday we shared that Escape joined OpenAI's Trusted Access for Cyber. Today we're a verified member of Anthropic's Cyber Verification Program.
Both programs solve the same
2 min read
Announcement
Escape joins OpenAI’s Trusted Access for Cyber (TAC) to advance AI-powered offensive security
We've been approved for OpenAI's Trusted Access for Cyber preview.
For years we've been building toward one idea: offensive security that runs continuously inside engineering, instead of arriving twice a year as a PDF nobody reads past the executive summary. Business-logic DAST first, then
4 min read
Product updates
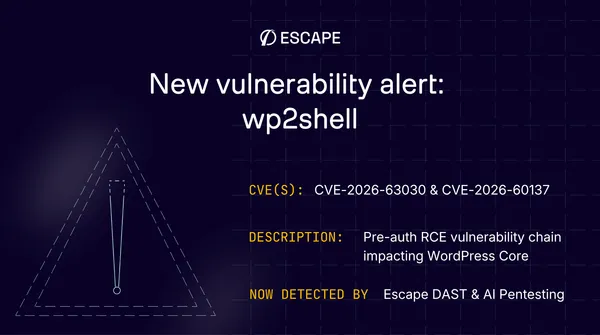
wp2shell (CVE-2026-63030 + CVE-2026-60137): WordPress pre-auth RCE, now detected by Escape
wp2shell is an unauthenticated RCE chain in WordPress core. It combines two separate vulnerabilities: CVE-2026-63030 and CVE-2026-60137. Escape detects it across DAST and AI Pentesting, confirms exploitability, and shows affected assets within its Attack Surface Management.
7 min read
DAST
Best AI DAST tools in 2026: ranked, compared, and reviewed for enterprise security teams
Every DAST vendor put "AI" on the homepage this year. The word now means ten different things to different tools, and even when discussing with analysts, they mention they give an "AI" badge when a certain capability checks the box. This is our attempt to fix
20 min read
Product updates
Fix issues with a prompt built for your coding agent
There's a translation step between a security finding and a fix, and it's usually done by hand.
Someone opens the issue, reads the description, checks the CVSS score, follows the link to the affected asset, works out which endpoint is actually involved, then writes all of
2 min read
Case Study
How Escape helped Bridgetech Group replace pentests with automated evidence
Security scanning that doesn't feel like going to the dentist. See how Bridgetech Group uses Escape for authenticated security testing and API scanning, replacing costly manual pentests with customer-ready security evidence for ISO 27001 and enterprise procurement.
6 min read
AI pentesting
Introducing Cascade: the multi-agent penetration testing that becomes an expert in your business
Escape CASCADE allows you to run deep, human-grade assessments across your whole attack surface, proves every finding with a working exploit, and gets more expert in your business with every engagement.
15 min read
API Security
Types of API security testing: a guide for enterprise teams
APIs account for a growing share of internet traffic, and attackers have noticed. In 2025, APIs accounted for 17% of all published security vulnerabilities, and 43% of newly added CISA Known Exploited Vulnerabilities were API-related, according to 2026 API ThreatStats Report. Between misconfigured authorization controls, exposed business logic, insecure API
22 min read
Alexandra Charikova — Events, Talks & Papers

Escape Blog Squad
-
 Alexandra Charikova
158 articles
-
 Antoine Carossio
38 articles
-
 Tristan Kalos
24 articles
-
 Sanjana Iyer
21 articles
-
 Achraf Ait Sidi Hammou
17 articles
-
 Gautier Ben Aïm
12 articles
-
 Escape - Offensive Security
11 articles
-
 Karim Rustom
8 articles
-
 Gwendal Mognier
8 articles
-
 Nohé Hinniger-Foray
8 articles
-
 Maxence Lecanu
8 articles
-
 Alexandre Tang
7 articles