
Maxence Lecanu — Last Publications
Research
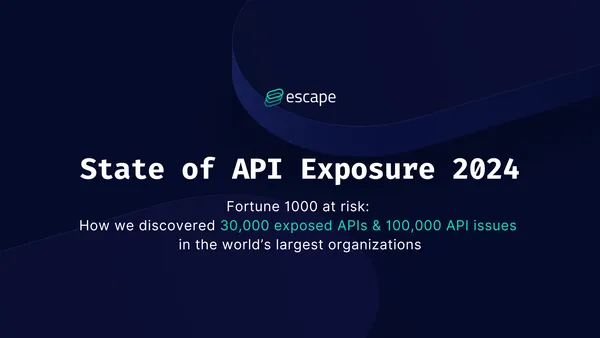
Fortune 1000 at risk: How we discovered 30k exposed APIs & 100k API vulnerabilities in the world’s largest organizations
Hey there!
Next week, social media will be flooded with Thanksgiving feasts (and Black Friday deals). But before you dive into the holiday shopping madness, the Escape team has prepared a special treat for you—not a Black Friday deal on Escape, of course, but rather some impressive findings on

6 min read
AppSec
Application security audit: an in-depth guide
Introduction
What are application security audits?
In information technologies departments, application security audits are systematic evaluations conducted to assess the security posture of an organization's applications.
Application security audits involve finding possible threats and determining the organization's attack surface. The different vectors that attackers can leverage
7 min read
Escape and Snyk officially partner to make GraphQL Security accessible to all developers!
Snyk and Escape provide developers with the ability to secure their GraphQL applications during the development lifecycle through an industry-leading end-to-end AppSec approach that includes SAST, DAST, and Cloud Security.
SAST and DAST for GraphQL Applications
Integrating Escape with Snyk means that a dynamic application security testing tool (DAST) and
3 min read
Open Source
Introducing 🪝 Mookme 🪝, a git hook manager for monorepos
Ever had troubles managing your git hooks in a monorepository ? We did too, so we created Mookme to solve our problems. Here is a git hook manager for dealing with different projects and languages, automated filtering, ease of configuration and setup.
5 min read
Escape Blog Squad
-
 Alexandra Charikova
158 articles
-
 Antoine Carossio
38 articles
-
 Tristan Kalos
23 articles
-
 Sanjana Iyer
21 articles
-
 Achraf Ait Sidi Hammou
17 articles
-
 Gautier Ben Aïm
12 articles
-
 Escape - Offensive Security
11 articles
-
 Karim Rustom
8 articles
-
 Gwendal Mognier
8 articles
-
 Nohé Hinniger-Foray
8 articles
-
 Maxence Lecanu
8 articles
-
 Alexandre Tang
7 articles