
Tristan Kalos — Last Publications
Escape raises $18M Series A to replace legacy scanners with AI agent-driven discovery, pentesting, and remediation
Led by Balderton Capital, with participation of Uncorrelated Ventures and existing investors IRIS and Y Combinator, the $18M Series A financing will accelerate our mission to multiply the impact of security teams through full-lifecycle offensive security.
4 min read
API Security
Reinventing API security: Why Escape is better than traditional traffic-based tools
We have been doing API Security wrong. Discover how the limitations of traffic-based API security tools might impact your security and why Escape's agentless technology is the best way to protect your APIs.
12 min read
API Security
Why security engineers need a new approach to identify business logic flaws
In the last decade, security scanners have evolved to identify common vulnerabilities like SQL injections.
But that’s just not enough anymore.
In 2024, data leaks in applications come from exploiting business logic flaws. In the next few years, applications will grow in size and number too fast, so the
8 min read
API Security
ASP.NET security best practices
Curious about the key strategies to ensure the security and reliability of your ASP.NET applications, including building APIs? Dive into our latest blog post, where we guide you through ASP.NET security best practices. Explore how these practices can not only enhance the security of your web applications but
7 min read
API Security
Escape API Security Checklist
Are you looking to make your API security program stronger? Do you sometimes find it challenging to spot and address security vulnerabilities effectively? You're not alone! Many security professionals like you face challenges in improving API security because technology and cyber threats keep changing. This makes ensuring strong
1 min read
API Security
Introducing business logic security testing for REST APIs
After one year and a half of approaching API security through the lenses of GraphQL, we are proud to introduce full support for REST API Security Testing in Escape, in addition to GraphQL 🚀
You like us on GraphQL. You will love us on REST.
It's been a ride
3 min read
GraphQL
What are Insecure Direct Object References (IDOR) in GraphQL, and how to fix them
As developers, ensuring the security of our applications is crucial. Insecure Direct Object References (IDOR) are common security vulnerabilities that occur when a system's internal implementation is exposed to users, allowing them to manipulate references to access unauthorized data. GraphQL, a powerful data query and manipulation language for
8 min read
GraphQL Query Cost Analysis
You must have understood that GraphQL is a very powerful language! Indeed, it is the query language used by the world's largest social network: Facebook (they created it in 2012 and made it public in 2015). However, these benefits and power also come with added complexity. This complexity
5 min read
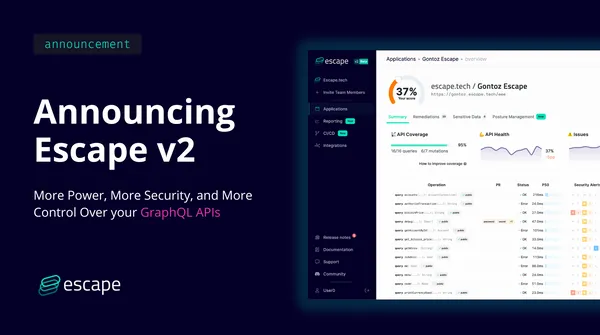
Introducing Escape v2: More Power, More Security, and More Control Over Your GraphQL APIs
tl;dr we are releasing the biggest update of our GraphQL Security platform so far. It includes numerous new features, including API Posture management, Reporting Overview, Better CI/CD Integration, GitHub SSO, and OWASP API Top 10 2023 Support.
Hello, Escape community! We are thrilled to announce the release of
3 min read
Announcement
APIRank.dev: we scanned and ranked 6031+ public APIs on the internet
tl;dr we scanned 6031+ public APIs on the internet with our in-house feedback driven exploration tech and ranked them using security, performance, reliability, and design criteria. The results are public on APIrank.dev. You can also request to index your own API for free and see how it compares
3 min read
What auditing 1000 endpoints told us about GraphQL Security Best Practices
This post is a write-up of a talk I gave at the GraphQL San Francisco Conference. You can find the video on youtube. If you are in the bay area do not forget to also join the GraphQL SF group on meetup.
It's commonly said that GraphQL is
9 min read
Startup Security
SaaS Startup Security 101 - A quick guide for building secure SaaS
Why should you care about security in a SaaS Startup?
1) To avoid expensive Data Leaks 🥷
A common misconception among startups is that only big corporations, or large scale-ups, are targeted by cyberattacks. Unfortunately, startups of all sizes can be targeted: from the 139 Million records leaked by Canva in
4 min read
Startup Security
The Russo-Ukrainian War: How the Fight for Democracy translates into Web API Security
In Ukraine, web APIs have demonstrated their value to achieve democratic progress through e-governance. Nonetheless, API security has revealed its vital nature in light of the cyberattacks launched by Russian state-sponsored hackers.
12 min read
DevSecOps
DevSecOps 101 Part 3: Scanning Live Web Applications with Nuclei scanner
This article is part of a series about integrating security tooling in the development process. You can find the rest of the articles here:
* Part 1: Detecting Insecure Dependencies (SCA)
* Part 2: Detecting Insecure Source Code (SAST)
* Part 4: Scanning Docker Images With Trivy
Note: This tutorial is based on
4 min read
Escape Blog Squad
-
 Alexandra Charikova
158 articles
-
 Antoine Carossio
37 articles
-
 Tristan Kalos
23 articles
-
 Sanjana Iyer
21 articles
-
 Achraf Ait Sidi Hammou
17 articles
-
 Gautier Ben Aïm
12 articles
-
 Escape - Offensive Security
11 articles
-
 Maxence Lecanu
8 articles
-
 Gwendal Mognier
8 articles
-
 Karim Rustom
8 articles
-
 Nohé Hinniger-Foray
8 articles
-
 Alexandre Tang
7 articles