
Antoine Carossio — Last Publications
AI pentesting
AI pentesting: what it is, and what it can actually find
Scanner with a chatbot
A real AI pentest
Login
Stops at the login page
Authenticates and tests behind it
Identities
Tests as one user
Holds several at once
Findings
A list it never reproduced
Every one reproduced before it files
13 min read
AI pentesting
What an external penetration test is and how one is actually run
Starts from
Asks
You get back
External pentest
The public internet, no access
Can an attacker get in at all
A demonstrated way in
Internal pentest
An assumed foothold
How far they get once inside
A lateral-movement path
Vulnerability scan
An asset list you supply
Is any known issue present
15 min read
Pentesting
How to build a continuous pentesting program
Introduction
An unpatched flaw is now the most common entry point for a breach, at 31%, ahead of stolen credentials at 13%, and the median time to fix one has crept up to 43 days (Verizon's 2026 DBIR). So an annual pentest is always a step behind, and
10 min read
Offensive Security
Penetration testing as a service (PTaaS), explained
Penetration testing as a service (PTaaS) made buying a pentest almost frictionless. You scope it in a portal, watch findings land on a live dashboard, and click a button to retest the fix, all without a single procurement call. But the test still runs on a schedule, so weeks after
10 min read
AI pentesting
Modern AI-powered Pentesting Tools In-Depth benchmark
If you're evaluating AI for offensive security right now, you're weighing two questions at once. The first: why not skip the tooling and point a frontier model at your apps yourself? The second: among the AI pentesting tools you could actually buy, which one earns the
15 min read
AI pentesting
Introducing Cascade: the multi-agent penetration testing that becomes an expert in your business
Escape CASCADE allows you to run deep, human-grade assessments across your whole attack surface, proves every finding with a working exploit, and gets more expert in your business with every engagement.
15 min read
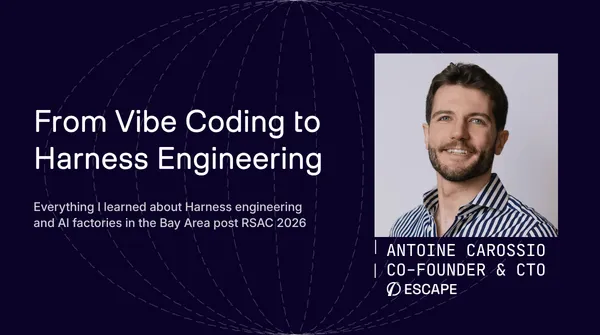
Everything I Learned About Harness Engineering and AI Factories in San Francisco (April 2026)
I spent the last week of March 2026 in San Francisco talking to CTOs, CPOs, and engineering leaders from companies of every size about how they actually build with AI agents today. I've met solo founders of pre-series A startups, I attended Y Combinator DevTool Day on March
15 min read
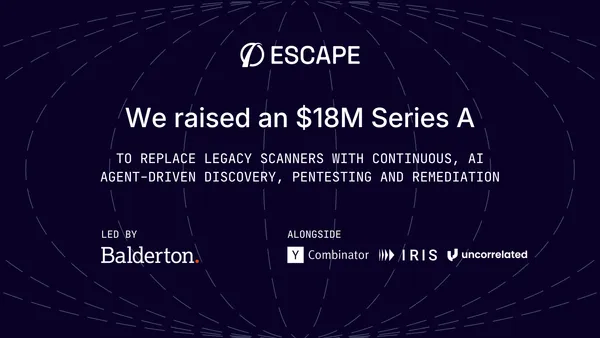
Escape raises $18M Series A to replace legacy scanners with AI agent-driven discovery, pentesting, and remediation
Led by Balderton Capital, with participation of Uncorrelated Ventures and existing investors IRIS and Y Combinator, the $18M Series A financing will accelerate our mission to multiply the impact of security teams through full-lifecycle offensive security.
4 min read
API Security
Escape vs Burp Suite: The Complete 2026 Comparison
Escape is the leading Burp Suite alternative for modern application security teams. Unlike Burp Suite, Escape automates business logic testing (IDORs, SSRFs, access control flaws), ensures faster scanning with fewer false positives, and provides remediation code snippets.
17 min read
API Security
Best API security testing tools in 2026: top picks, key features and expert comparison
When it comes to securing applications and APIs, the best API security testing tools are indispensable. These advanced solutions detect vulnerabilities by continuously scanning for weaknesses and simulating real-world attacks.
But how do you choose between all API security testing vendors?
Agentless API security tools are transforming application security by
28 min read
API Security
Escape's DAST proprietary Business Logic Security Testing algorithm: what makes it innovative
Testing APIs for Business Logic vulnerabilities is hard. Actually, this is a mission that old-school DAST solutions like ZAP (formerly OWASP ZAP) cannot handle.
I'm Antoine Carossio, passionate about Computer Science for more than 15 years now and cofounder & CTO of Escape. With my team, we'
10 min read
Pentesting
Best 8 AI Pentesting Tools in 2026
Explore the best AI pentesting tools in 2026. Learn how modern pentesting solutions detect business logic flaws and scale continuous security testing, so security teams can replace manual pentests with faster, more accurate coverage. Updated: August 2026
26 min read
Product updates
Introducing Multi-User Testing with Natural Language Queries in Escape DAST
Most of today’s SaaS structures are multi-tenant environments. Making sure that each tenant’s data and resources are securely isolated from others is critical. Weaknesses or misconfigurations in tenant isolation can lead to unauthorized access or data leaks between tenants, compromising the security of the entire system.
If you’
8 min read
Application Security
Gin & Juice Shop Benchmark: How DAST Tools Really Stack Up
This month, we set out to compare our DAST against some of the established names in Dynamic Application Security Testing. We’ve already benchmarked our scanner on vulnerable apps like VAMPI and DVGA, and now we’re putting it up against Qualys, ZAP, and Intruder (available in free trial) on
11 min read
Pentesting
Top Automated Penetration Testing Tools (2026)
Explore the best automated penetration testing tools of 2026. Learn how modern pentesting solutions detect business logic flaws and scale continuous security testing, so security teams can replace manual pentests with faster, more accurate coverage.
29 min read
Application Security
Top Vulnerability Scanning tools 2026
In 2026, vulnerability scanning tools are essential for modern security teams, but running a scan is rarely the hard part anymore. The real challenge is automating it at scale: across thousands of assets, spanning APIs, web applications, and cloud services, in environments that can change by the hour.
Security engineers
23 min read
How to Efficiently Implement DAST in CI/CD (2026 Guide)
Working with multiple customers implementing DAST in CI/CD has allowed us to learn a lot about what works, what doesn’t, and most importantly how to do it efficiently.
The truth is, it’s not about adopting just any tool. It's about making testing for runtime vulnerabilities
16 min read
GraphQL
The Paradox of Disabling GraphQL Introspection: Lessons from the Parse Server GraphQL API vulnerability
Last week, the security community was alerted to a vulnerability in Parse Server GraphQL API, which allowed public access to the GraphQL schema without requiring a session token or the master key. It is now identified as CVE-2025-53364.
So, the question comes up: Should we disable introspection entirely in production
4 min read
Application Security
The Alternative to Acunetix DAST: Escape DAST
Explore how Escape DAST serves as a superior alternative to Acunetix, offering advanced vulnerability detection for web applications and APIs, seamless integration into modern development workflows, and scalable solutions for enterprises.
8 min read
Escape Blog Squad
-
 Alexandra Charikova
158 articles
-
 Antoine Carossio
37 articles
-
 Tristan Kalos
23 articles
-
 Sanjana Iyer
21 articles
-
 Achraf Ait Sidi Hammou
17 articles
-
 Gautier Ben Aïm
12 articles
-
 Escape - Offensive Security
11 articles
-
 Maxence Lecanu
8 articles
-
 Gwendal Mognier
8 articles
-
 Karim Rustom
8 articles
-
 Nohé Hinniger-Foray
8 articles
-
 Alexandre Tang
7 articles