
Antoine Carossio — Last Publications
API Security
DAST is dead, why Business Logic Security Testing takes center stage
“DAST is dead” - that’s the phrase that appears every year on social media and in cybersecurity newsletters. But what if in 2024, it finally came true?
DAST, Dynamic Application Security Testing (even though we see a new terminology “Dynamic API Security Testing” popping up here and there within
8 min read
API Security
Introducing business logic security testing for REST APIs
After one year and a half of approaching API security through the lenses of GraphQL, we are proud to introduce full support for REST API Security Testing in Escape, in addition to GraphQL 🚀
You like us on GraphQL. You will love us on REST.
It's been a ride
3 min read
GraphQL Query Cost Analysis
You must have understood that GraphQL is a very powerful language! Indeed, it is the query language used by the world's largest social network: Facebook (they created it in 2012 and made it public in 2015). However, these benefits and power also come with added complexity. This complexity
5 min read
GraphQL
Introducing Seamless GraphQL Compliance
As your go-to partner in GraphQL Security, we at Escape are constantly innovating to simplify and streamline security for you. We're proud of our reputation for crafting modern, dynamic application security testing (DAST) tools tailored to GraphQL, beloved by developers and trusted by security teams worldwide. From comprehensive
3 min read
GraphQL
GraphQL Input Validation & Sanitization
Why input validation and sanitization are important in GraphQL?
GraphQL allows you to identify the data and validate inputs based on type information. By default, GraphQL Specification has the Int, Float, String, Boolean and ID Scalar types. But as a conscious API developer, you've probably come across situations
5 min read
Say Hi to SecureGPT: The free Security Tool for ChatGPT Developers
👋 tl;dr Are you a ChatGPT plugin developer who wants to ensure the safety and security of your creations? Look no further. Escape is thrilled to announce the release of SecureGPT, a lightning-fast and free security tool designed specifically for ChatGPT plugins. Secure your ChatGPT plugins in seconds with SecureGPT
2 min read
GraphQL Vulnerability
Demystifying GraphQL Security: A Comprehensive Guide to GraphQL Introspection
Whether or not to disable introspection in GraphQL has been a common debate among GraphQL developers since its inception. In this blog post, we will explain why completely disabling GraphQL introspection is not necessary and why it can be counterproductive.
I can't really find any good reasons for
5 min read
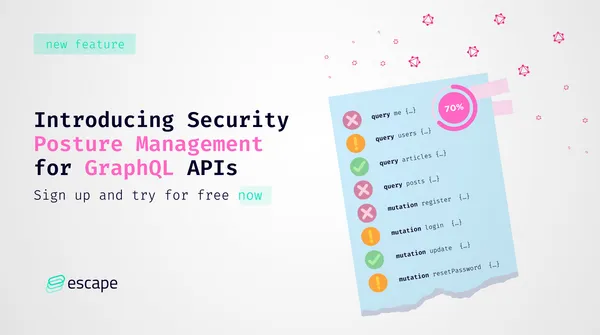
Introducing API Security Posture Management for GraphQL
tl;dr The Escape Team is excited to announce the release of its latest feature, API Security Posture Management for GraphQL. This feature proposes a single API Catalog view to explore the security, integrity, and performance of all GraphQL operations in one place. See it for yourself in action
With
2 min read
Introducing OpenAPI.Security, a free tool to quickly check the security of REST APIs
tl;dr We released OpenAPI.security, an online tool that performs a dozen of security tests on any given OpenAPI/Swagger-based API, with no signup or email required
Our team at Escape is mainly focused on securing GraphQL APIs. For this, we developed a new approach called feedback-driven API exploration,
1 min read
Escape is proud to be backed by Y Combinator!
Escape is proud to announce that we are backed by Y Combinator, the world's most prestigious and well-known startup accelerator, joining the YC Winter 23 batch!
Y Combinator, known for investing in and mentoring early-stage startups, has an impressive portfolio of successful companies such as Airbnb, Dropbox, and
2 min read
Access Control and Data Segregation in multi-tenant GraphQL applications
If you have ever worked with GraphQL, you must know that ensuring proper data segregation and access control is implemented correctly is a nightmare, especially in multi-tenant environments.
Access control and data segregation are critical aspects of any multi-tenant application where multiple customers or tenants share the same application instance.
6 min read
Announcing GraphQL Armor support for GraphQL Yoga 2 - Bringing security by default to GraphQL
We are utterly excited to introduce GraphQL Armor compatibility with Yoga 2.
When the GraphQL Ecosystem encounters Security
A few weeks ago, we released GraphQL Armor, an open-source middleware to add a security layer on top of GraphQL endpoints and mitigate common attacks.
GraphQL Armor blocks abusive requests by putting
2 min read
Escape Blog Squad
-
 Alexandra Charikova
158 articles
-
 Antoine Carossio
37 articles
-
 Tristan Kalos
23 articles
-
 Sanjana Iyer
21 articles
-
 Achraf Ait Sidi Hammou
17 articles
-
 Gautier Ben Aïm
12 articles
-
 Escape - Offensive Security
11 articles
-
 Maxence Lecanu
8 articles
-
 Gwendal Mognier
8 articles
-
 Karim Rustom
8 articles
-
 Nohé Hinniger-Foray
8 articles
-
 Alexandre Tang
7 articles