Alexandra Charikova — Last Publications
Podcast
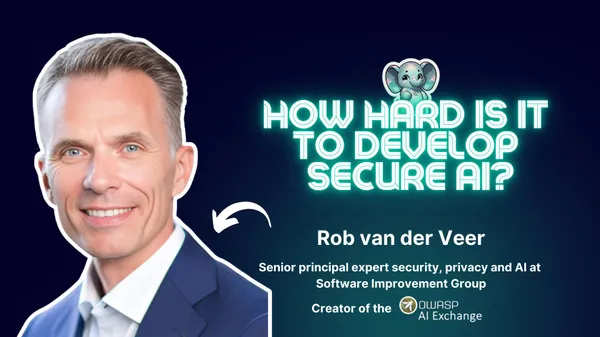
AI Security: How Hard Is It to Develop Secure AI?
This blog is based on our conversation with Rob van der Veer, Senior Principal Expert at the Software Improvement Group. It explores the complex challenges of developing secure AI systems and the critical role of governance and role segregation in AI security.
8 min read
Product updates
Product updates: Automated schema generation
We are excited to introduce our latest feature: automated schema generation for all your discovered APIs.
Having an OpenAPI Specification (OAS) is beneficial because it provides a standardized, machine-readable format for documenting RESTful APIs, promoting clarity and consistency across different services. with an OAS, developers can leverage a plethora of
4 min read
Application Security
How to secure non-human identities? with Andrew Wilder and Amir Shaked
This blog is based on our conversation with Andrew Wilder, Retained Chief Security Officer at Community Veterinary Partners and Amir Shaked, VP of R&D at Oasis Security. It covers the unique challenges of securing non-human identities.
8 min read
Application Security
Software Supply Chain Risks ⎪Cassie Crossley (VP Supply Chain Security, Schneider Electric)
This blog is based on our conversation with Cassie Crossley, Vice President of Supply Chain Security at Schneider Electric. It covers the unique challenges of software supply chain security.
10 min read
GraphQL Security
How to secure GraphQL APIs: challenges and best practices
GraphQL APIs, while offering robust features and flexibility, present unique security challenges compared to traditional REST APIs. This article delves into the complexities of securing GraphQL APIs, highlighting common vulnerabilities and providing a comprehensive guide to best practices for building secure GraphQL apps.
A visual learner? Check out our latest
6 min read
Custom Security Tests
Are custom security tests a product security superpower? ⎜Keshav Malik (LinkedIn)
Welcome to the Elephant in AppSec, the podcast to explore, challenge, and boldly face the AppSec Elephants in the room.
In this article, we'll cover the main takeaways from our conversation with Keshav Malik, a senior Product Security Engineer at LinkedIn. Our goal is to help you understand
5 min read
API Security
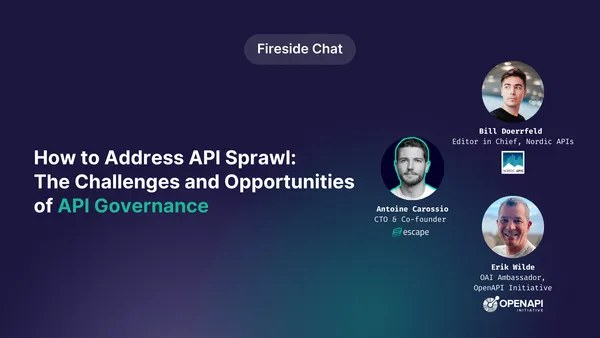
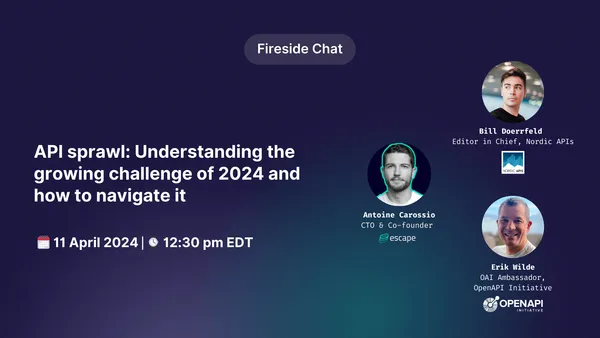
[Fireside Chat] API sprawl: Understanding the growing challenge of 2024 and how to navigate it
Hey there 👋
Join Bill Doerrfeld, tech journalist and Editor-in-Chief at the Nordic APIs blog, Erik Wilde, OAI Ambassador at the OpenAPI Initiative, and Antoine Carossio, CTO and co-founder at Escape, for a fireside chat on the challenges of API sprawl.
Sign me up!
During this live discussion, they will explore:
1 min read
API Security
Workshop "How to write custom security tests" - Main Takeaways
Organizations are constantly seeking ways to improve their defenses against business logic vulnerabilities. These vulnerabilities, often difficult to detect, can lead to significant security breaches if left unchecked. To address this challenge, we've introduced a new feature within our platform that empowers teams to create custom business logic
5 min read
Podcast
The art and science of product security: A deep dive with Jacob Salassi
Welcome to the Elephant in AppSec, the podcast to explore, challenge, and boldly face the AppSec Elephants in the room.
Today we’re excited to have an amazing guest, Jacob Salassi, join us. You can find the main takeaways from our conversation with Jacob just down below!
Jacob's
6 min read
Product updates
Introducing Escape rules - Rules that adapt for you
Today, we’re launching customization improvements to Escape’s automated testing capabilities. With Escape Rules, you can now write custom security tests that do not require any maintenance and adapt to each newly discovered API and each new version of your existing APIs.
💡Want to learn how to write custom
4 min read
Application Security
Building security training for developers in 2024: Is it really worth it and how to proceed?
If you're a security engineer, the chances that you've struggled with your development team to implement secure coding practices are high. If you don't have the right culture in your organization, it might be even harder. Developers consider you as an adversary, rather than
9 min read
API Security
Sensitive data exposure: How to prevent it and where do we stand in 2025
Do you fully grasp the magnitude of sensitive data exposure? It stands as one of the most prevalent and menacing threats to organizational security in 2025.
Picture any information quintessential to an individual's or a company's identity and safety - personal, financial, health, or trade secrets.
9 min read
Alexandra Charikova — Events, Talks & Papers

Escape Blog Squad
-
 Alexandra Charikova
158 articles
-
 Antoine Carossio
38 articles
-
 Tristan Kalos
24 articles
-
 Sanjana Iyer
21 articles
-
 Achraf Ait Sidi Hammou
17 articles
-
 Gautier Ben Aïm
12 articles
-
 Escape - Offensive Security
11 articles
-
 Karim Rustom
8 articles
-
 Gwendal Mognier
8 articles
-
 Nohé Hinniger-Foray
8 articles
-
 Maxence Lecanu
8 articles
-
 Alexandre Tang
7 articles