Alexandra Charikova — Last Publications
API Discovery
What is a Shadow API? Understanding the risks and strategies to prevent their sprawl
API Sprawl is a serious challenge in 2024, and shadow APIs are part of the problem. But do you actually know what Shadow APIs are and why they represent danger for organizations?
With the ever-increasing number of exposed APIs, the pain of not being able to gain visibility over all
6 min read
Podcast
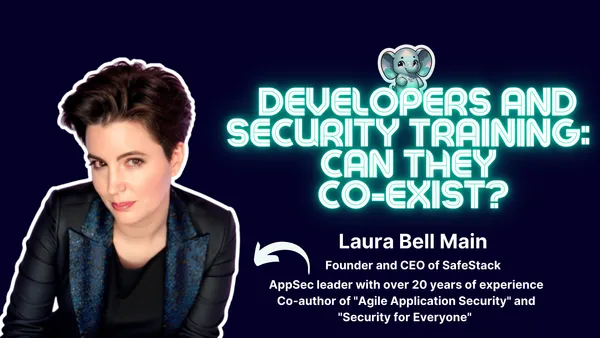
Developers and security training: can they co-exist?⎜Laura Bell Main
Welcome to the Elephant in AppSec, the podcast to explore, challenge, and boldly face the AppSec Elephants in the room.
Today, we’re excited to have an amazing guest, Laura Bell Main, join us.
With over 20 years in software development and application security, Laura is the co-founder and CEO
2 min read
API Security
API security for PCI compliance: A deep dive into the PCI DSS 4.0 impact
There are more than 50 new requirements in PCI DSS v4.0 – do you know which ones apply to you and what you need to do to meet them? The March deadline is approaching, and we want to ensure you're fully prepared for the changes ahead.
The deadline
10 min read
API Security
How to secure gRPC APIs
Looking for ways to secure gRPC APIs? Don't worry, we've got you covered!
In this article, we will be exploring the topic of gRPC security and its importance in ensuring the security of API endpoints. We will also discuss the role of dynamic application security testing
8 min read
Podcast
AppSec vendors and CISOs: a love-hate relationship? ⎜Olivia Rose
Welcome to the Elephant in AppSec, the podcast to explore, challenge, and boldly face the AppSec Elephants in the room.
Today, we're joined by an amazing guest, Olivia Rose.
Olivia is an executive leader with more than 20 years of dedicated experience, having served as the former CISO
1 min read
Application Security
4 lessons from recent application security case studies
Every organization, no matter how big or small, if it's dependent on the software (which is impossible not to be in the modern world), must prioritize software security. Interested in enhancing yours? Want to know how real-world application security challenges are tackled? Let's get straight to
6 min read
API Security
API gateway security: 8 best practices
Are your API gateways well secured? If you have doubts, then they are not. API gateways play a large role in securing the flow of data between clients and backend services. But with the surge in API adoption (nearly 90% of developers are using APIs) and the increasing sophistication of
6 min read
API Security
Methodology: How we discovered over 18,000 API secret tokens
Hey there!
It's just the beginning of the year, but our security research team has been working hard to identify current API security challenges.
So for the Escape team, January went under the tagline "API secret sprawl" (we thought it was more fun than"Dry
6 min read
Podcast
Security training: Necessary investment or overrated expense?⎥Mel Reyes (Global CEO, CIO, CISO, & CTO with 30 years of experience)
Welcome to the Elephant in AppSec, the podcast to explore, challenge, and boldly face the AppSec Elephants in the room.
Today, we’re excited to have an amazing guest, Mel Reyes, join us.
Mel has navigated through two IPOs and three M&As, worked with several startups, Pepsi and
1 min read
Podcast
What is ASPM: A breakdown of the current state and its future⎥James Berthoty (Security at PagerDuty)
Welcome to the Elephant in AppSec, the podcast to explore, challenge, and boldly face the AppSec Elephants in the room.
Today, we're excited to have an amazing guest, James Berthoty, joining us.
James has been in technology for over 10 years across engineering and security. An early advocate
18 min read
Podcast
SCADA systems: How secure are the systems running our infrastructure?⎥Malav Vyas (Security Researcher at Palo Alto Networks)
Welcome to the Elephant in AppSec, the podcast to explore, challenge, and boldly face the AppSec Elephants in the room.
Today, we're excited to have an amazing guest, Malav Vyas, joining us.
Malav is a security researcher at Palo Alto Networks, passionate about exploiting and securing systems.
Security
14 min read
Application Security
Threat modeling: the future of cybersecurity or another buzzword⎥Derek Fisher (author of The Application Security Handbook)
Welcome to the Elephant in AppSec, the podcast to explore, challenge, and boldly face the AppSec Elephants in the room.
Today we’re excited to have an amazing guest, Derek Fisher, joining us.
Derek is a cybersecurity leader, a speaker on various cybersecurity topics, and author of the famous “The
25 min read
Application Security
What is business logic, and why it's important for application security
Is understanding business logic a critical component of application security? Absolutely. In the world of cybersecurity, business logic is more than just a set of operational directives. It serves as the crucial bridge between an application's technical function and its alignment with strategic business goals.
More than that,
6 min read
Alexandra Charikova — Events, Talks & Papers

Escape Blog Squad
-
 Alexandra Charikova
158 articles
-
 Antoine Carossio
38 articles
-
 Tristan Kalos
24 articles
-
 Sanjana Iyer
21 articles
-
 Achraf Ait Sidi Hammou
17 articles
-
 Gautier Ben Aïm
12 articles
-
 Escape - Offensive Security
11 articles
-
 Karim Rustom
8 articles
-
 Gwendal Mognier
8 articles
-
 Nohé Hinniger-Foray
8 articles
-
 Maxence Lecanu
8 articles
-
 Alexandre Tang
7 articles