Application Security
121 posts
Podcast
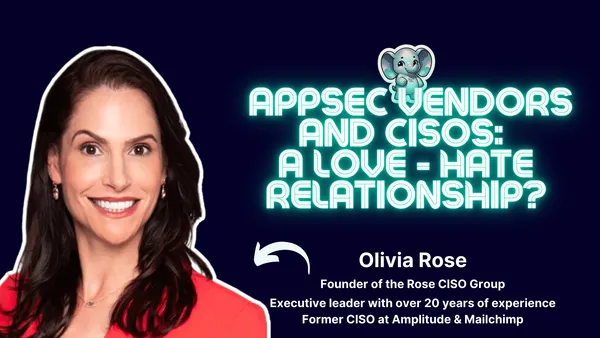
AppSec vendors and CISOs: a love-hate relationship? ⎜Olivia Rose
Welcome to the Elephant in AppSec, the podcast to explore, challenge, and boldly face the AppSec Elephants in the room.
Today, we're joined by an amazing guest, Olivia Rose.
Olivia is an executive leader with more than 20 years of dedicated experience, having served as the former CISO
1 min read
Application Security
4 lessons from recent application security case studies
Every organization, no matter how big or small, if it's dependent on the software (which is impossible not to be in the modern world), must prioritize software security. Interested in enhancing yours? Want to know how real-world application security challenges are tackled? Let's get straight to
6 min read
API Security
Methodology: How we discovered over 18,000 API secret tokens
Hey there!
It's just the beginning of the year, but our security research team has been working hard to identify current API security challenges.
So for the Escape team, January went under the tagline "API secret sprawl" (we thought it was more fun than"Dry
6 min read
Podcast
Security training: Necessary investment or overrated expense?⎥Mel Reyes (Global CEO, CIO, CISO, & CTO with 30 years of experience)
Welcome to the Elephant in AppSec, the podcast to explore, challenge, and boldly face the AppSec Elephants in the room.
Today, we’re excited to have an amazing guest, Mel Reyes, join us.
Mel has navigated through two IPOs and three M&As, worked with several startups, Pepsi and
1 min read
Podcast
What is ASPM: A breakdown of the current state and its future⎥James Berthoty (Security at PagerDuty)
Welcome to the Elephant in AppSec, the podcast to explore, challenge, and boldly face the AppSec Elephants in the room.
Today, we're excited to have an amazing guest, James Berthoty, joining us.
James has been in technology for over 10 years across engineering and security. An early advocate
18 min read
API Security
How to build secure APIs with Ruby on Rails: Security guide
Are your Ruby on Rails APIs as secure as they could be? In today's world, where digital security is no longer an option, ensuring the robustness of your APIs is crucial. If you find yourself uncertain when attempting to answer this question, then this guide is for you.
13 min read
Flask security
Best practices to protect your Flask applications
Want to know how to protect your Flask applications? Dive into our latest blog post, where we guide you through the best practices for Flask security. Explore how these techniques can not only enhance the security of your web applications but also bring tangible benefits to your development journey.
In
12 min read
Podcast
SCADA systems: How secure are the systems running our infrastructure?⎥Malav Vyas (Security Researcher at Palo Alto Networks)
Welcome to the Elephant in AppSec, the podcast to explore, challenge, and boldly face the AppSec Elephants in the room.
Today, we're excited to have an amazing guest, Malav Vyas, joining us.
Malav is a security researcher at Palo Alto Networks, passionate about exploiting and securing systems.
Security
14 min read
Application Security
Threat modeling: the future of cybersecurity or another buzzword⎥Derek Fisher (author of The Application Security Handbook)
Welcome to the Elephant in AppSec, the podcast to explore, challenge, and boldly face the AppSec Elephants in the room.
Today we’re excited to have an amazing guest, Derek Fisher, joining us.
Derek is a cybersecurity leader, a speaker on various cybersecurity topics, and author of the famous “The
25 min read
API Security
ASP.NET security best practices
Curious about the key strategies to ensure the security and reliability of your ASP.NET applications, including building APIs? Dive into our latest blog post, where we guide you through ASP.NET security best practices. Explore how these practices can not only enhance the security of your web applications but
7 min read
Application Security
What is business logic, and why it's important for application security
Is understanding business logic a critical component of application security? Absolutely. In the world of cybersecurity, business logic is more than just a set of operational directives. It serves as the crucial bridge between an application's technical function and its alignment with strategic business goals.
More than that,
6 min read
Application Security
SAST vs DAST: how to make the choice and combine them effectively
Should you choose between SAST and DAST? Perhaps the real question is, why not use both in your application security strategy? Let's be honest—vulnerabilities are often discovered when it's too late. No matter how well developers follow secure coding guidelines, it's impossible to
8 min read
Application Security
Vulnerability Management Lifecycle: 5 Steps and Best Practices
Maintaining robust security of your organization is not just crucial in 2023 – it's a survival strategy. The recent data breach at 23andMe in October 2023 is a case in point. This incident, where a credential-stuffing attack led to unauthorized access to customer accounts, underscores a harsh reality. Even
15 min read
Application Security
How to establish an application security policy
As organizations increasingly rely on web and mobile applications to conduct business, robust application security has become paramount. Cyberattacks are on the rise, and without adequate protection, businesses risk losing sensitive data, revenue, and reputational damage. Having an application security policy in place is the first line of defense against
14 min read
API Security
Escape API Security Checklist
Are you looking to make your API security program stronger? Do you sometimes find it challenging to spot and address security vulnerabilities effectively? You're not alone! Many security professionals like you face challenges in improving API security because technology and cyber threats keep changing. This makes ensuring strong
1 min read
API Discovery
What is API discovery, and how does it work?
Ever wondered how applications effortlessly communicate and collaborate, seamlessly sharing data and functionalities? Enter API discovery – the game-changer in modern development. What if finding and connecting with APIs was as intuitive as flipping a switch?
As the newly appointed security engineer, you quickly realize the sprawling web of APIs that
6 min read