Application Security
121 posts
API Security
Reinventing API security: Why Escape is better than traditional traffic-based tools
We have been doing API Security wrong. Discover how the limitations of traffic-based API security tools might impact your security and why Escape's agentless technology is the best way to protect your APIs.
12 min read
API Security
Limitations of current automatic specification generation tools
Have you ever wondered how automatic specification generation can streamline API security scanning? By significantly reducing the manual effort involved in creating and maintaining API specifications, automated tools offer clear benefits in terms of scan accuracy and setup time.
Yet, many existing tools on the market have notable limitations. Understanding
5 min read
Application Security
How to secure non-human identities? with Andrew Wilder and Amir Shaked
This blog is based on our conversation with Andrew Wilder, Retained Chief Security Officer at Community Veterinary Partners and Amir Shaked, VP of R&D at Oasis Security. It covers the unique challenges of securing non-human identities.
8 min read
Application Security
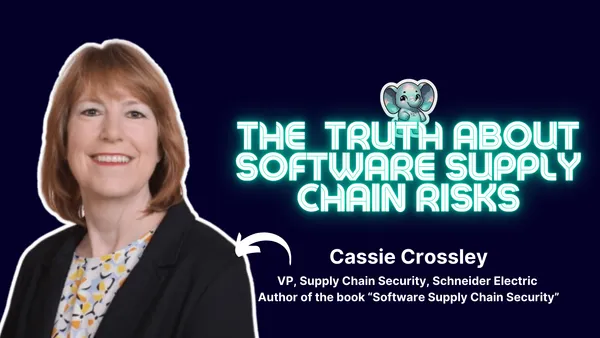
Software Supply Chain Risks ⎪Cassie Crossley (VP Supply Chain Security, Schneider Electric)
This blog is based on our conversation with Cassie Crossley, Vice President of Supply Chain Security at Schneider Electric. It covers the unique challenges of software supply chain security.
10 min read
API Security
DAST is dead, why Business Logic Security Testing takes center stage
“DAST is dead” - that’s the phrase that appears every year on social media and in cybersecurity newsletters. But what if in 2024, it finally came true?
DAST, Dynamic Application Security Testing (even though we see a new terminology “Dynamic API Security Testing” popping up here and there within
8 min read
Custom Security Tests
Are custom security tests a product security superpower? ⎜Keshav Malik (LinkedIn)
Welcome to the Elephant in AppSec, the podcast to explore, challenge, and boldly face the AppSec Elephants in the room.
In this article, we'll cover the main takeaways from our conversation with Keshav Malik, a senior Product Security Engineer at LinkedIn. Our goal is to help you understand
5 min read
API Security
Workshop "How to write custom security tests" - Main Takeaways
Organizations are constantly seeking ways to improve their defenses against business logic vulnerabilities. These vulnerabilities, often difficult to detect, can lead to significant security breaches if left unchecked. To address this challenge, we've introduced a new feature within our platform that empowers teams to create custom business logic
5 min read
API Security
Why security engineers need a new approach to identify business logic flaws
In the last decade, security scanners have evolved to identify common vulnerabilities like SQL injections.
But that’s just not enough anymore.
In 2024, data leaks in applications come from exploiting business logic flaws. In the next few years, applications will grow in size and number too fast, so the
8 min read
Podcast
The art and science of product security: A deep dive with Jacob Salassi
Welcome to the Elephant in AppSec, the podcast to explore, challenge, and boldly face the AppSec Elephants in the room.
Today we’re excited to have an amazing guest, Jacob Salassi, join us. You can find the main takeaways from our conversation with Jacob just down below!
Jacob's
6 min read
Application Security
Building security training for developers in 2024: Is it really worth it and how to proceed?
If you're a security engineer, the chances that you've struggled with your development team to implement secure coding practices are high. If you don't have the right culture in your organization, it might be even harder. Developers consider you as an adversary, rather than
9 min read
Podcast
Developers and security training: can they co-exist?⎜Laura Bell Main
Welcome to the Elephant in AppSec, the podcast to explore, challenge, and boldly face the AppSec Elephants in the room.
Today, we’re excited to have an amazing guest, Laura Bell Main, join us.
With over 20 years in software development and application security, Laura is the co-founder and CEO
2 min read
API Security
API security for PCI compliance: A deep dive into the PCI DSS 4.0 impact
There are more than 50 new requirements in PCI DSS v4.0 – do you know which ones apply to you and what you need to do to meet them? The March deadline is approaching, and we want to ensure you're fully prepared for the changes ahead.
The deadline
10 min read
API Security
How to secure gRPC APIs
Looking for ways to secure gRPC APIs? Don't worry, we've got you covered!
In this article, we will be exploring the topic of gRPC security and its importance in ensuring the security of API endpoints. We will also discuss the role of dynamic application security testing
8 min read