Application Security
121 posts
Application Security
Two Major Updates from The Elephant in AppSec Conference: Agenda Is Live & Partnership with InfoSecMap
Two exciting updates in the Elephant in AppSec corner!
1. The Elephant in AppSec Conference 2026 Agenda Is Now Live
The agenda for the 2026 edition of The Elephant in AppSec Conference is officially published. This year’s program brings together a lineup of speakers who aren’t afraid to
3 min read
Pentesting
Best 8 AI Pentesting Tools in 2026
Explore the best AI pentesting tools in 2026. Learn how modern pentesting solutions detect business logic flaws and scale continuous security testing, so security teams can replace manual pentests with faster, more accurate coverage. Updated: August 2026
26 min read
Case Study
From Complex Authentication to Confident Coverage: How Applied Systems Transformed Their AppSec with Escape
In a recent webinar on "From Business Logic Vulnerabilities to Actionable Insights: AI-powered Pentesting + ASM in Action," Andrew Orr Erwing, Manager of Security Engineering (AppSec) at Applied Systems, shared his team's journey in modernizing their application security approach.
For organizations that have grown rapidly through acquisitions,
4 min read
Research
Methodology: How we discovered over 2k high-impact vulnerabilities in apps built with vibe coding platforms
Hey there,
With Halloween around the corner, what’s scarier for organizations than vulnerabilities in their web applications?
And it's even scarier when the development of these applications is in the hands of users not familiar with security practices.
This year, the Escape research team has focused on
10 min read
Product updates
Introducing Multi-User Testing with Natural Language Queries in Escape DAST
Most of today’s SaaS structures are multi-tenant environments. Making sure that each tenant’s data and resources are securely isolated from others is critical. Weaknesses or misconfigurations in tenant isolation can lead to unauthorized access or data leaks between tenants, compromising the security of the entire system.
If you’
8 min read
Competitor Comparison
Detectify alternatives in 2026: Escape vs Detectify and 4 more tools
Looking for a Detectify alternative? Compare Escape vs Detectify on API and app security, pricing, G2 ratings, and key features. See why security teams choose this application security scanner for business logic testing and internal app scanning.
19 min read
Application Security
Gin & Juice Shop Benchmark: How DAST Tools Really Stack Up
This month, we set out to compare our DAST against some of the established names in Dynamic Application Security Testing. We’ve already benchmarked our scanner on vulnerable apps like VAMPI and DVGA, and now we’re putting it up against Qualys, ZAP, and Intruder (available in free trial) on
11 min read
Attack Surface Management
Why context is king in Attack Surface Management (ASM): Key insights from my conversations with security leaders
When I launched this research, my goal was to understand the current perception of security practitioners regarding Attack Surface Management (ASM) solutions. Unlike in my previous article, "What is wrong with the current state of DAST?" I didn't start with an overall negative perception from the
8 min read
Application Security
[Webinar] From Business Logic Vulnerabilities to Actionable Insights: AI-powered Pentesting + ASM in Action
For years, security teams have relied on human penetration testers to uncover critical vulnerabilities hidden in complex business logic. These flaws are subtle, context-dependent, and unique to every system’s workflow. Even modern scanners struggle to capture them, focusing only on a limited range of vulnerabilities displayed in their UI.
2 min read
Application Security
Top Vulnerability Scanning tools 2026
In 2026, vulnerability scanning tools are essential for modern security teams, but running a scan is rarely the hard part anymore. The real challenge is automating it at scale: across thousands of assets, spanning APIs, web applications, and cloud services, in environments that can change by the hour.
Security engineers
23 min read
Application Security
How to Automate Your Penetration Testing?
AI is revolutionizing penetration testing, transforming traditionally manual exploits, once spanning several days, into automated systems that can now handle reconnaissance, scanning, and fuzzing in a matter of hours.
Automate your pentesting
For teams that deploy every day
Book a demo →
Learn more
"AI is already transforming pentesting. If
11 min read
Application Security
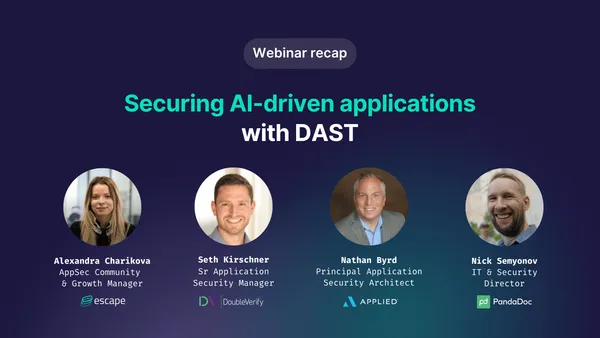
Feedback From Escape Customers: Securing AI-Driven Applications with DAST
“You ask the developer why they wrote the code the way that they did, and they don’t have an answer anymore. They’re like, ‘Well, AI wrote it.” - Seth Kirschner, DoubleVerify
AI is now deeply embedded in software development workflows, and the implications for application security teams are
11 min read
Application Security
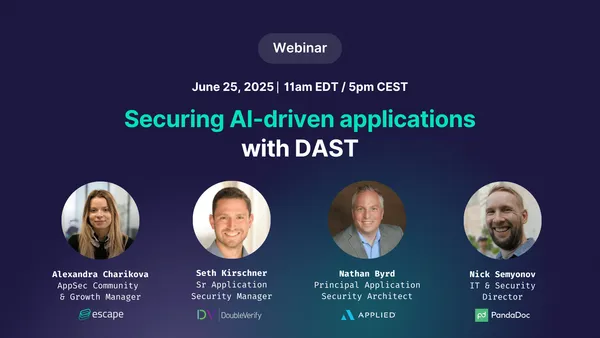
[Webinar] Securing AI-driven applications with DAST
Join us for a live webinar with application security experts and Escape clients - Seth Kirschner (DoubleVerify), Nathan Byrd (Applied Systems), Nick Semyonov (PandaDoc), as they break down how their teams are rethinking testing strategies to keep up with AI-influenced codebases.
1 min read
Product updates
From Alert to Action: Escape’s Jira Integration Explained
Ticketing systems are an essential part of modern DevSecOps. They orchestrate cross-functional collaboration, ensure accountability, and drive issues to resolution. But in application security, the value of ticketing hinges on one critical factor: context.
Too often, security tools generate vague alerts or findings without right context associated with them that
5 min read