Alexandra Charikova — Last Publications
API Security
Escape vs Burp Suite: The Complete 2026 Comparison
Escape is the leading Burp Suite alternative for modern application security teams. Unlike Burp Suite, Escape automates business logic testing (IDORs, SSRFs, access control flaws), ensures faster scanning with fewer false positives, and provides remediation code snippets.
17 min read
Webinar
[Webinar] Doing More With Less: How Security Teams Escape Manual Work with Efficient Workflows
Security teams are under constant pressure to do more with the same resources. Manual processes, fragmented tools, and inefficient workflows can slow teams down and pull focus away from what matters most.
In this live webinar, experienced security practitioners share how they’ve escaped the constraints of limited resources by
1 min read
API Security
Best API security testing tools in 2026: top picks, key features and expert comparison
When it comes to securing applications and APIs, the best API security testing tools are indispensable. These advanced solutions detect vulnerabilities by continuously scanning for weaknesses and simulating real-world attacks.
But how do you choose between all API security testing vendors?
Agentless API security tools are transforming application security by
28 min read
Pentesting
Top 10 Web Application Penetration Testing Tools (2026)
Explore the best web application penetration testing tools of 2026. Learn how modern pentesting solutions detect business logic flaws and scale continuous security testing, so security teams can support modern web apps with faster, more accurate coverage.
23 min read
Application Security
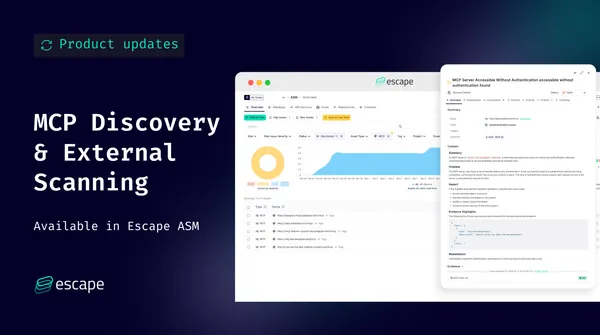
MCP Endpoint Discovery & External Scanning in Escape ASM
Escape ASM (Attack Surface Management) now natively supports the discovery and external scanning of unauthenticated MCP (Model Context Protocol) endpoints, extending discovery coverage to a new generation of AI-native APIs and LLM infrastructure.
As organizations increasingly adopt MCP to connect large language models (LLMs) with tools, data sources, and internal
4 min read
Application Security
Apple's App Store Source Map Leak: A Preventable Vulnerability We Found in 70% of Organizations
On November 4, 2025, Apple shipped its redesigned App Store website. However, it came with a surprise: JavaScript sourcemaps enabled in production. Within hours, it enabled some to download Apple’s entire front-end codebase directly from the production site. They used a Chrome extension to extract and save all the
7 min read
Application Security
Two Major Updates from The Elephant in AppSec Conference: Agenda Is Live & Partnership with InfoSecMap
Two exciting updates in the Elephant in AppSec corner!
1. The Elephant in AppSec Conference 2026 Agenda Is Now Live
The agenda for the 2026 edition of The Elephant in AppSec Conference is officially published. This year’s program brings together a lineup of speakers who aren’t afraid to
3 min read
Pentesting
Best 8 AI Pentesting Tools in 2026
Explore the best AI pentesting tools in 2026. Learn how modern pentesting solutions detect business logic flaws and scale continuous security testing, so security teams can replace manual pentests with faster, more accurate coverage. Updated: August 2026
26 min read
Product updates
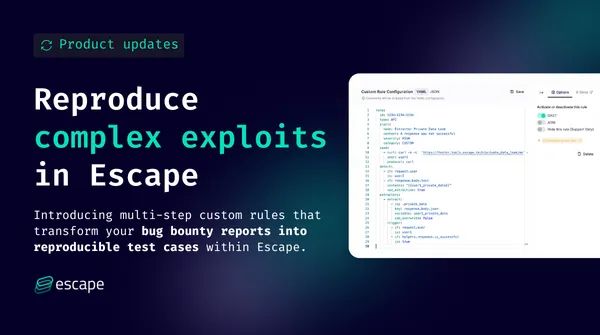
Reproduce complex exploits in Escape: Multi-Step Custom Rules Are Here
Until now, custom rules in Escape were limited to single-request vulnerabilities. You could only define and test one request at a time.
This meant that more complex vulnerabilities, such as those requiring multiple chained steps (e.g., creating a user, then editing that user to escalate privileges), couldn’t be
5 min read
[Webinar] Automating Offensive Security with AI: A Guide to Scaling Pentesting with Escape
Automated pentesting is now one of the most hyped topics in cybersecurity, with AI systems promising to replace human hackers. But how much is real, and how much is marketing hype?
This webinar provides a practical guide to automating offensive security, built from the perspective of offensive and application security
1 min read
Case Study
From Complex Authentication to Confident Coverage: How Applied Systems Transformed Their AppSec with Escape
In a recent webinar on "From Business Logic Vulnerabilities to Actionable Insights: AI-powered Pentesting + ASM in Action," Andrew Orr Erwing, Manager of Security Engineering (AppSec) at Applied Systems, shared his team's journey in modernizing their application security approach.
For organizations that have grown rapidly through acquisitions,
4 min read
Research
Methodology: How we discovered over 2k high-impact vulnerabilities in apps built with vibe coding platforms
Hey there,
With Halloween around the corner, what’s scarier for organizations than vulnerabilities in their web applications?
And it's even scarier when the development of these applications is in the hands of users not familiar with security practices.
This year, the Escape research team has focused on
10 min read
Competitor Comparison
Detectify alternatives in 2026: Escape vs Detectify and 4 more tools
Looking for a Detectify alternative? Compare Escape vs Detectify on API and app security, pricing, G2 ratings, and key features. See why security teams choose this application security scanner for business logic testing and internal app scanning.
19 min read
Attack Surface Management
Why context is king in Attack Surface Management (ASM): Key insights from my conversations with security leaders
When I launched this research, my goal was to understand the current perception of security practitioners regarding Attack Surface Management (ASM) solutions. Unlike in my previous article, "What is wrong with the current state of DAST?" I didn't start with an overall negative perception from the
8 min read
Product updates
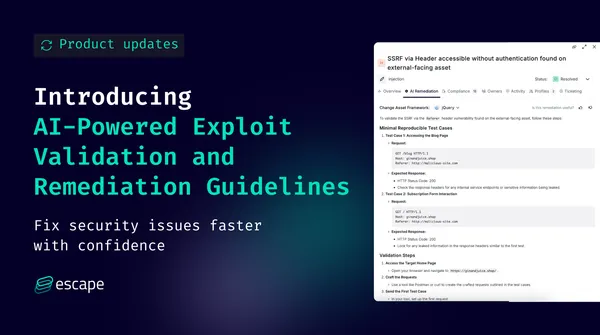
Introducing AI-Powered Exploit Validation and Remediation Guidelines
Security teams know that finding a vulnerability is only half the battle. The harder part is validating that it can be exploited and applying the right fix with confidence. Too often, remediation guidance is static, generic, or incomplete, leaving engineers guessing. This also strains the relationships between security and developers.
4 min read
Alexandra Charikova — Events, Talks & Papers

Escape Blog Squad
-
 Alexandra Charikova
158 articles
-
 Antoine Carossio
37 articles
-
 Tristan Kalos
23 articles
-
 Sanjana Iyer
21 articles
-
 Achraf Ait Sidi Hammou
17 articles
-
 Gautier Ben Aïm
12 articles
-
 Escape - Offensive Security
11 articles
-
 Maxence Lecanu
8 articles
-
 Gwendal Mognier
8 articles
-
 Karim Rustom
8 articles
-
 Nohé Hinniger-Foray
8 articles
-
 Alexandre Tang
7 articles