Sanjana Iyer

Sanjana is a Growth Marketer at Escape, with a background in marketing in finance and a growing focus on API and application security. She constantly contributes research and insights into the current landscape of AppSec tools and trends.

Sanjana Iyer

Sanjana Iyer — Last Publications
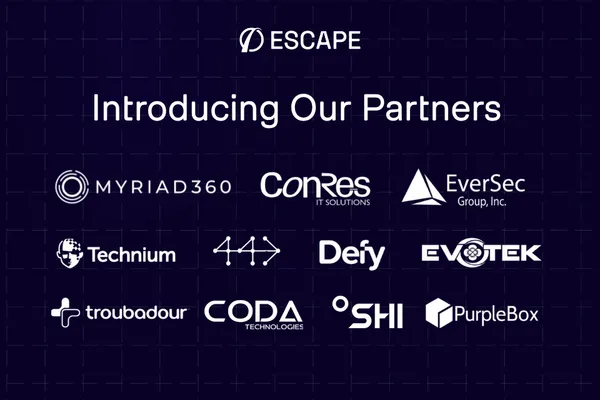
Escape's Channel Partners: ConRes, Myriad360, EverSec, Technium, and more
Announcement

Introducing Escape's Channel Partners

After announcing our channel partner program last month, we are excited to now be working with eleven incredible partners, with more soon to join us! Escape's Channel Partner Program is built on a simple principle: a two-way relationship centered on the shared goal of helping security teams do
Sanjana Iyer
Sanjana Iyer
5 min read
Automated Penetration Testing: The Complete Guide in 2026
Offensive Security

Automated Penetration Testing: The Complete Guide in 2026

Discover a guide to what automated penetration testing is, how it works, and best practices when looking for a vendor and implementing automated pentesting.
Sanjana Iyer
Sanjana Iyer
14 min read
Top continuous penetration testing tools with expert review
AI pentesting

7 best continuous penetration testing tools in 2026

Continuous penetration testing tools close the gap in coverage left by annual pentests. This guide breaks down the best options, what each tool actually does, and how to choose.
Sanjana Iyer
Sanjana Iyer
21 min read
How Escape DAST helped Sigma Computing achieve complete GraphQL API endpoint coverage
Case Study

How Escape DAST helped Sigma Computing achieve complete GraphQL API endpoint coverage

Sigma Computing needed GraphQL-native DAST, not a REST crawler with GraphQL bolted on. Here's how they got full endpoint coverage and slashed their triage time with Escape.
Sanjana Iyer
Sanjana Iyer
9 min read
AI pentesting, Mission log: July
Product updates

AI pentesting, Mission log: July

What we shipped in AI pentesting this month.
Sanjana Iyer
Alexandra Charikova
Sanjana Iyer, Alexandra Charikova
6 min read
Best GraphQL security tools list
Application Security

Best GraphQL security tools in 2026: An in-depth guide, including business logic and enterprise coverage

Discover a practical guide to GraphQL security tools, an in-depth comparison, and how to choose the right ones for your stack.
Sanjana Iyer
Alexandra Charikova
Sanjana Iyer, Alexandra Charikova
24 min read
Introducing Escape's Partner Program
Announcement

Introducing Escape's Partner Program

Join Escape's partner program to build offensive security into every stack, together.
Sanjana Iyer
Sanjana Iyer
3 min read
Race against the Machine: Can you match AI's pentesting time?
Pentesting

Race against the Machine: Can you match AI's pentesting time?

Race our AI in a series of pentesting challenges to try and beat its time.
Gwendal Mognier
Sanjana Iyer
Gwendal Mognier, Sanjana Iyer
3 min read
Claude in Security Engineering: From Proof-of-Concept to Production
Webinar recap

Claude in Security Engineering: From Proof-of-Concept to Production

Senior Security Engineer Geet Pradhan and Escape CEO Tristan Kalos run through how to use Claude to automate security engineering through threat modeling, detection engineering, and incident response
Sanjana Iyer
Sanjana Iyer
15 min read
How DAST helps meet Cyber Resilience Act compliance requirements
Compliance

Why DAST Is Critical for Cyber Resilience Act Compliance

The EU’s Cyber Resilience Act is reshaping how companies build and secure digital products. Learn why modern DAST is critical for CRA compliance from secure development to incident response and how to prepare before the 2027 deadline.
Sanjana Iyer
Sanjana Iyer
10 min read
How Escape Enabled Deeper Business Logic Testing for Arkose Labs
Case Study

How Escape Enabled Deeper Business Logic Testing for Arkose Labs

Arkose Labs is a global cybersecurity company that specializes in account security, including bot management, device ID, anti-phishing and email intelligence. Its unified platform helps the world’s biggest enterprises across industries, including banking, gaming, e-commerce and social media, protect user accounts and digital ecosystems from malicious automation, credential stuffing
Alexandra Charikova
Sanjana Iyer
Alexandra Charikova, Sanjana Iyer
4 min read
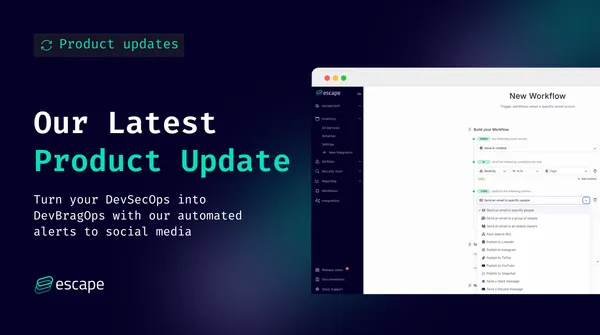
Product Update: Automate alerts to your social media
Product updates

Product Update: Automate alerts to your social media

Escape has created the first ever push-to-post automation to revolutionize vulnerability management by giving you the recognition you deserve.
Sanjana Iyer
Sanjana Iyer
3 min read
How to maintain security compliance at a Fintech: A complete guide
Compliance

How to maintain security compliance at a Fintech: A complete guide

If you're responsible for security at a financial services or fintech company, here is your comprehensive overview of what you need to do to be compliant.
Sanjana Iyer
Sanjana Iyer
12 min read
Spring 2025 Events Spotlight
Announcement

Spring 2025 Events Spotlight

Discover all of the exciting events you can find us at this March and April!
Sanjana Iyer
Sanjana Iyer
5 min read
Webinar recap: The security mistakes everyone makes in M&A
Webinar recap

Webinar recap: The security mistakes everyone makes in M&A

Discover exactly how to avoid the common security pitfalls during M&A from our panel of experts, who are drawing from decades of experience in the field.
Sanjana Iyer
Sanjana Iyer
10 min read
Webinar recap: How to combine SAST and DAST for complete application coverage
Webinar recap

Webinar recap: How to combine SAST and DAST for complete application coverage

Modern applications come with a whole host of challenges that legacy SASTs and DASTs simply cannot keep up with. If you want to be sure no vulnerabilities slip through the cracks in these applications, the key is combining a modern SAST and DAST. Why? Last week, Escape’s CEO Tristan
Sanjana Iyer
Sanjana Iyer
16 min read
Webinar cover on combining SAST and DAST for complete application security coverage
Webinar

Webinar: How to combine SAST and DAST for complete application coverage

Join experts Amit Bismut and Tristan Kalos as they give you actionable insights and practical examples on how to harness SAST and DAST together to create a robust security strategy.
Sanjana Iyer
Sanjana Iyer
1 min read
The Elephant in AppSec Talks Highlight: Shifting Left Doesn't Mean Anything Anymore
The Elephant in AppSec

The Elephant in AppSec Talks Highlight: Shifting Left Doesn't Mean Anything Anymore

Discover key highlights from Tanya Janca's talk at The Elephant in AppSec Conference on shifting security to be present throughout the entire Software Development Lifecycle.
Sanjana Iyer
Sanjana Iyer
5 min read
The Elephant in AppSec Conference Panel Highlight: Why scaling AppSec is harder than you think
Application Security

The Elephant in AppSec Conference Panel Highlight: Why scaling AppSec is harder than you think

Key takeaways from highly experienced industry experts on how to scale application security from the panel in Track 1 of The Elephant in AppSec Conference.
Sanjana Iyer
Sanjana Iyer
5 min read
The Elephant in AppSec Talks Highlight: Reinventing API Security
API Security

The Elephant in AppSec Talks Highlight: Reinventing API Security

Highlights from Escape's talks at The Elephant in AppSec Conference on the challenges of API security and how Escape is overcoming these
Sanjana Iyer
Sanjana Iyer
6 min read
The Elephant in AppSec Conference: 4 Key Takeaways
The Elephant in AppSec

The Elephant in AppSec Conference: 4 Key Takeaways

Here are the key takeaways from the Elephant in AppSec Conference, uncovering the top insights from industry experts in application security.
Sanjana Iyer
Sanjana Iyer
6 min read