Geoffrey Diederichs — Last Publications
Research
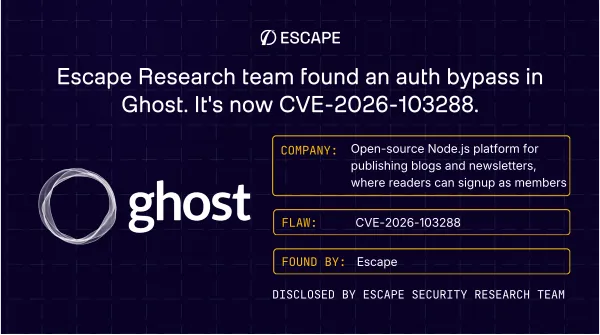
Escape research found an auth bypass in Ghost that can wipe all member's votes. It's now CVE-2026-103288.
Escape's research team found two stacked flaws that led to an auth bypass enabling any member to delete all members' likes on comments. It's now CVE-2026-103288, found only by testing as multiple low-auth users to see what they could do with data they shouldn't have access to.
10 min read
Offensive Security
Escape found the same XSS in two AI chatboxes. The vulnerability was in the Markdown renderer.
Weeks apart, at two unrelated companies, Escape's AI pentesting agent found the same stored XSS. Both had shipped a customer-facing chat where the model emits Markdown and the frontend renders it with raw HTML enabled and no sanitizer, so anything the model can be made to say executes
8 min read
Escape Blog Squad
-
 Alexandra Charikova
158 articles
-
 Antoine Carossio
40 articles
-
 Tristan Kalos
25 articles
-
 Sanjana Iyer
24 articles
-
 Achraf Ait Sidi Hammou
17 articles
-
 Gautier Ben Aïm
12 articles
-
 Escape - Offensive Security
11 articles
-
 Maxence Lecanu
8 articles
-
 Karim Rustom
8 articles
-
 Nohé Hinniger-Foray
8 articles
-
 Gwendal Mognier
8 articles
-
 Alexandre Tang
7 articles