Offensive Security
12 posts
Offensive Security
Escape found the same XSS in two AI chatboxes. The vulnerability was in the Markdown renderer.
Weeks apart, at two unrelated companies, Escape's AI pentesting agent found the same stored XSS. Both had shipped a customer-facing chat where the model emits Markdown and the frontend renders it with raw HTML enabled and no sanitizer, so anything the model can be made to say executes
8 min read
Offensive Security
Horizon3.ai alternatives in 2026: Escape vs NodeZero and 4 more tools
Escape is the best Horizon3.ai alternative for continuous AI pentesting across APIs, web apps, and complex authentication, including regression testing, developer-ready remediation, and platform pricing suited for rapidly scaling orgs.
21 min read
Offensive Security
Escape vs Pentera: how each one proves exploitability (2026)
Most teams arrive at this comparison with the wrong framing: two automated penetration testing platforms, pick one.
Start with what Pentera actually is, because the comparisons that skip this get everything after it wrong. Pentera is an exposure validation platform with a key focus on network testing, and a good
14 min read
Offensive Security
Pentera Alternatives for Continuous Pentesting: 7 Competitors Compared In-Depth
Most security and IT teams we talk to who are evaluating Pentera alternatives are mostly happy with what Pentera does. What changed is the shape of the problem underneath them. It used to be a network problem. Now it is also a web application problem, and the tool hasn'
21 min read
Offensive Security
Continuous penetration testing: what it means when the testing never stops
In late 2025, Anthropic disclosed the first documented cyberattack run largely by AI, a state-linked group that used Claude Code to run 80 to 90 percent of an espionage campaign on its own, at thousands of requests a second.
Offense now moves at machine speed while most defenses stay scheduled
10 min read
Offensive Security
Penetration testing as a service (PTaaS), explained
Penetration testing as a service (PTaaS) made buying a pentest almost frictionless. You scope it in a portal, watch findings land on a live dashboard, and click a button to retest the fix, all without a single procurement call. But the test still runs on a schedule, so weeks after
10 min read
Product updates
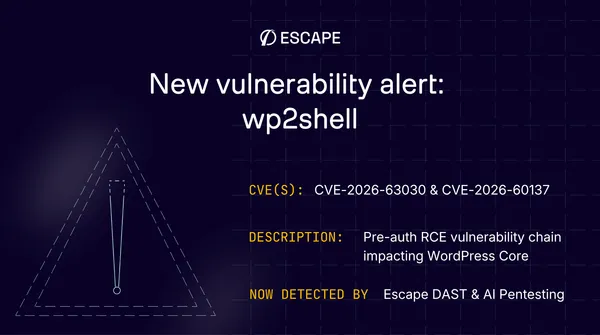
wp2shell (CVE-2026-63030 + CVE-2026-60137): WordPress pre-auth RCE, now detected by Escape
wp2shell is an unauthenticated RCE chain in WordPress core. It combines two separate vulnerabilities: CVE-2026-63030 and CVE-2026-60137. Escape detects it across DAST and AI Pentesting, confirms exploitability, and shows affected assets within its Attack Surface Management.
7 min read
Agentic Pentesting
How Escape AI Pentesting Exploited SSRF in LiteLLM
At Escape, we routinely test the AI infrastructure that teams deploy inside their cloud environments.
LLM gateways, RAG pipelines, model proxies: these are services that make outbound HTTP requests by design, which makes them natural targets for SSRF.
When we looked at LiteLLM, we found three confirmed SSRF sinks, a
9 min read