Events
13 posts
Webinar
[Webinar] Doing More With Less: How Security Teams Escape Manual Work with Efficient Workflows
Security teams are under constant pressure to do more with the same resources. Manual processes, fragmented tools, and inefficient workflows can slow teams down and pull focus away from what matters most.
In this live webinar, experienced security practitioners share how they’ve escaped the constraints of limited resources by
1 min read
Application Security
Two Major Updates from The Elephant in AppSec Conference: Agenda Is Live & Partnership with InfoSecMap
Two exciting updates in the Elephant in AppSec corner!
1. The Elephant in AppSec Conference 2026 Agenda Is Now Live
The agenda for the 2026 edition of The Elephant in AppSec Conference is officially published. This year’s program brings together a lineup of speakers who aren’t afraid to
3 min read
Application Security
[Webinar] From Business Logic Vulnerabilities to Actionable Insights: AI-powered Pentesting + ASM in Action
For years, security teams have relied on human penetration testers to uncover critical vulnerabilities hidden in complex business logic. These flaws are subtle, context-dependent, and unique to every system’s workflow. Even modern scanners struggle to capture them, focusing only on a limited range of vulnerabilities displayed in their UI.
2 min read
Application Security
Feedback From Escape Customers: Securing AI-Driven Applications with DAST
“You ask the developer why they wrote the code the way that they did, and they don’t have an answer anymore. They’re like, ‘Well, AI wrote it.” - Seth Kirschner, DoubleVerify
AI is now deeply embedded in software development workflows, and the implications for application security teams are
11 min read
Webinar
Webinar: The security mistakes everyone makes in M&A
If you often manage security across diverse brands or handle mergers and acquisitions, this webinar is not to be missed, as a panel of guest experts take you through all of the real-world security pitfalls when bringing companies together.
2 min read
API Security
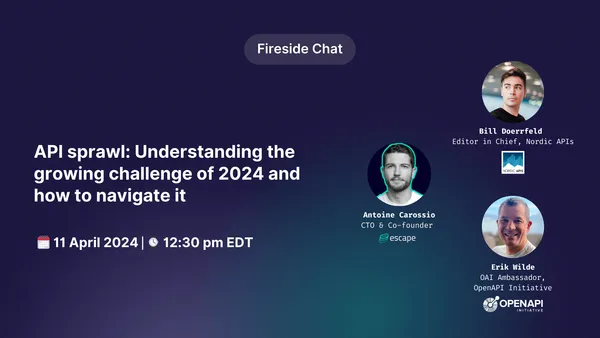
[Fireside Chat] API sprawl: Understanding the growing challenge of 2024 and how to navigate it
Hey there 👋
Join Bill Doerrfeld, tech journalist and Editor-in-Chief at the Nordic APIs blog, Erik Wilde, OAI Ambassador at the OpenAPI Initiative, and Antoine Carossio, CTO and co-founder at Escape, for a fireside chat on the challenges of API sprawl.
Sign me up!
During this live discussion, they will explore:
1 min read
API Security
Workshop "How to write custom security tests" - Main Takeaways
Organizations are constantly seeking ways to improve their defenses against business logic vulnerabilities. These vulnerabilities, often difficult to detect, can lead to significant security breaches if left unchecked. To address this challenge, we've introduced a new feature within our platform that empowers teams to create custom business logic
5 min read
Events
Webinar: Building Your Product Security Roadmap
Whether you're in the first few weeks of your ProdSec journey or building your Product security program for 2024, you might feel lost trying to wrap your head around all the attack surface your org faces and identifying some of the biggest security gaps. Don't worry,
1 min read