Compliance
7 posts
Compliance
Why DAST Is Critical for Cyber Resilience Act Compliance
The EU’s Cyber Resilience Act is reshaping how companies build and secure digital products. Learn why modern DAST is critical for CRA compliance from secure development to incident response and how to prepare before the 2027 deadline.
10 min read
Compliance
How API Security Fits into DORA Compliance: Everything You Need to Know
With over 22,000 financial institutions and IT service providers now affected, the Digital Operational Resilience Act (DORA) represents an important shift in cybersecurity for the EU’s financial sector.
DORA forces tighter collaboration between regulators, financial institutions, and third-party vendors. It’s not just about protecting internal systems anymore
7 min read
Product updates
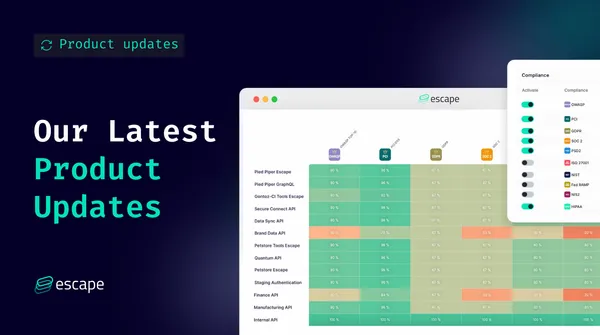
Our Latest Product Updates
We’re constantly improving our product for our customers. See the latest features, improvements, and fixes we have shipped over the past month.
Customize your compliance view
Last month we shipped a new feature designed to enhance your compliance management experience. It allows you to hide irrelevant compliance frameworks from
5 min read
GraphQL
Introducing Seamless GraphQL Compliance
As your go-to partner in GraphQL Security, we at Escape are constantly innovating to simplify and streamline security for you. We're proud of our reputation for crafting modern, dynamic application security testing (DAST) tools tailored to GraphQL, beloved by developers and trusted by security teams worldwide. From comprehensive
3 min read