Platform
Solution
Company
Resources
Escape Platform
Replace legacy scanners and manual offensive security processes with AI agents that discover, test, and remediate directly in your engineering workflows.
AI in Escape
Leverage our in-house, AI-powered DAST to secure your applications at the business logic level
Research
Escape rebuilds offensive and application security from the ground up: business logic testing, agentic pentesting, code-to-cloud correlation. Always developed in-house.
Products
AI Pentesting
Run continuous AI-powered pentesting that learns your business, proves exploitability, and delivers reports that auditors and engineers can act on.
Business-logic-aware DAST
External network pentesting
Continuous testing of everything reachable from the internet. Every host, port, and exposed service is probed the way an attacker would, with proof of what's exploitable, followed by a retest.
Attack Surface Management
Discover and validate exposure of modern applications, APIs, and infrastructure from code to cloud.
News
By use case
Use case one
Use case two
Use case three
By industry
Industry one
Industry two
About us
Learn about our story
Partners
For the partners who give outnumbered security teams an unfair advantage
Careers
Join us on our mission!
Blog
Explore offensive and application security insights
Customer stories
Learn what our customers achieve with Escape
Documentation
We're here to help you
The Elephant in AppSec Podcast
Listen to other practitioners’ stories
Pentester vs. AI challenges
Can you beat the machine?
Events
Discover our upcoming events across the world
Security Research
Modern AI-powered Pentesting Tools Benchmark
Where the only variable is harness.
Escape Research team found a PII disclosure in Keycloak
It's now CVE-2026-17059.
Escape found the same XSS in two AI chatboxes
The vulnerability was in the Markdown renderer.
State of GraphQL Security 2024
The State of Security of Vibe Coded Apps
How we discovered over 2k high-impact vulnerabilities in apps built with vibe coding platforms
Tools
GraphQL Security
GraphQL Armor
Featured
How Amp got its SOC 2 type II pentest evidence in hours
Compliance was in the product from day one, which meant a pentest in year one. Here is how they scoped it, ran it in hours with Escape, and made sure they're ready for their SOC 2 Type II audit.
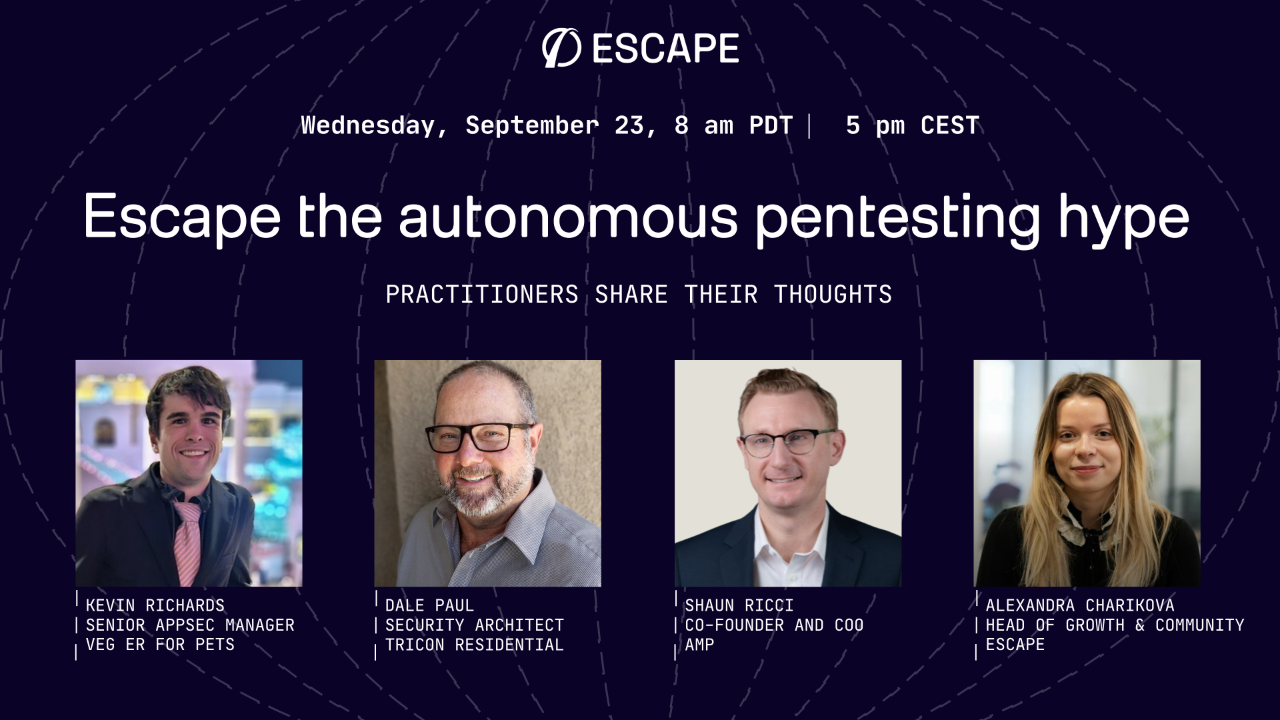
Escape the autonomous pentesting hype
Practitioners share their thoughts